AI cybersecurity researchers uncovered VOLTA-AUTODOXER malware that steals your data and uses AI to profile victims. Get cybersecurity tips to stay protected.
Sem86 is an x86 full-system emulator that loads instruction behavior from a file at runtime, so undefined or undocumented instructions can be changed by editing the file.…
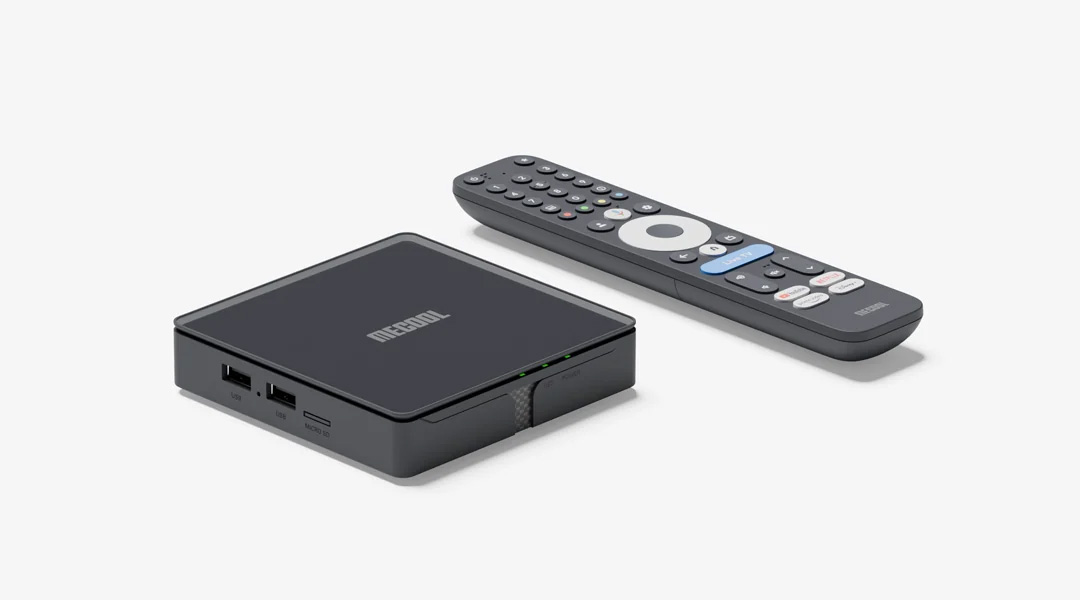
The backdoor was discovered in the firmware of multiple Videostrong devices, such as the Mecool KTI, as well as several white-label Android TV boxes. Seattle-based cybersecurity and...
We measured what open package-malware feeds flag on npm and PyPI, what the registries did, how many flags left up are wrong, and what open scanners cost in false alarms.
Malware infecting Android devices isn’t new, but Google’s recent report is grim and concerning. The search giant has taken down a massive botnet that turned over 1.3 million Android TV set-top boxes into tools for cybercriminals.…
New AI-driven Windows malware feeds stolen data to Claude to rank victims’ assets by value, then deletes itself — payload builds custom target assessment, can switch models if one refuses, or skip the AI step entirely
While major data breaches have previously been traced to login credentials stolen by infostealer malware, the integration of mainstream LLMs give such established threats a new edge.
Zeus, Emotet and Qakbot infected millions of computers by looking harmless. Then police did something wild — they used the botnets' own channels to remove the malware. A plain guide to trojans and the biggest botnet takedowns.
If you’ve downloaded a PS5 emulator from GitHub, it’s worth double-checking what you installed. According to a report from Engadget, NordVPN’s Threat Intelligence team found fake GitHub projects posing as two PS5 emulators, KytyPS5 and AnyPS5.…