Key takeaways
Government APIs are prime targets for nation-states and advanced threat actors that are seeking long-term access to permanent personally identifiable information (PII) rather than transient financial data.
Legacy debt and high availability demands make securing public sector endpoints unique — agencies must wrap modern APIs around legacy back ends without taking critical civic services offline.
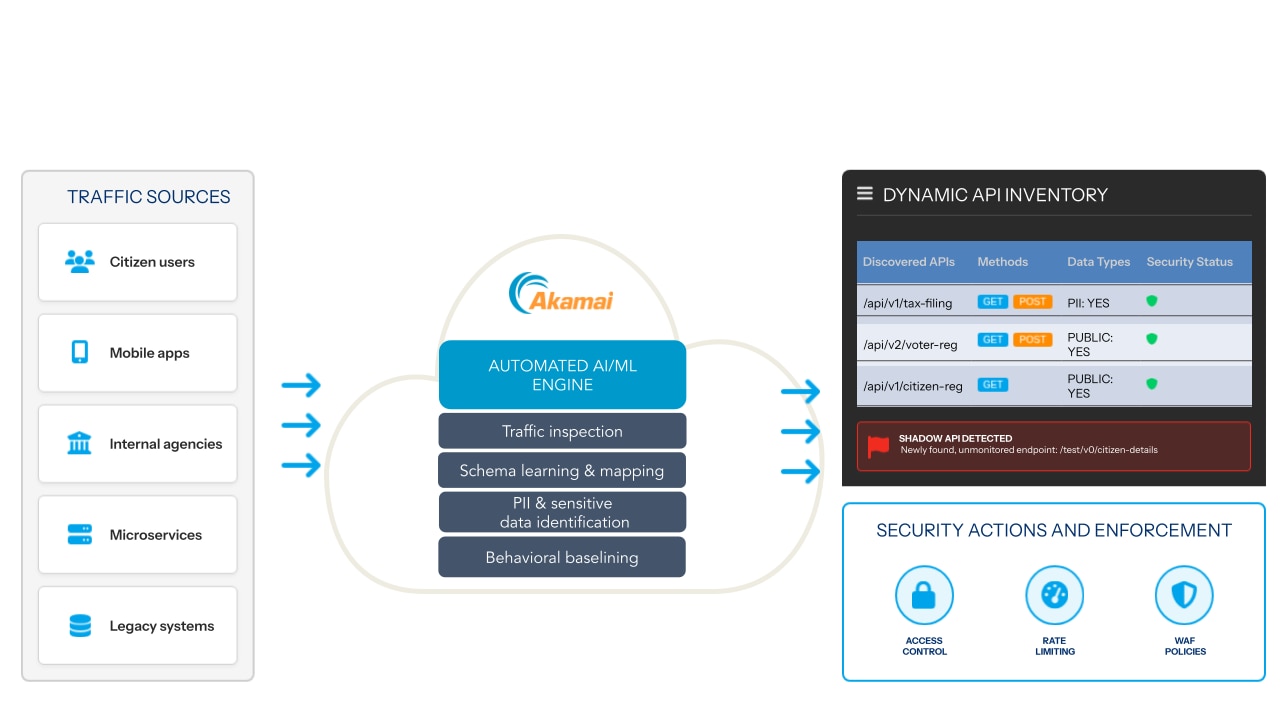
Traditional firewalls miss modern API threats like Broken Object Level Authorization (BOLA) , business logic abuse, and untracked “shadow” or “zombie” APIs, which mimic legitimate user activity at scale.
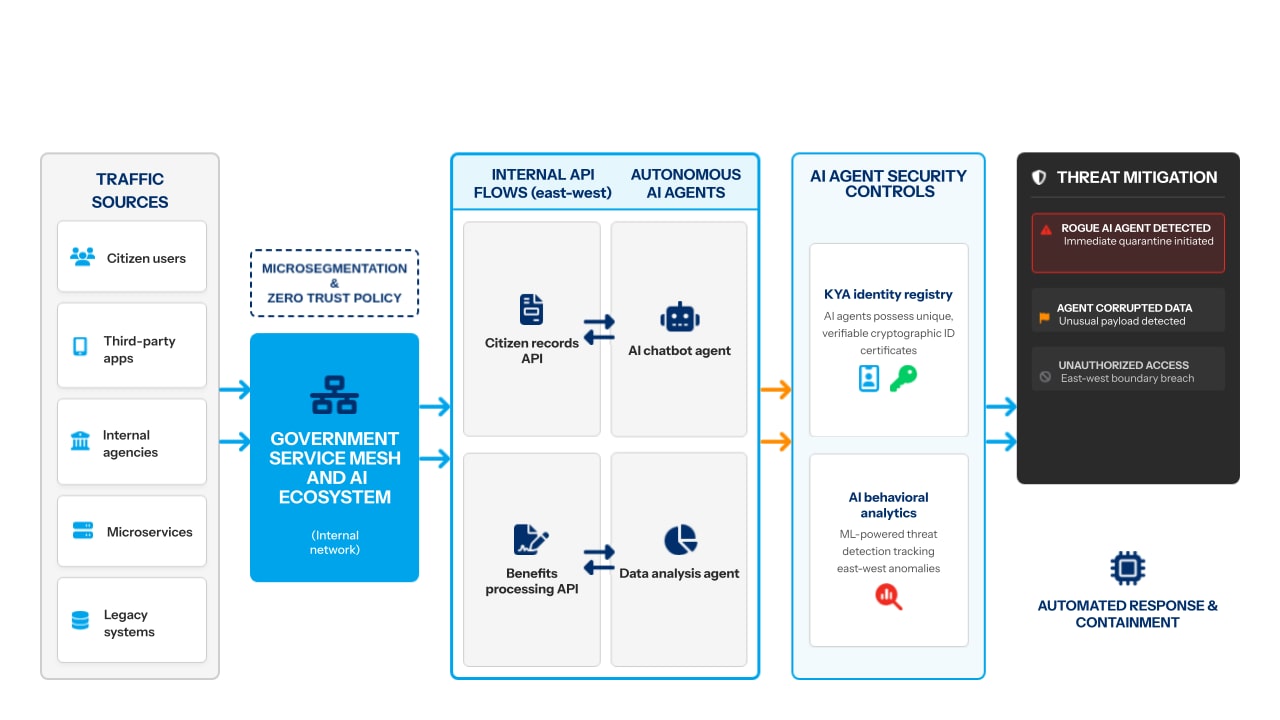
Security visibility must expand to “detect shadow everything ” — including emerging AI agents, Model Context Protocol (MCP) servers, and internal service-to-service (east-west) traffic.
Comprehensive API defense requires continuous automated discovery, strict Zero Trust architecture (e.g., sender-constrained tokens, Know Your Agent policies), AI-driven behavioral analytics, and shift-left security…