Blog
Security
Stopping Active Attacks with Penalty Box
Ryan Barnett is a Principal Security Researcher working on the Akamai Threat Research Team supporting App and API Protector security solutions. In addition to his primary work at Akamai, he is also a WASC Board Member and OWASP Project Leader for: Web Hacking Incident Database (WHID) and Distributed Web Honeypots. Mr. Barnett is a frequent speaker at security industry conferences such as Black Hat and has authored two web security books: Preventing Web Attacks with Apache (Pearson) and The Web Application Defender's Cookbook: Battling Hackers and Defending Users (Wiley).
A web application firewall (WAF) is most often used by organizations for external security controls to detect and block individual attack attempts against target web application assets.
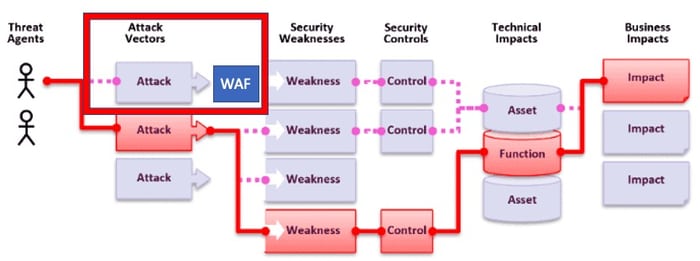
Open Web Application Security Project (OWASP) risk rating methodology
Unfortunately, today's sophisticated web application threats have gained some advantages over typical WAFs:
\r\n \r\n Favorable…