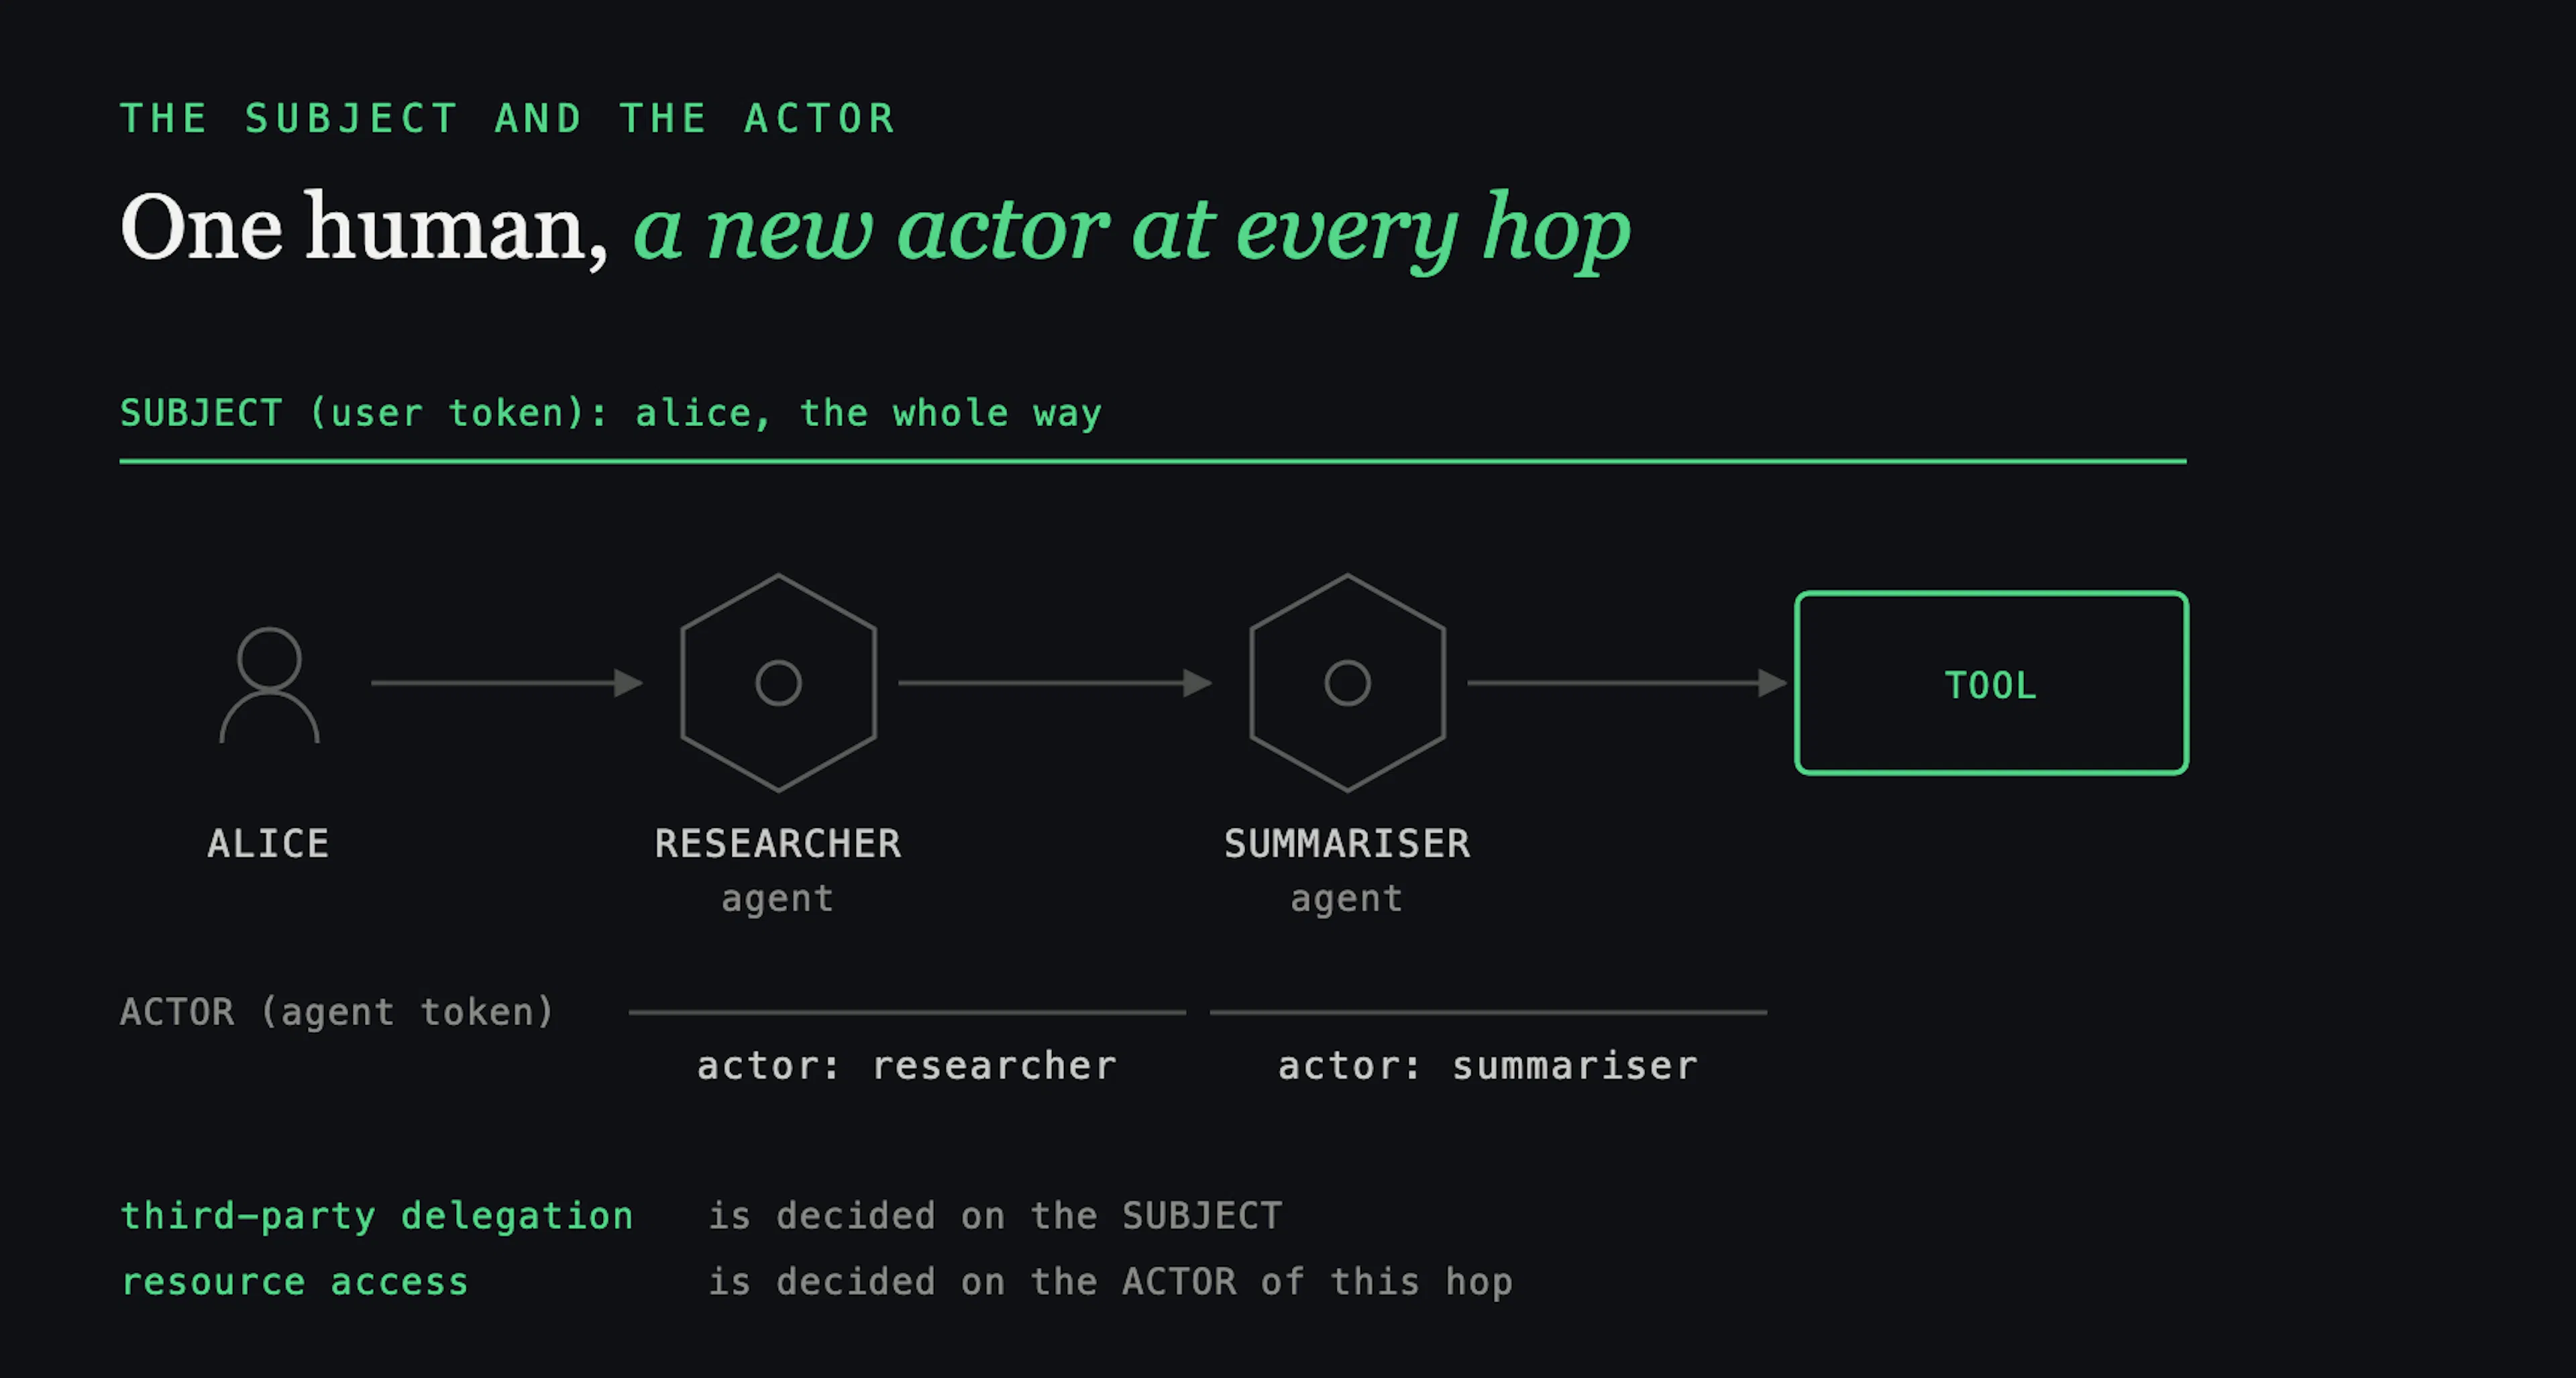
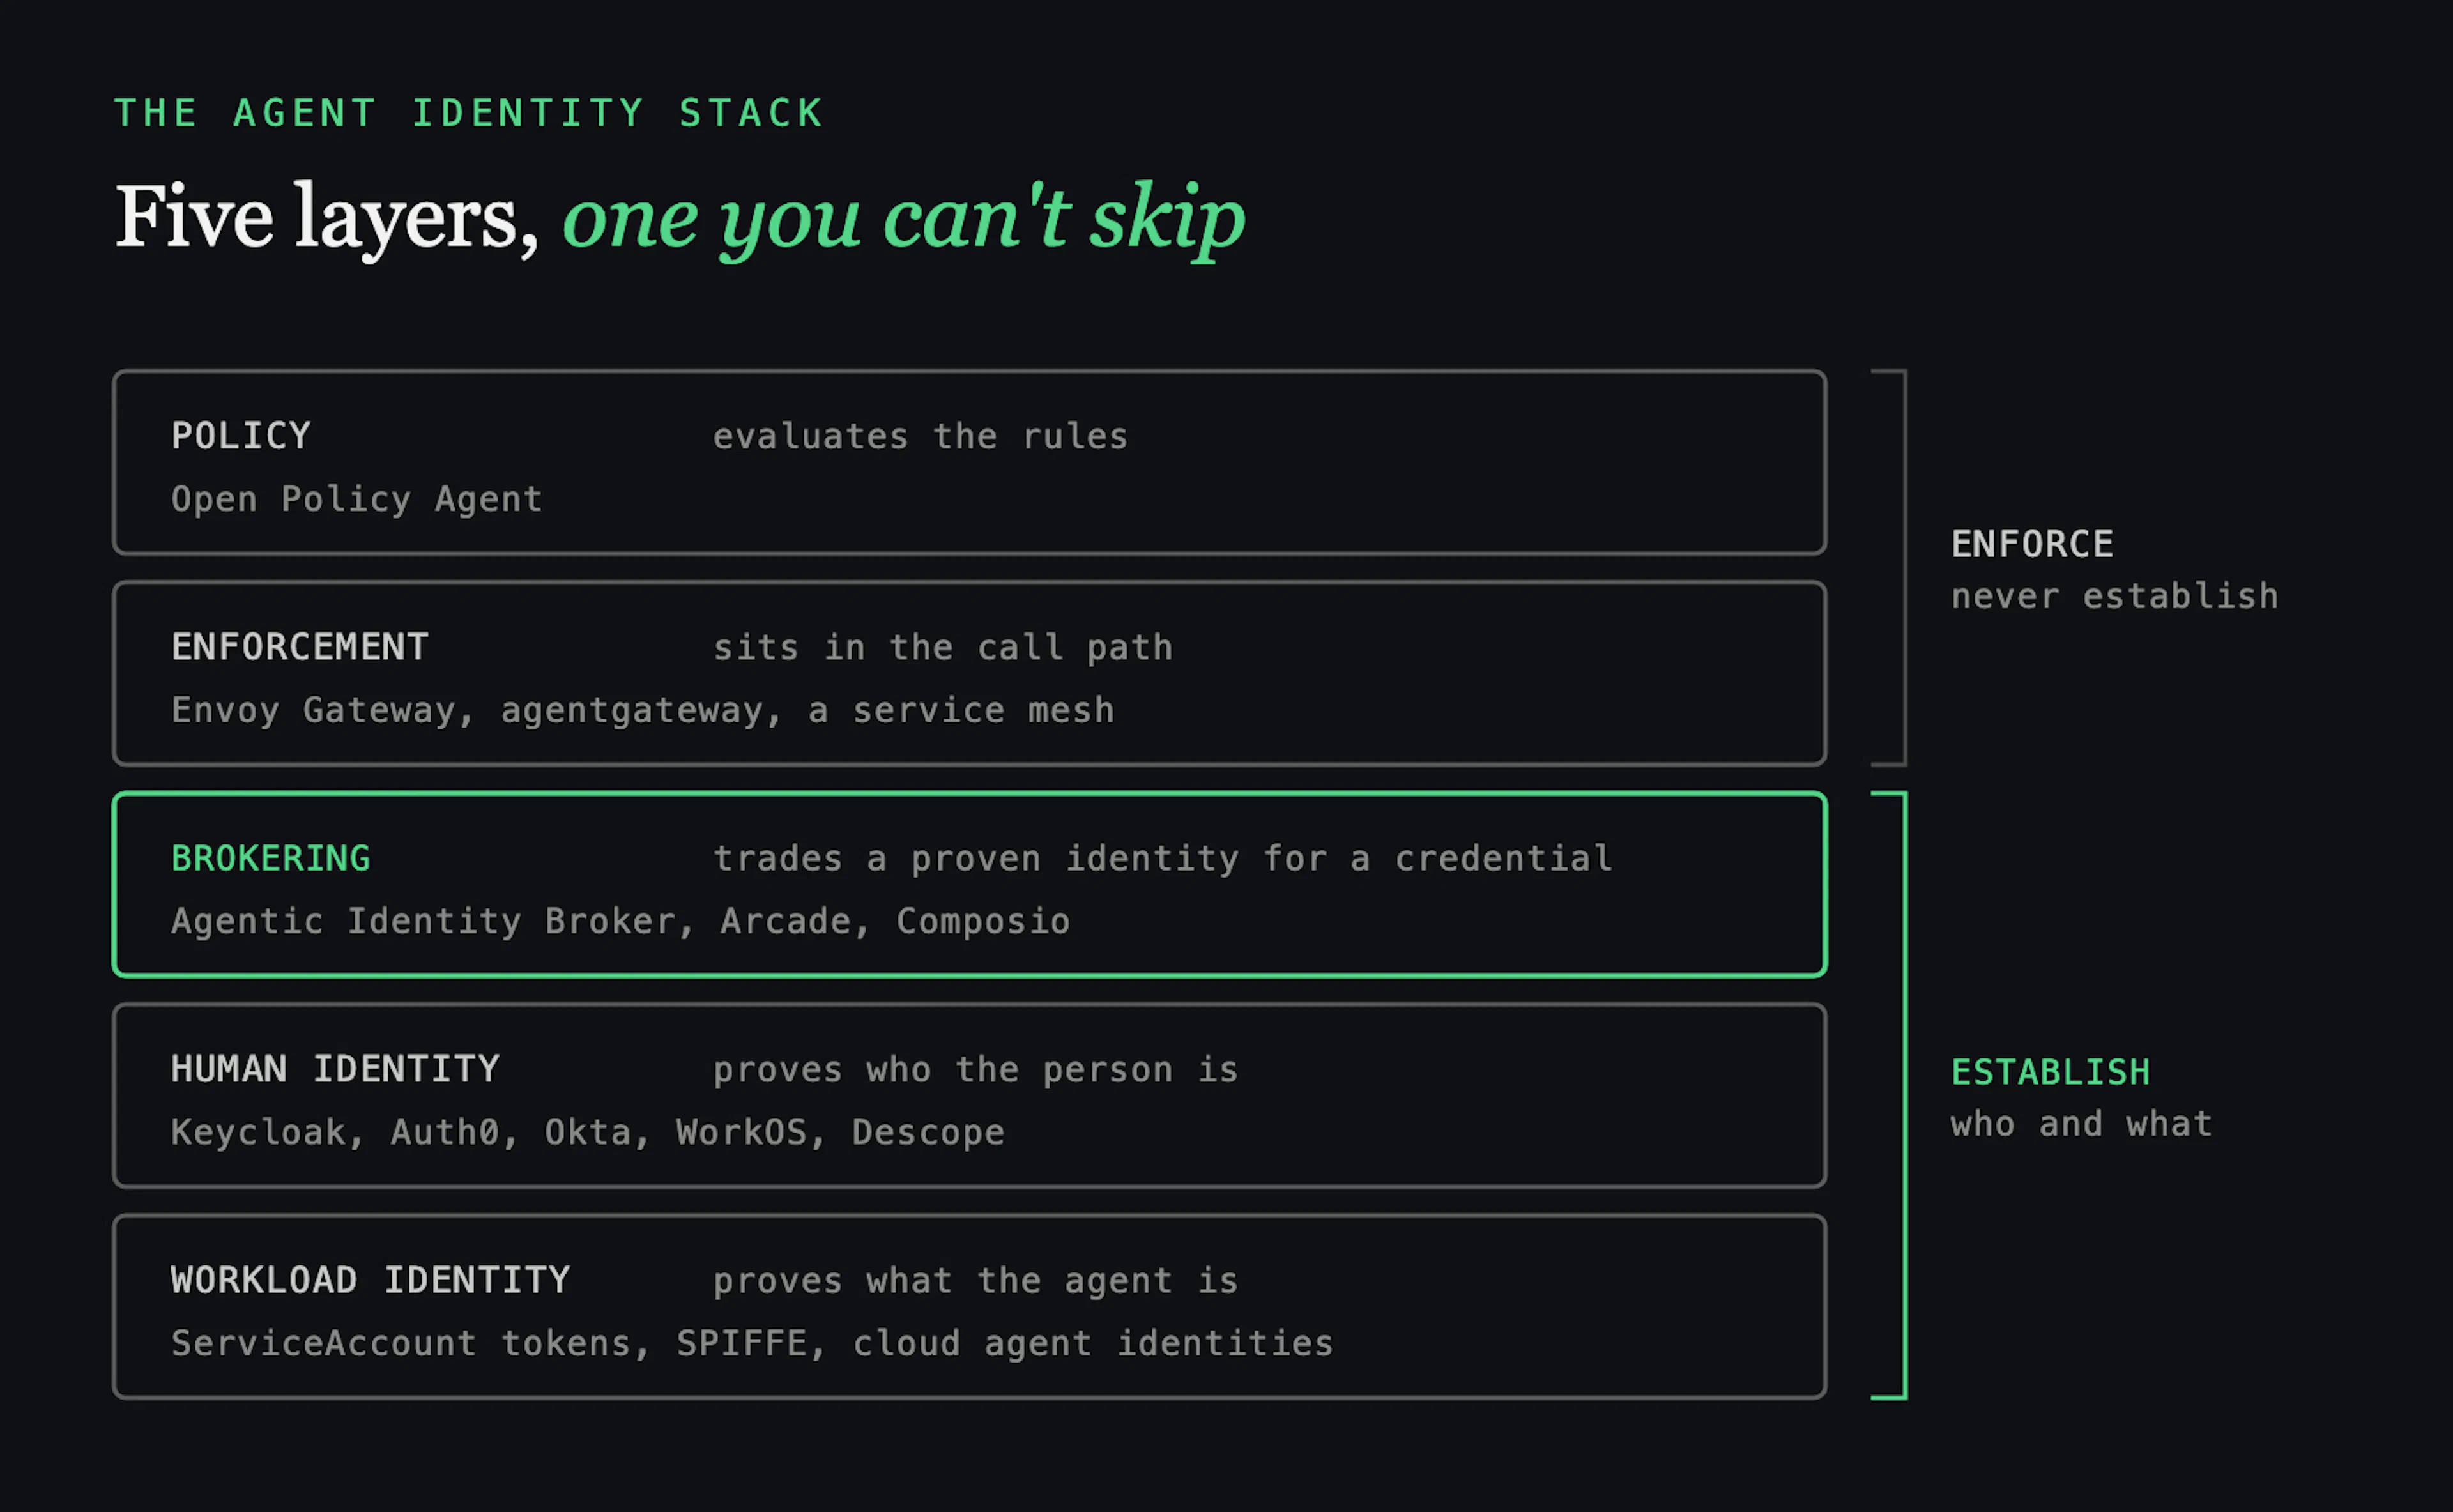
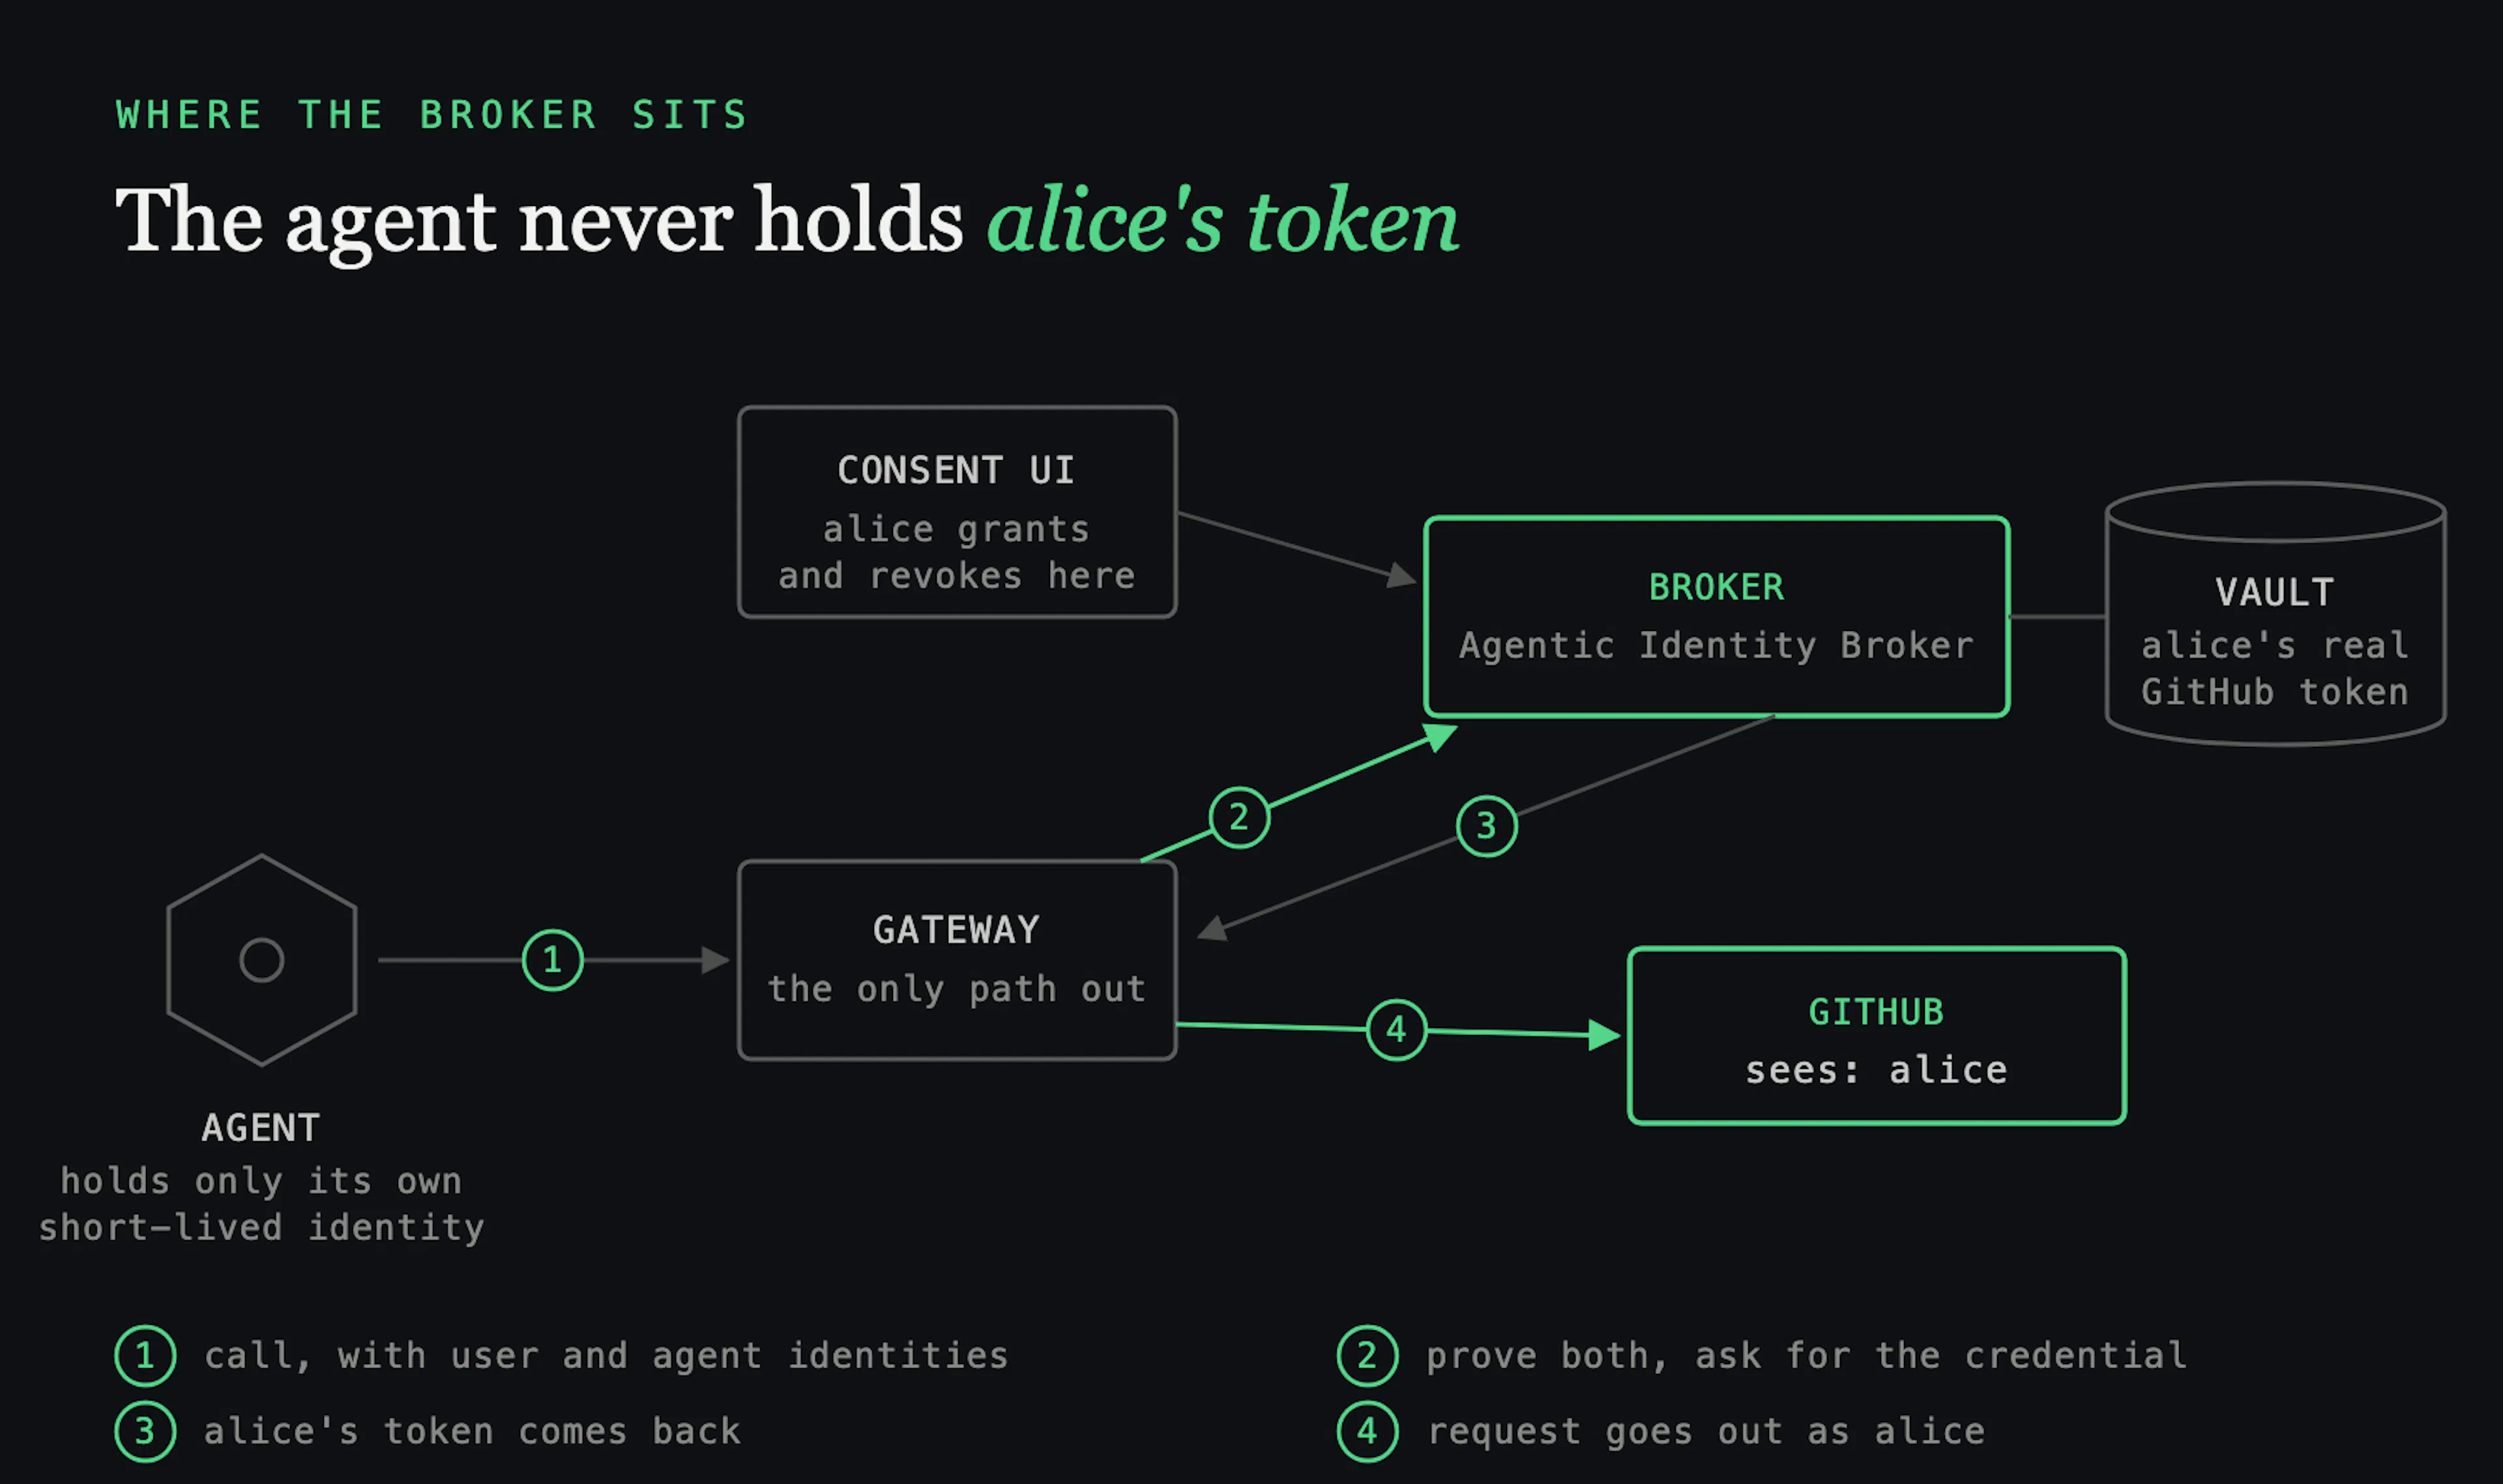
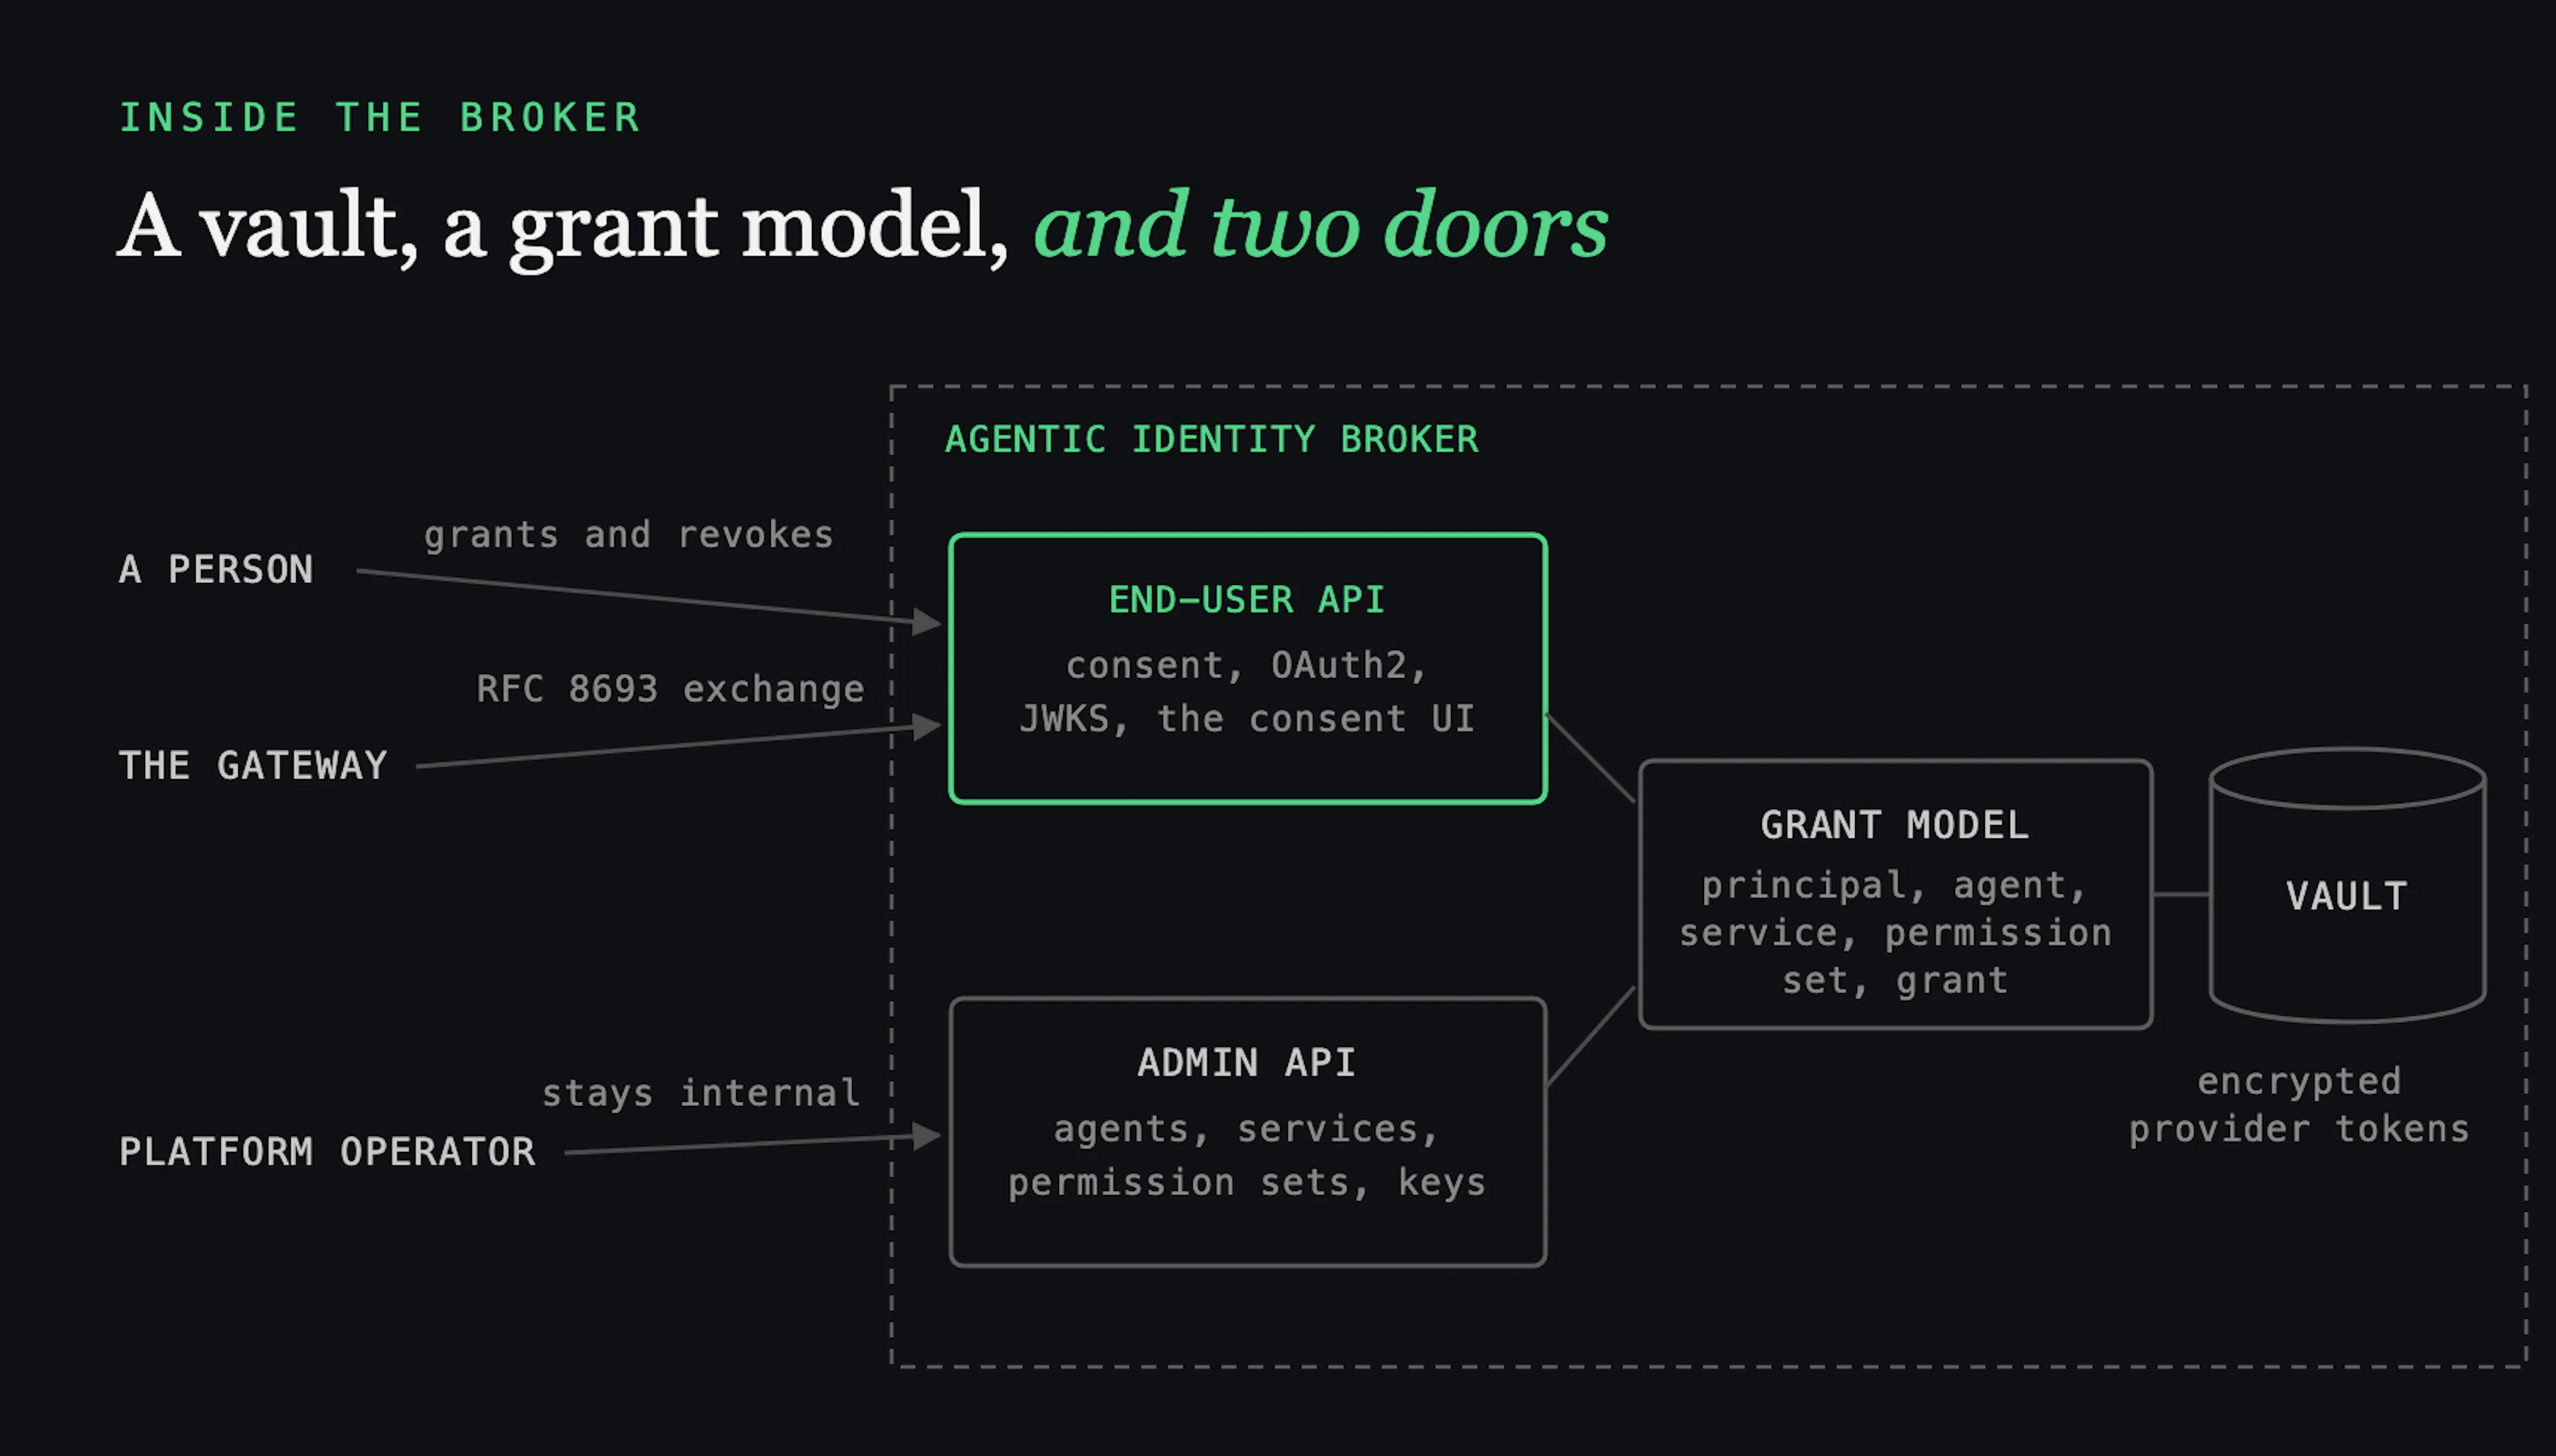
This is a 2-part series on agent identity and security: who the user is, who the agent is, and what each of them should be allowed to reach. Part 1 covers the delegation problem, the standards to build on, and the Agentic Identity Broker that Zalando has just open sourced.
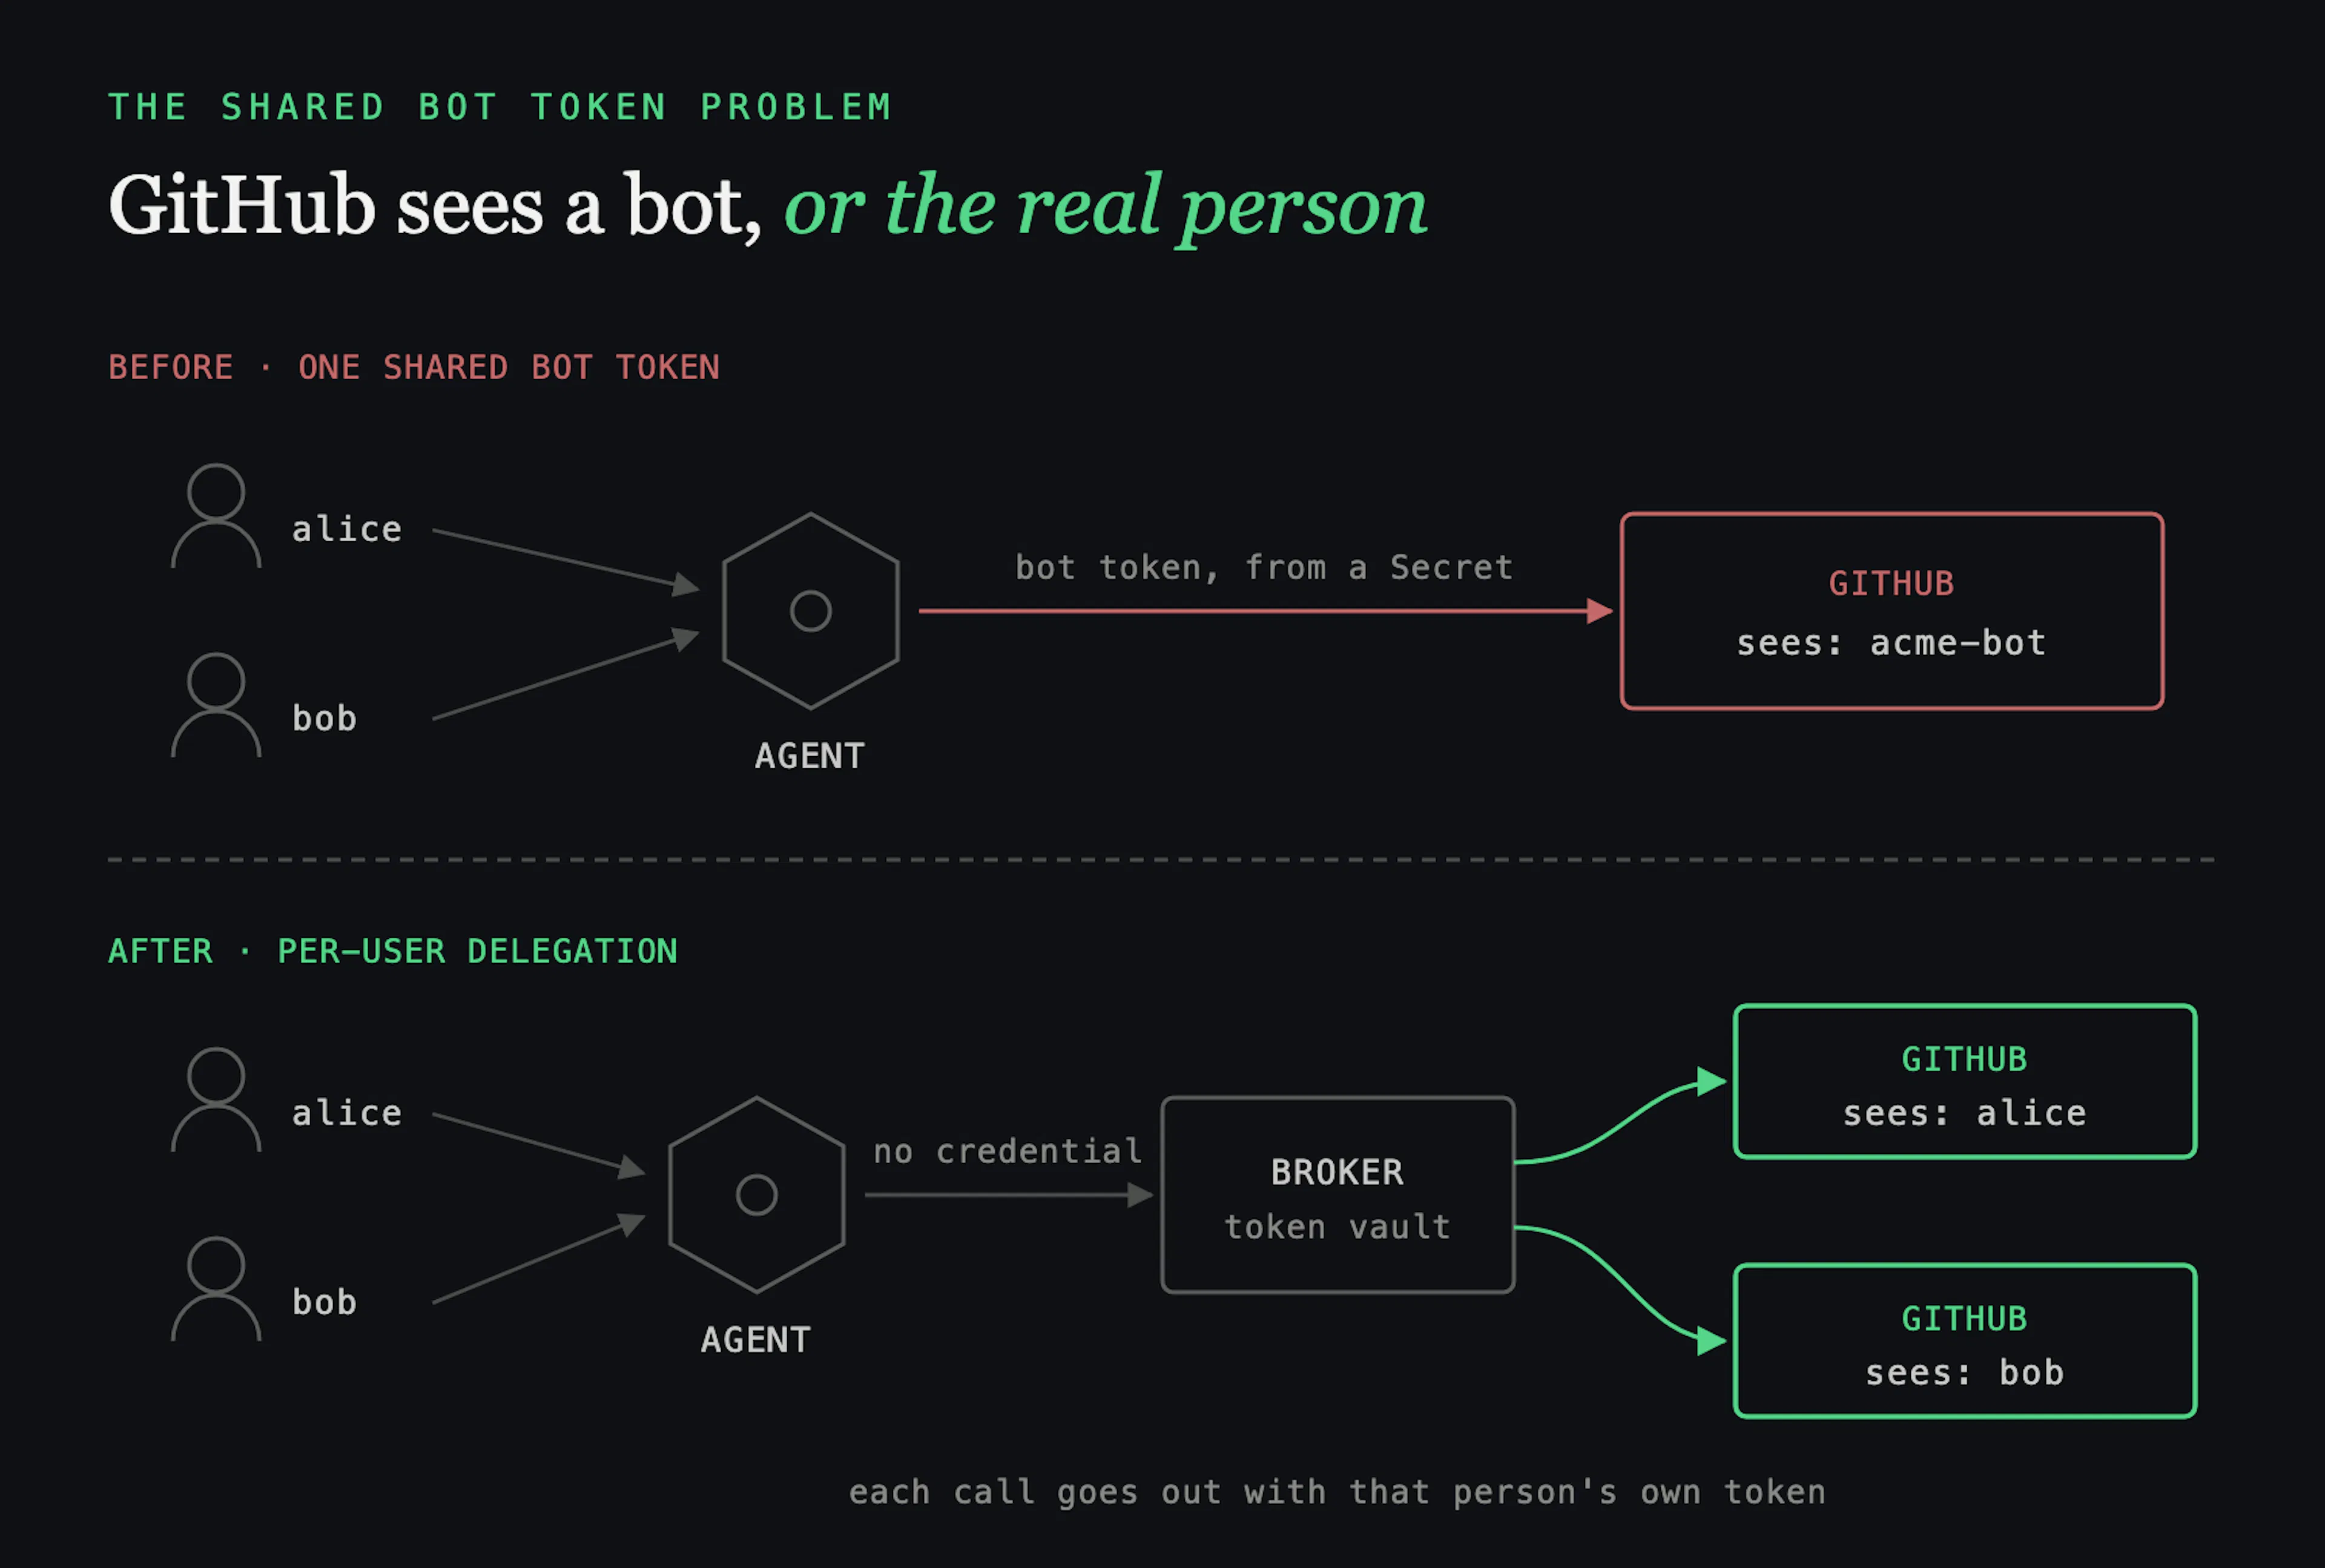
The first time I wired one of my agents up to GitHub I did the thing everyone does. I created a bot account, put its token in a Kubernetes Secret, and let every user's request ride on it.
It wasn't a deliberate design decision, it was just the quickest way to get the demo working, and it held up right until a second person tried to use the agent. GitHub saw one identity for all of us, so I couldn't tell whose request was whose. If I'd wanted to cut one person off, the only lever I had was rotating a credential that everybody else depended on.…