Secure your dependencies with us
Socket proactively blocks malicious open source packages in your code.
Install
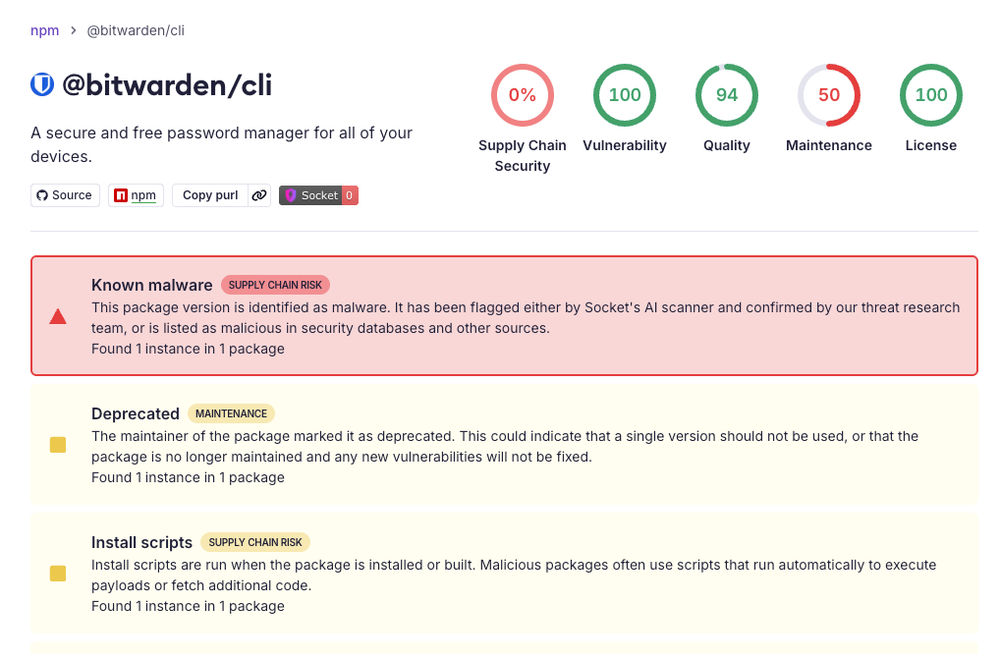
Socket researchers discovered that the Bitwarden CLI was compromised as part of the ongoing Checkmarx supply chain campaign . The open source password manager serves more than 10 million users and over 50,000 businesses, and ranks among among the top three password managers by enterprise adoption.
The affected package version appears to be @bitwarden/cli2026.4.0 , and the malicious code was published in bw1.js , a file included in the package contents. The attack appears to have leveraged a compromised GitHub Action in Bitwarden’s CI/CD pipeline, consistent with the pattern seen across other affected repositories in this campaign.
What we know so far:
Bitwarden CLI builds were affected
The compromise follows the same GitHub Actions supply chain vector identified in the broader Checkmarx campaign
This is an ongoing investigation.…