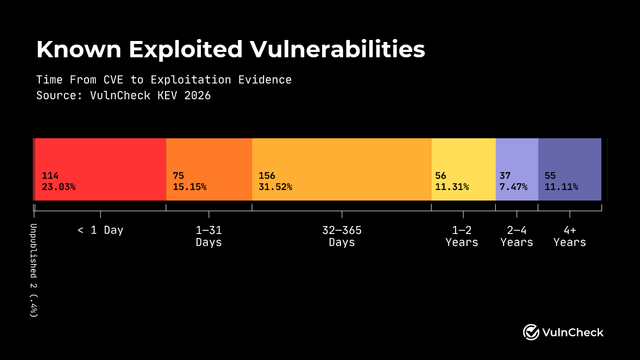
I released a security fix for OCaml's cohttp 6.3.0 today, fixing a path traversal issue . The patch itself was straightforward and in normal times, the security procedure would have been to fix it privately, inform affected users, and then issue a public advisory. This time around though, I noticed probes in my live webserver logs with the exact bug pattern just minutes after opening the PR to fix the issue . What's worse, I found I could use my own agents to find the exploit just by knowing roughly what it was about and so could have been exploiting it well before the public patch was available! Given that just the rumour of a security issue seems enough to give attackers enough info to find new exploits, we're going to need to change the way we deal with security responses in open source. 1 The rumour of a bug is all new agentic exploit systems need This particular report arrived privately on a Slack channel via Jane Street last week, and was itself found via Claude Fable.…