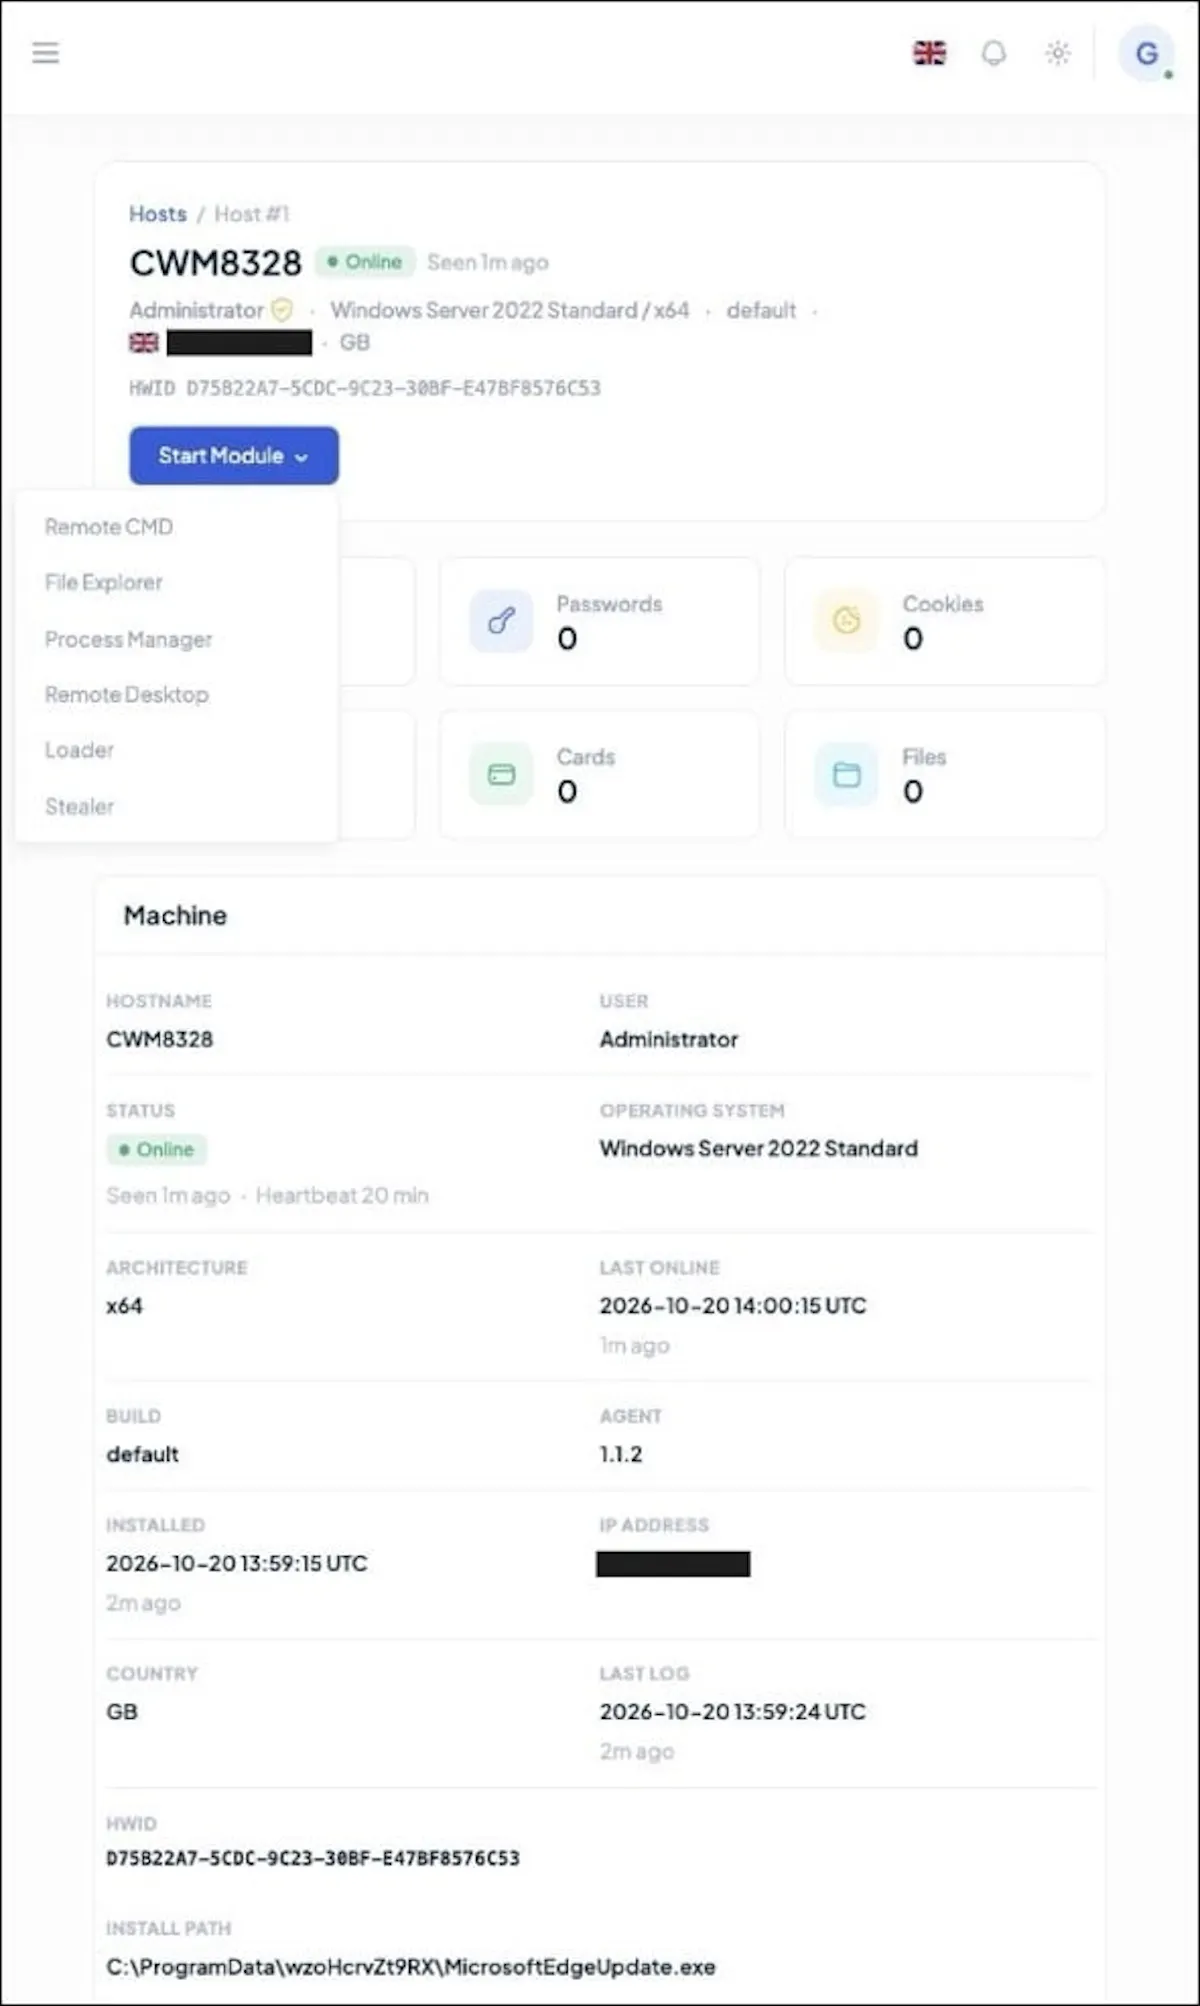
Four months after Operation Endgame took it down, StealC's seller returns with Stadia, a remote access trojan that shares StealC's code byte for byte.
In June, Europol tore down StealC, a prominent infostealer, as part of Operation Endgame. International authorities seized 326 servers and 142 domains , recovered more than 25 million stolen credentials from 385,000 infected machines, and pulled the plug on one of the most widely sold infostealers of the last three years.
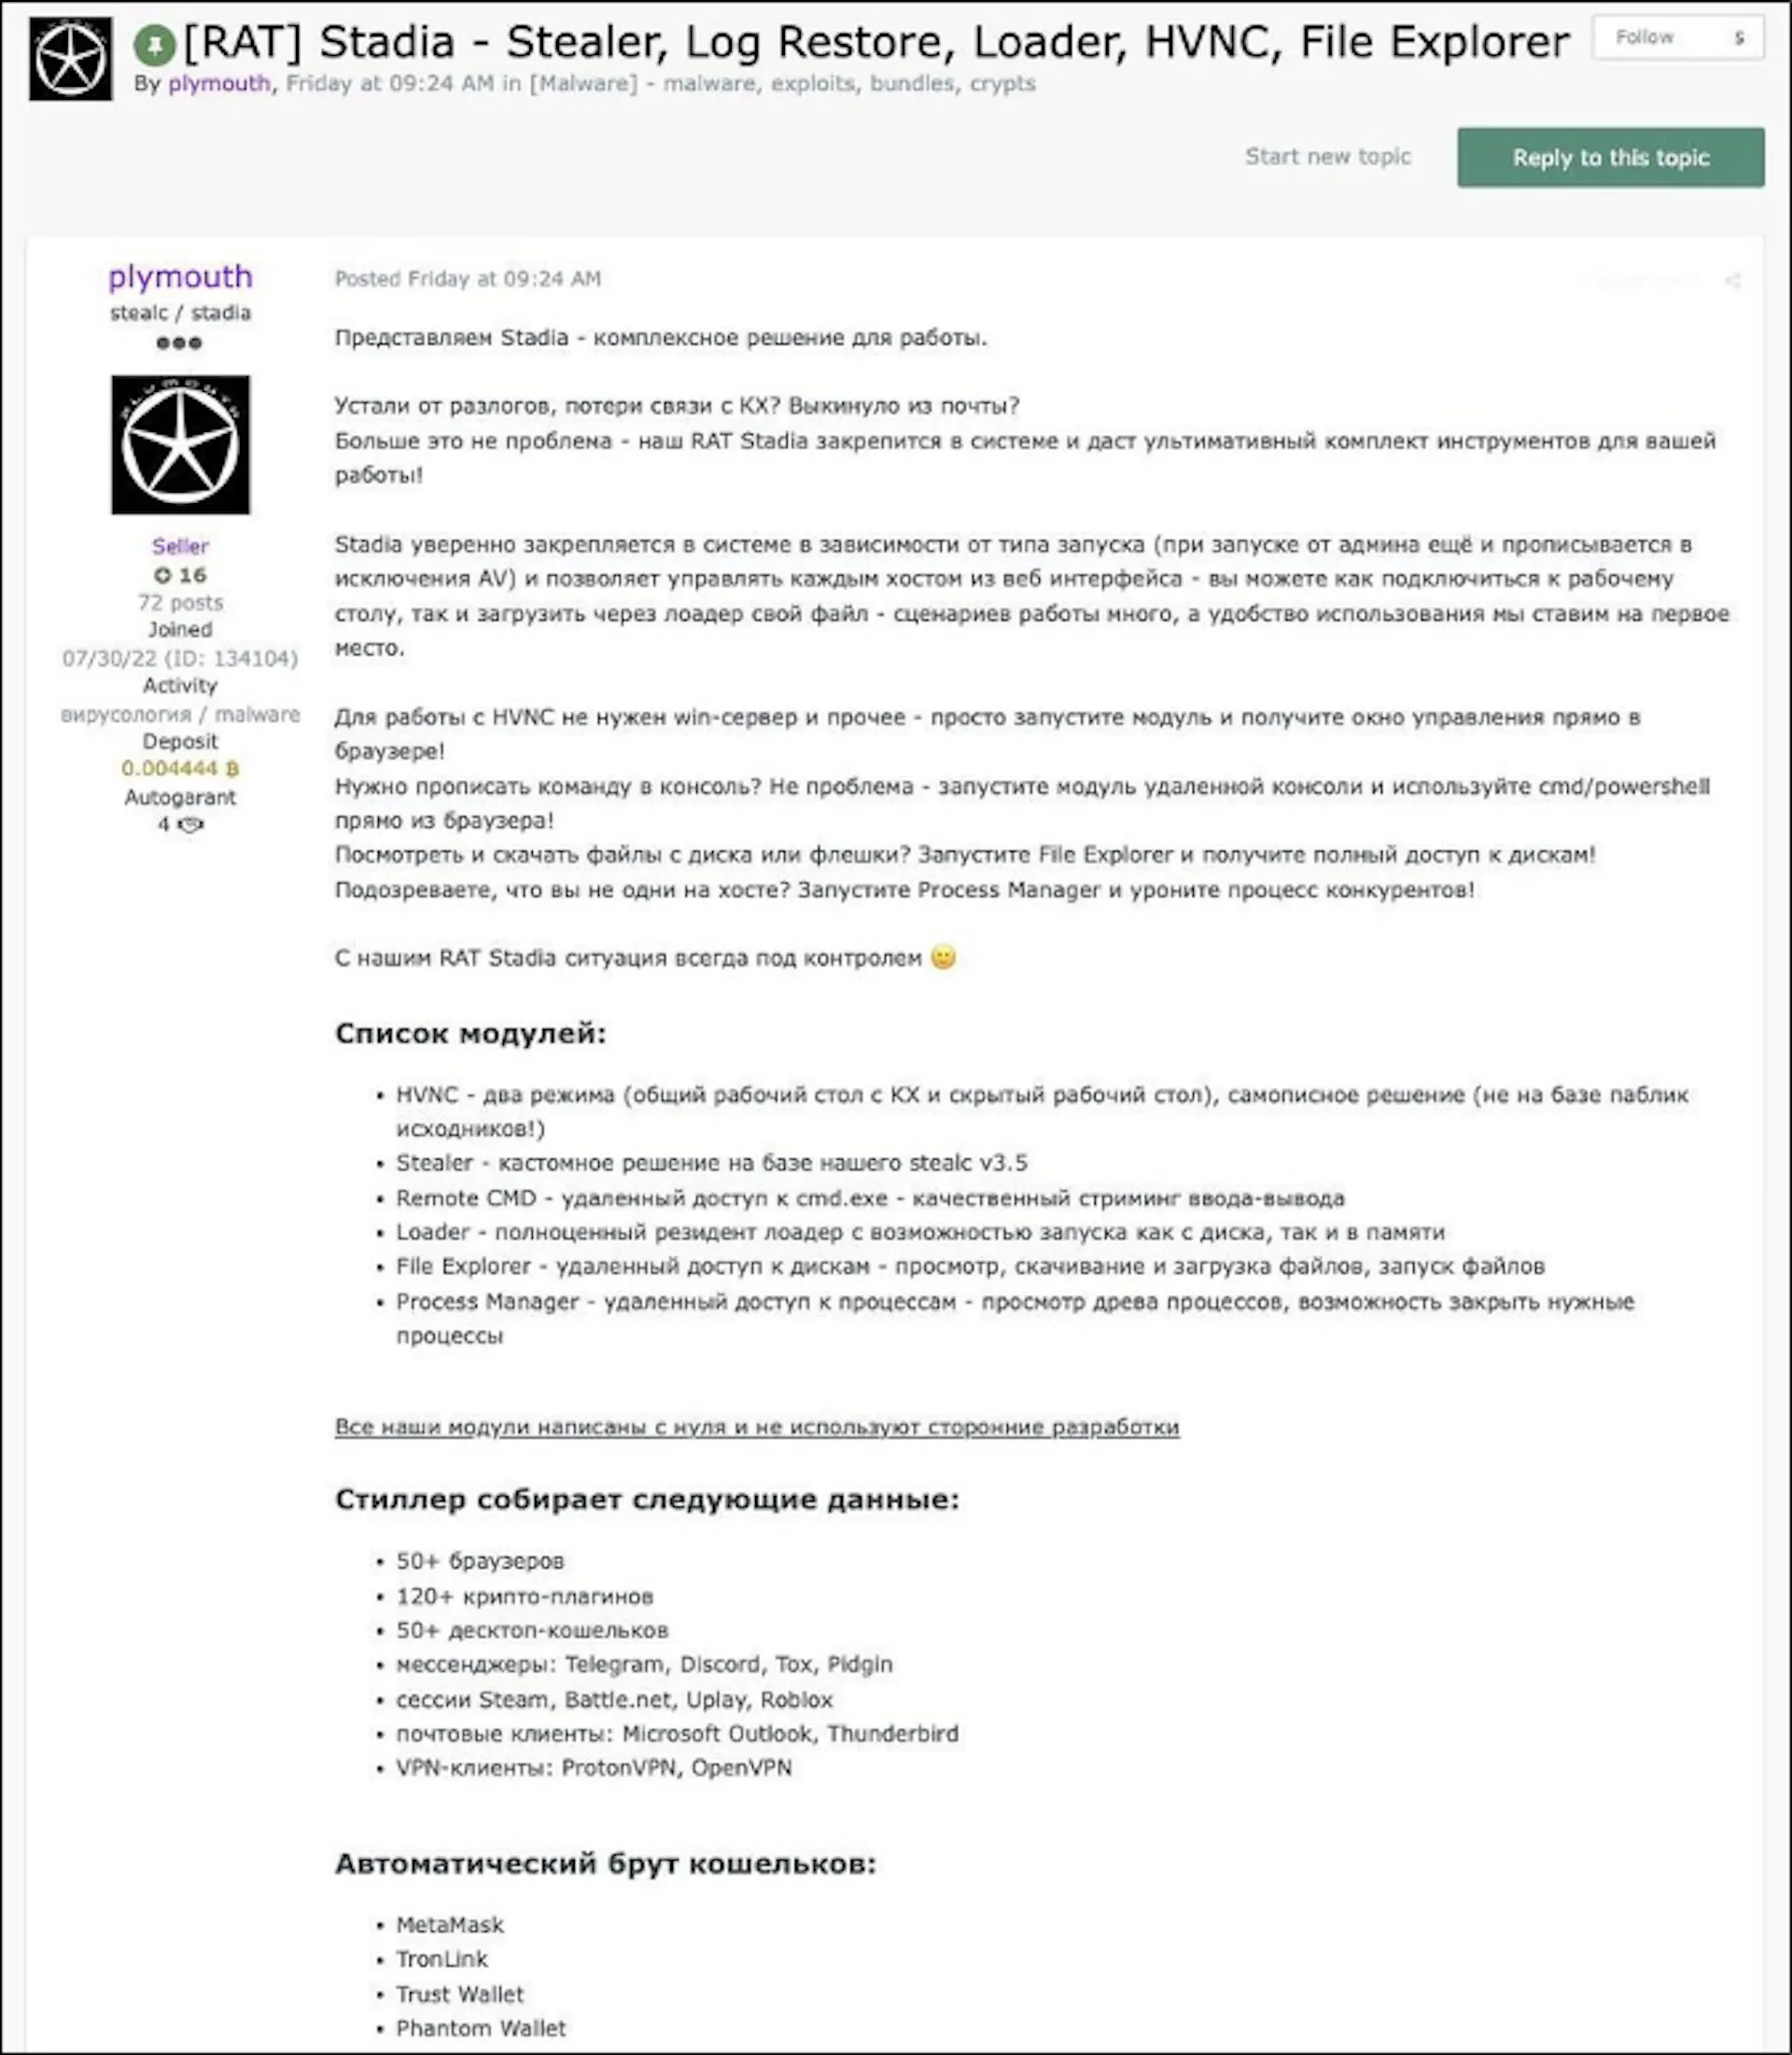
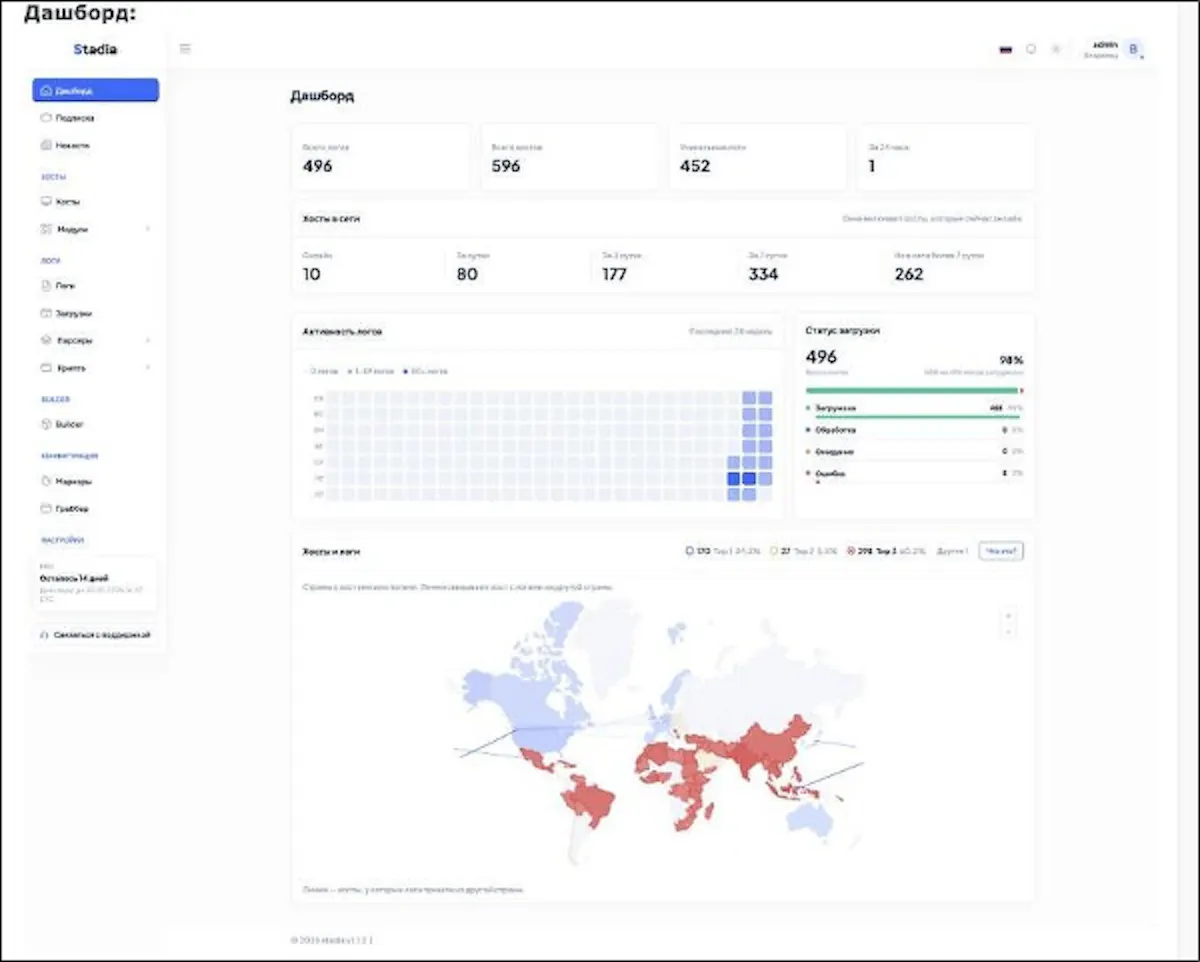
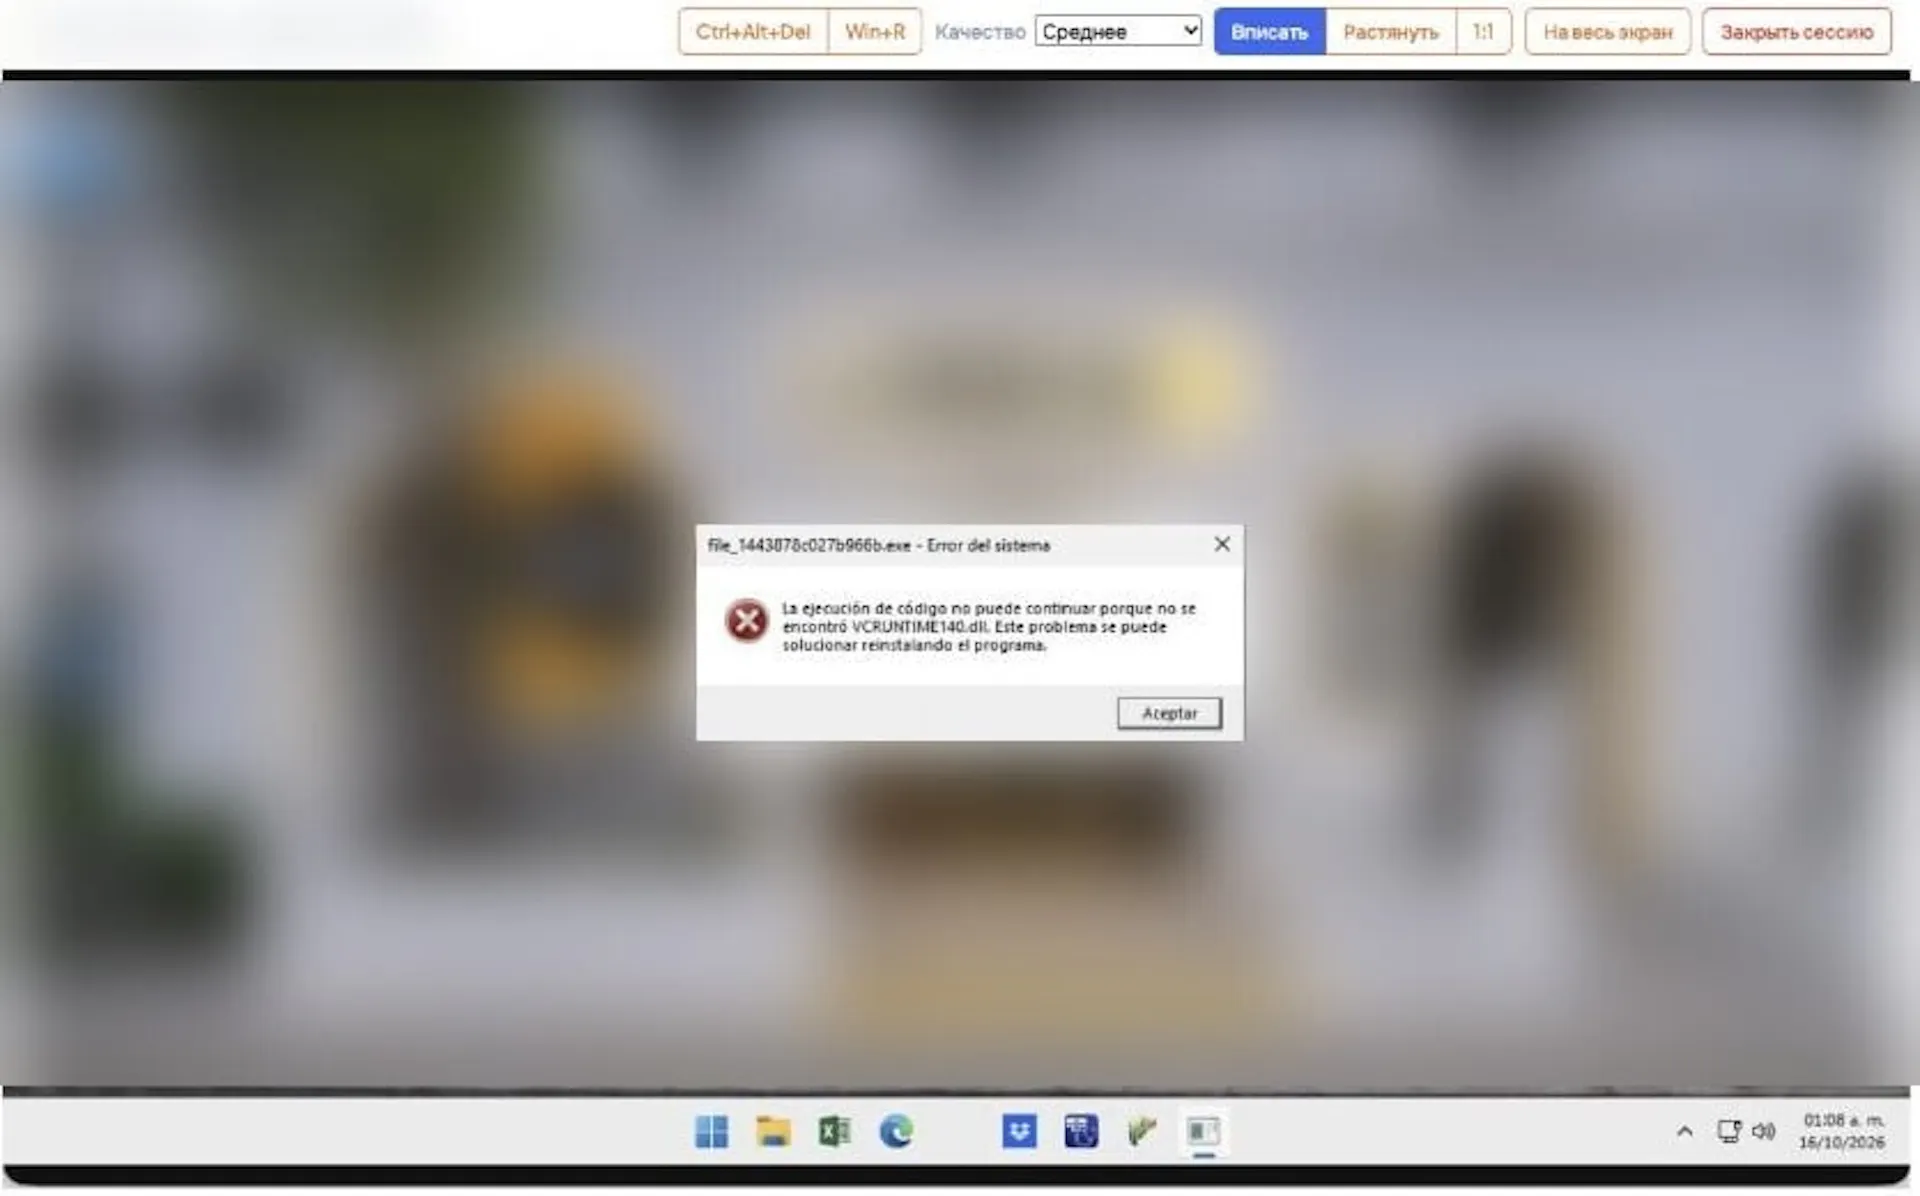
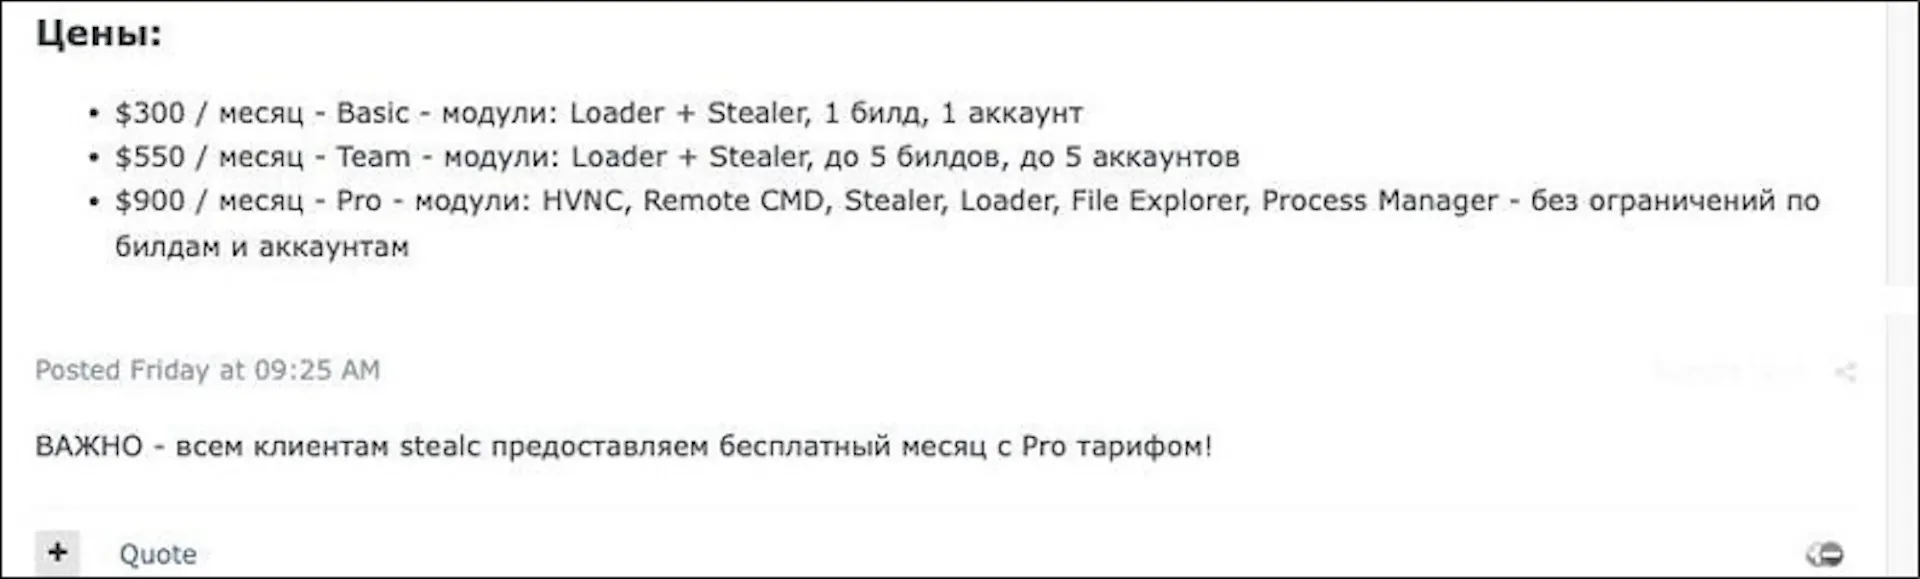
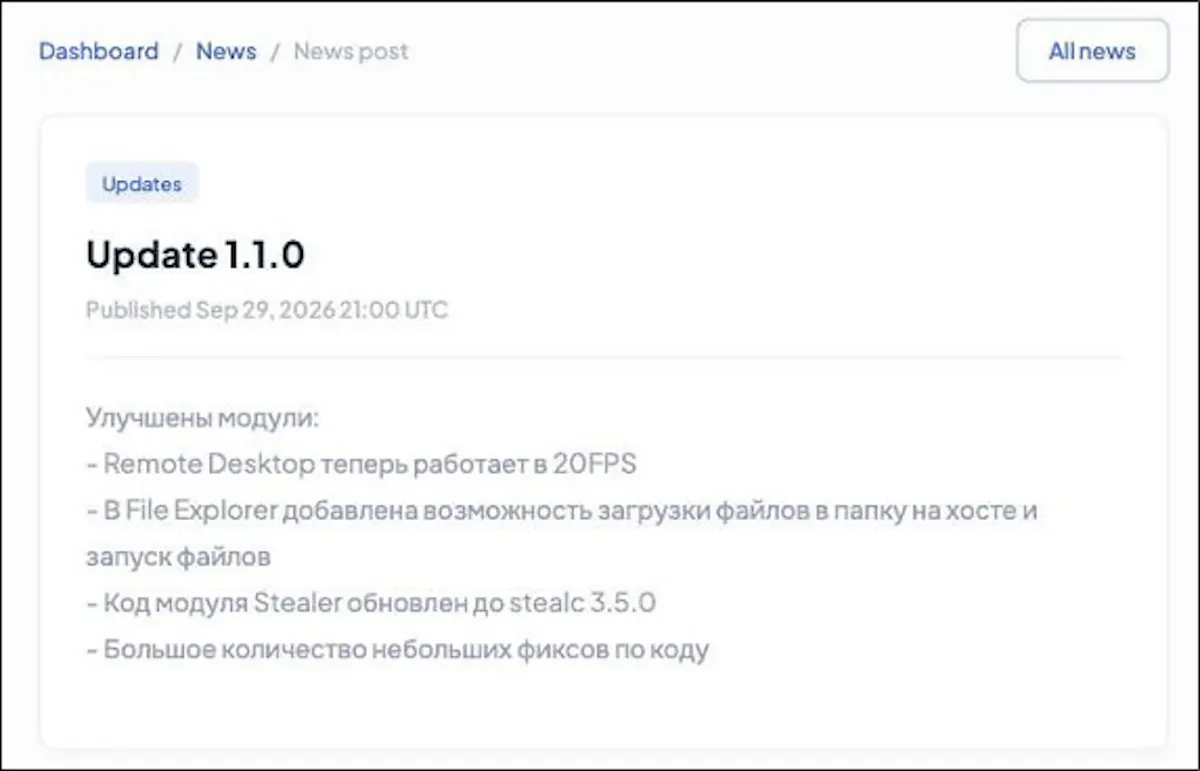
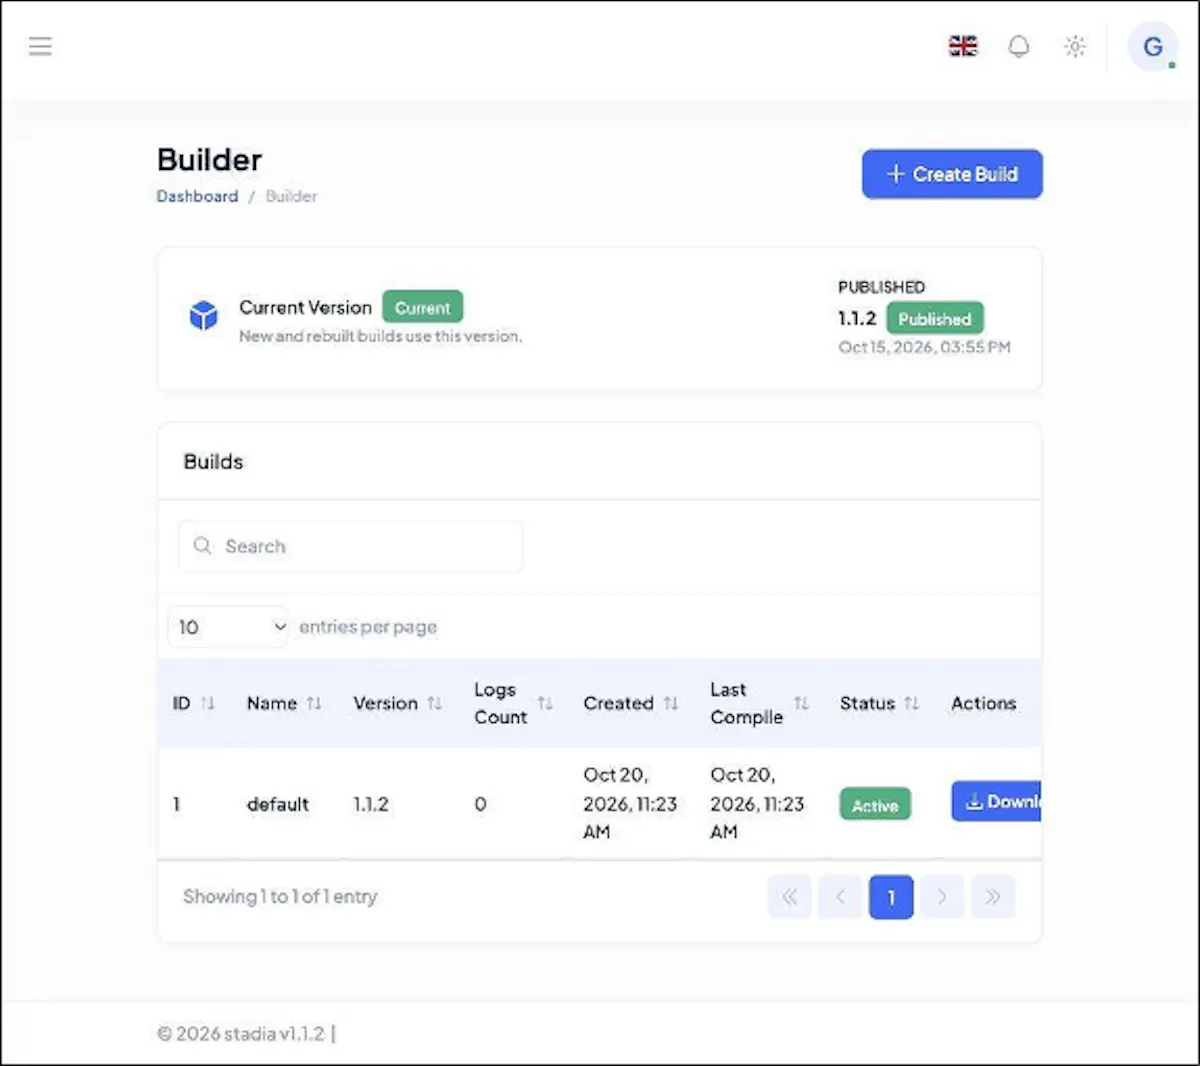
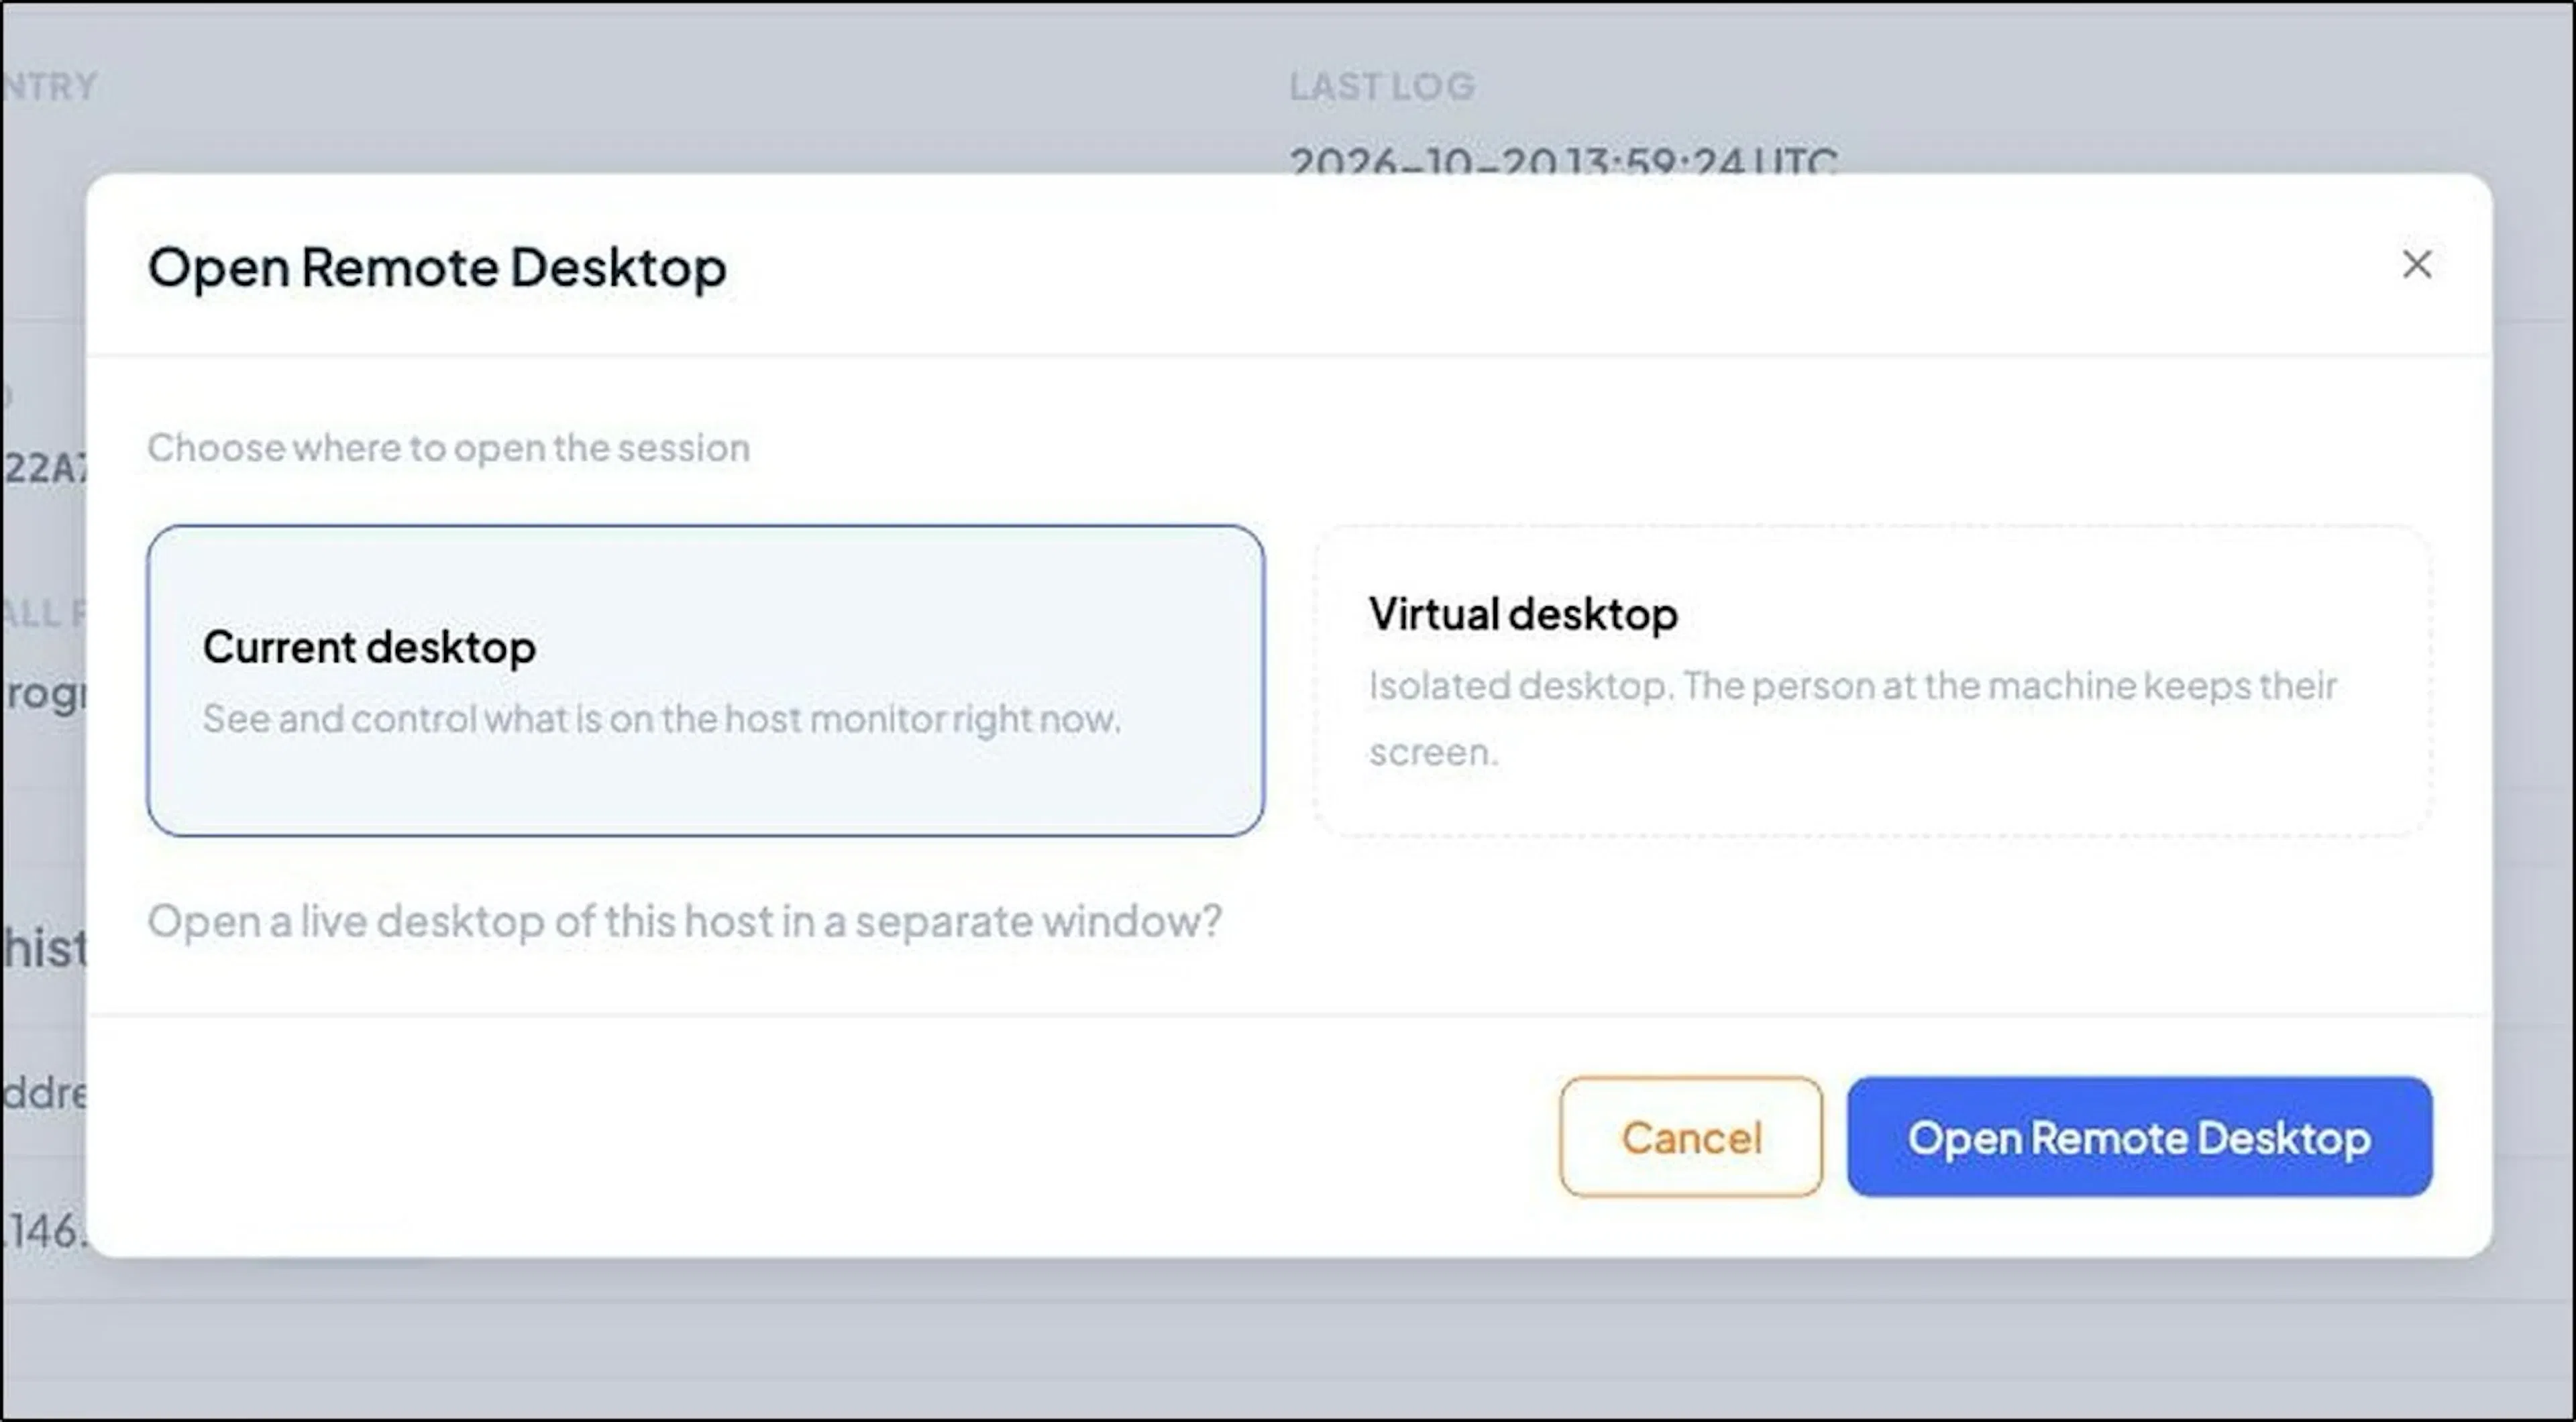
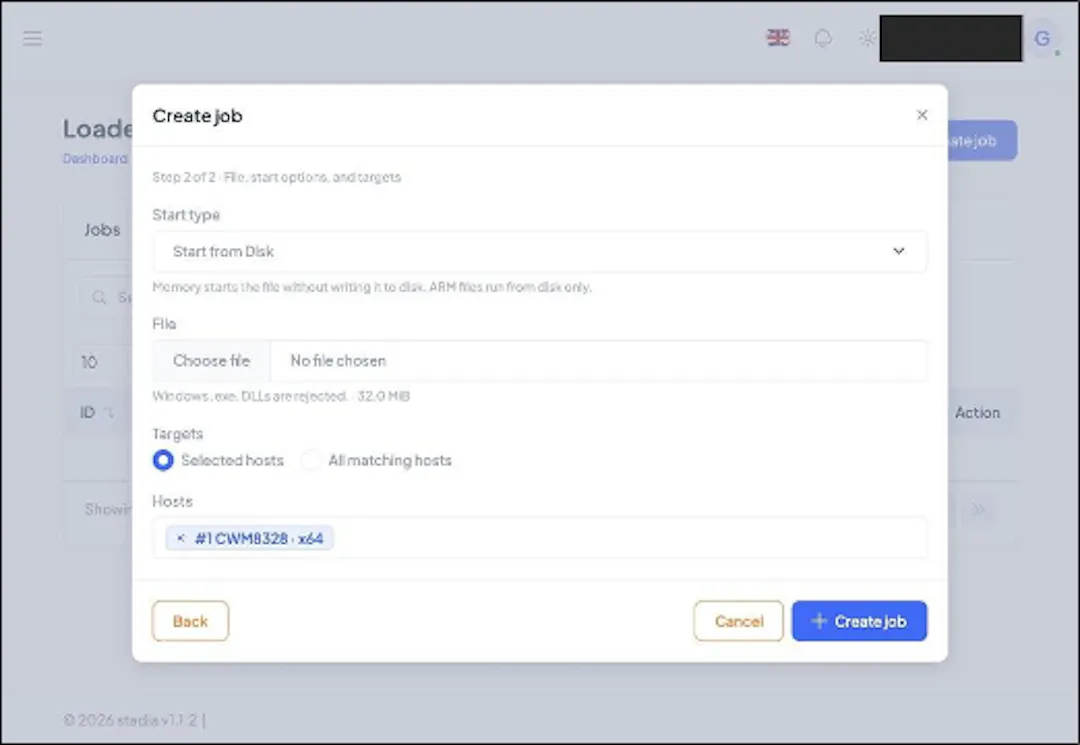
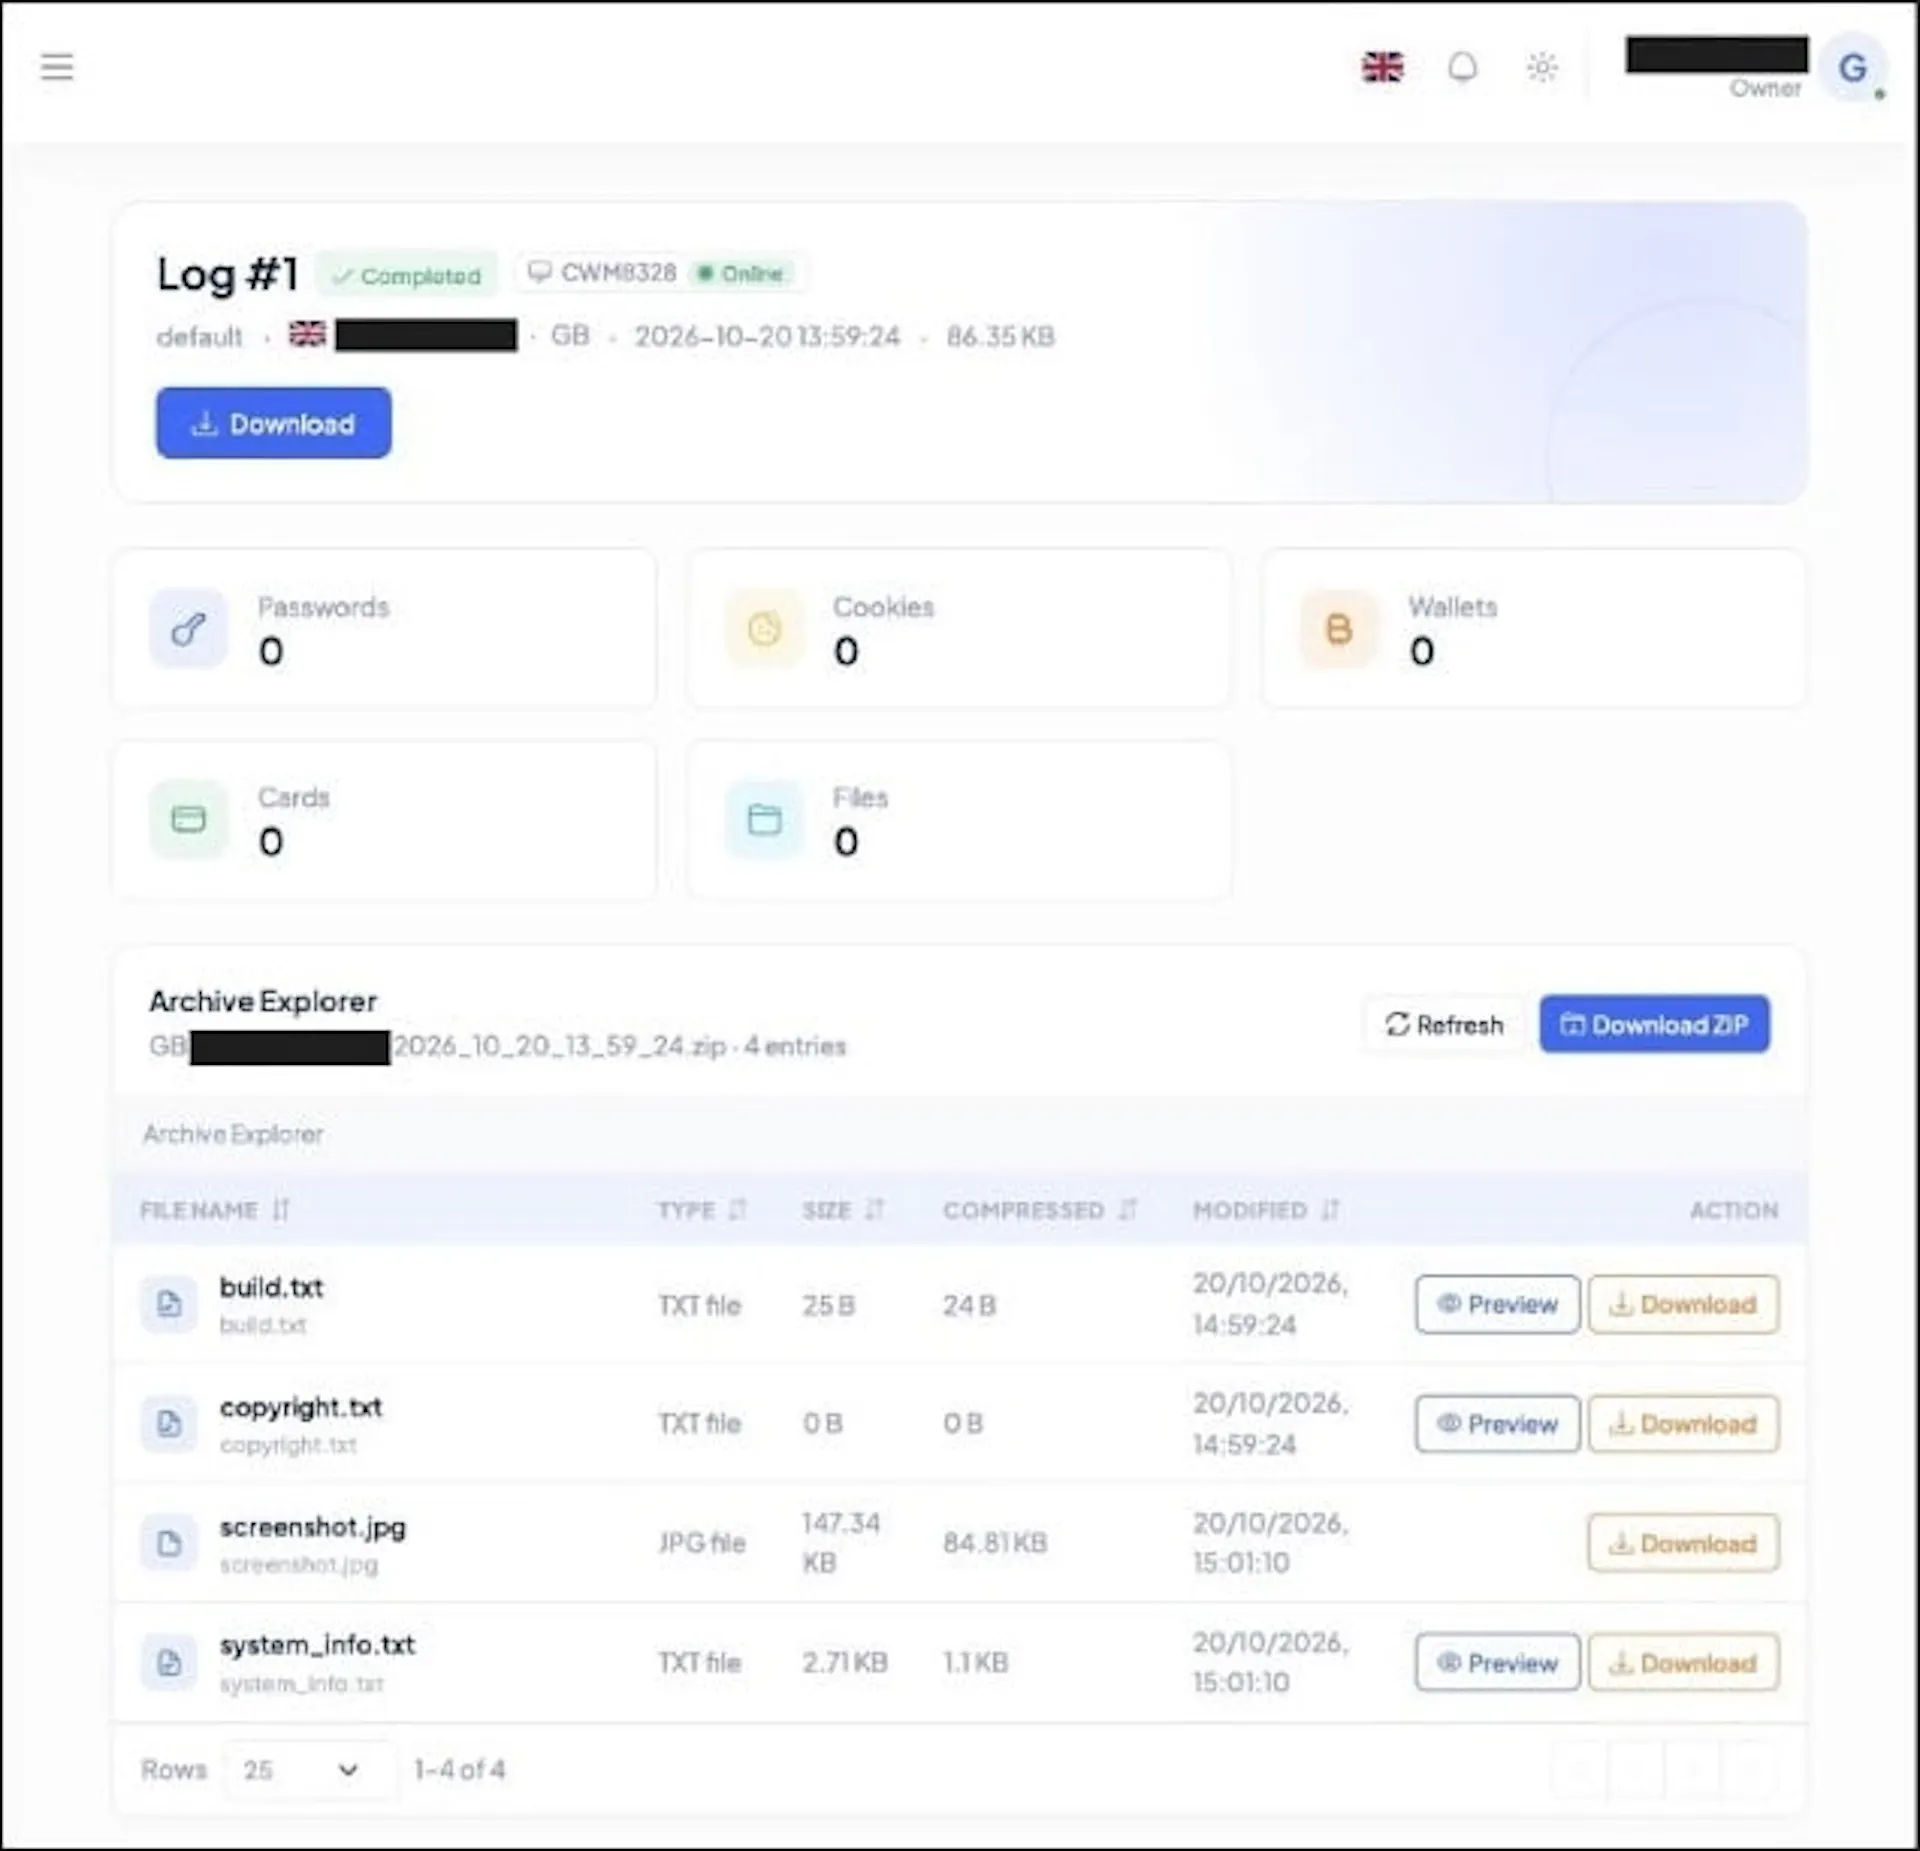
Four months later, on October 16, the seller behind StealC resurfaced with Stadia. This time it's not a stealer: it's a full remote access trojan. The RAT’s features include hidden desktop control, a live command shell, a file explorer, a process manager and an in-memory loader, with StealC's stealer welded on as one module among six.…