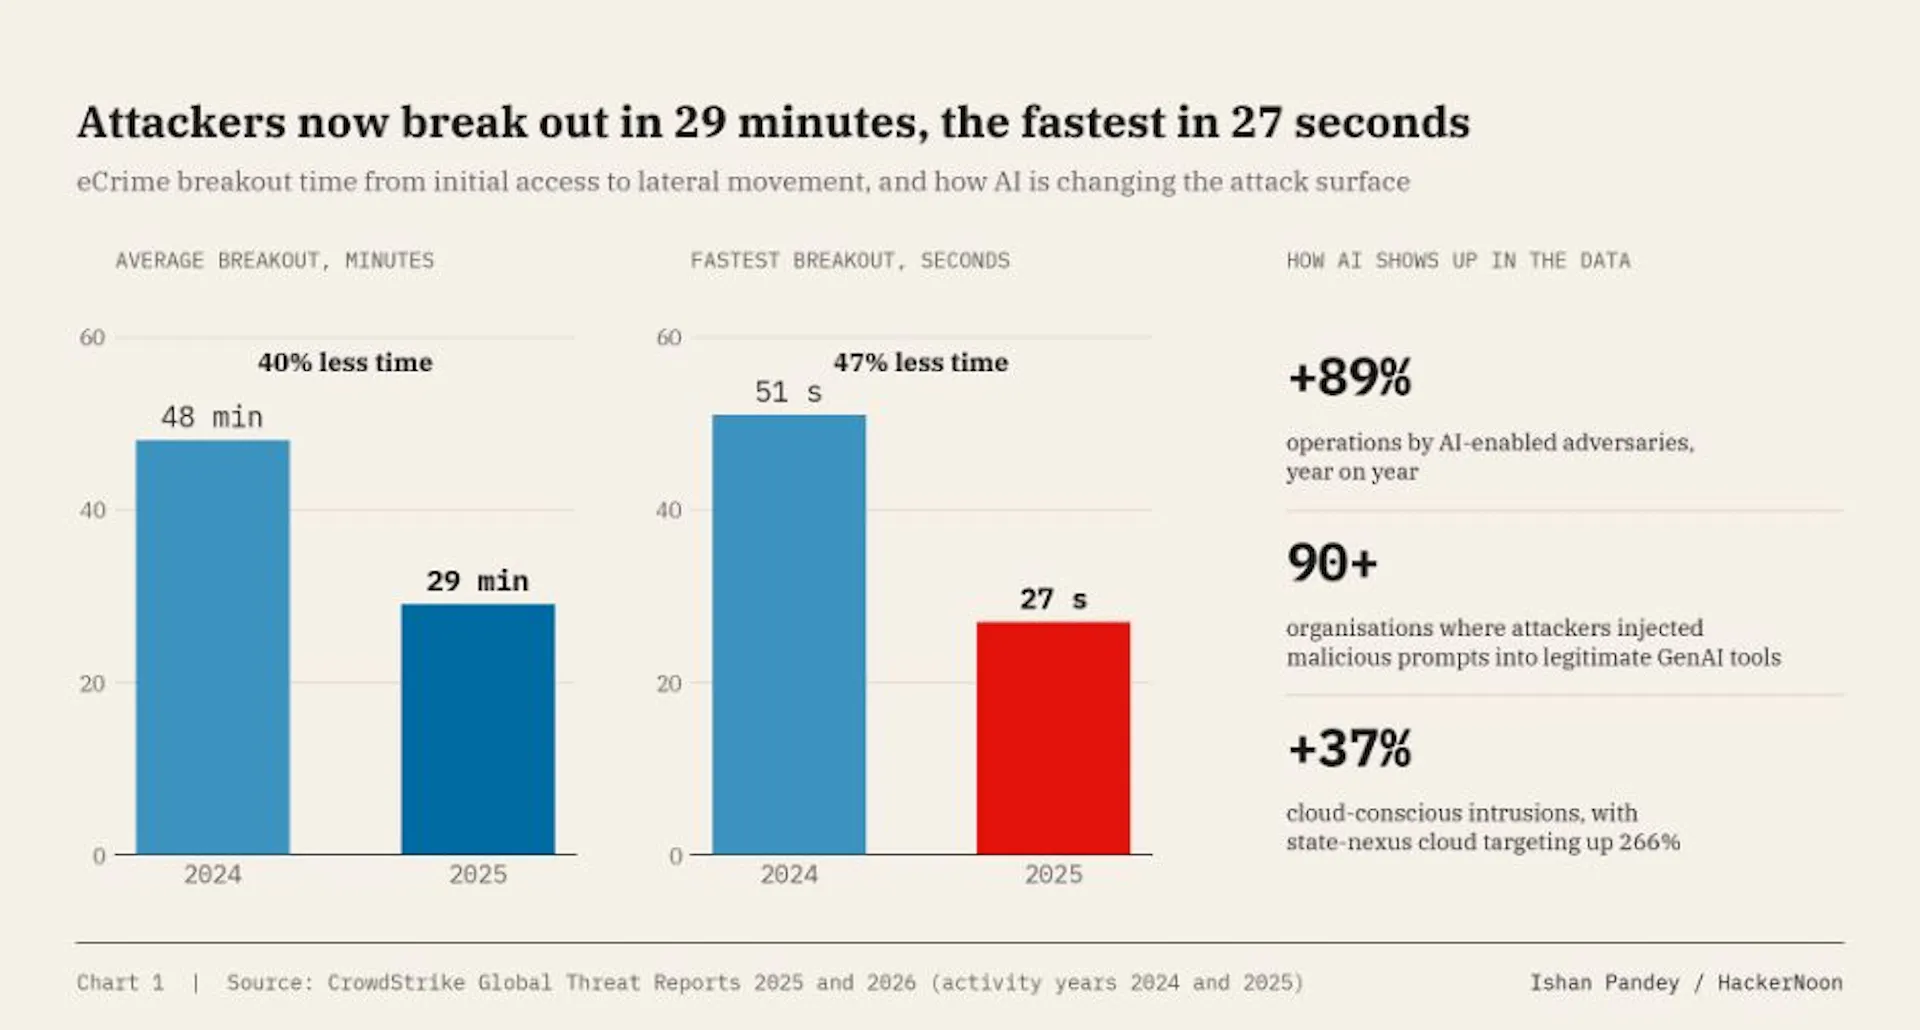
An AI agent that deploys code, pays an invoice or signs a blockchain transaction usually does it with whatever a human would have used, a private key, an API secret or a cloud credential, sitting in its environment where anything that talks to the model can reach it. One prompt injection or one leaked log hands an attacker everything the agent was allowed to do, at a time when CrowdStrike has watched intruders move from first access to the rest of a network in 27 seconds.
1Claw sells a different arrangement in which the agent gets permission to act without receiving the master key, through HSM-backed vaults, per-agent spending limits and an enclave proxy that screens model traffic for prompt injection.…