Blog
Hacking OpenAI
A heap overflow and SSO misconfiguration to compromise OpenAI internal repositories
September 13, 2026 11 min read
Intro
On July 25, 2026, we chained two critical vulnerabilities to compromise multiple OpenAI employees’ ChatGPT accounts. With these accounts, we could then access internal OpenAI repositories, and potentially many other connectors.
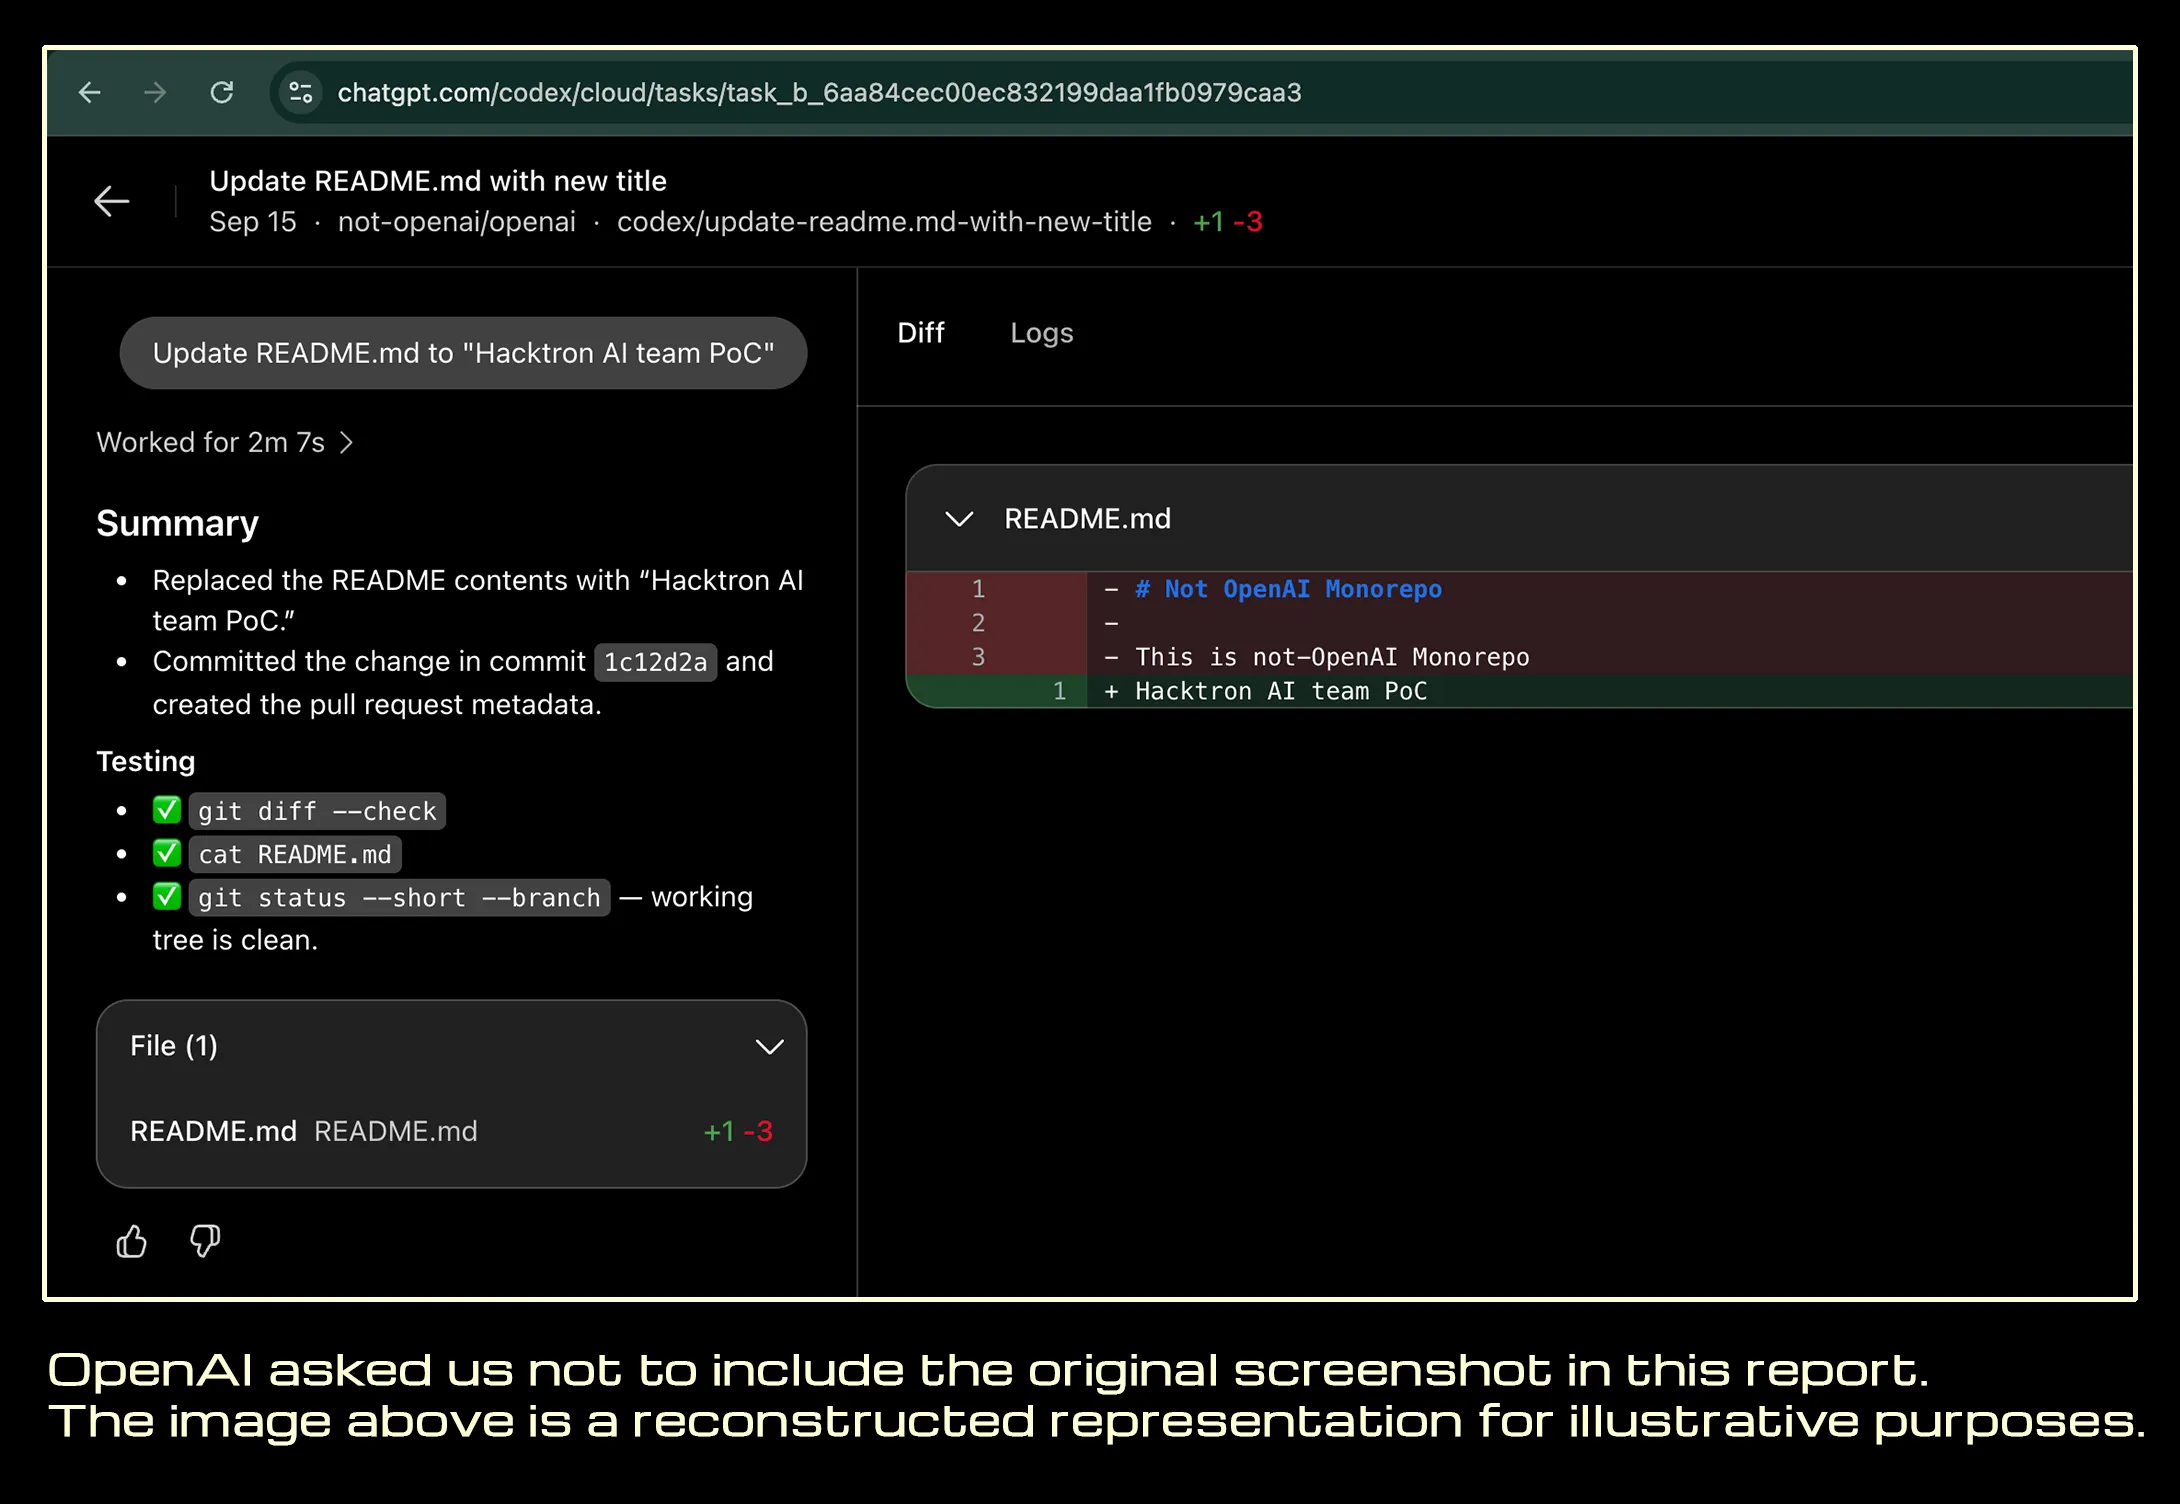
To prove we had in fact gained the access we believed without allowing ourselves to learn any sensitive information, we used the employee’s Codex to open a PR #1186742 in OpenAI’s internal monorepo openai/openai .
Exploit chain libheif Image decoder
Debian Missing security backport
ImageMagick Uses libheif
Discourse Image uploads
OpenAI forum community.openai.com
OpenAI SSO Identity flaw
ChatGPT / Codex Account access
GitHub Connected integration
Internal repos OpenAI
Until two months ago, any user or OpenAI employee logging into OpenAI’s own help forum ( community.openai.com ) could have had their ChatGPT and Codex accounts taken…