March 18, 2026 · 13 minutes read
A friend of mine once told me:
If you ever spot an IIS blue screen, don’t stop there; there must be something.
Yep, he was right. That IIS splash page is not a dead end. Behind that blue window sits one of the most consistently misconfigured web servers on the www, and it’s begging you to look deeper.
So let me walk you through how I approach IIS targets during bug bounty:
table of contents
psst, psst, IIS servers, where are you? shodan
google dorking
active tech fingerprinting
ok, I found an IIS server. now what? internal IP disclosure
pwn time nuclei templates: automate the boring stuff
the HTTPAPI 2.0 dead end that isn’t
IIS tilde enumeration: the gift that keeps giving using LLMs
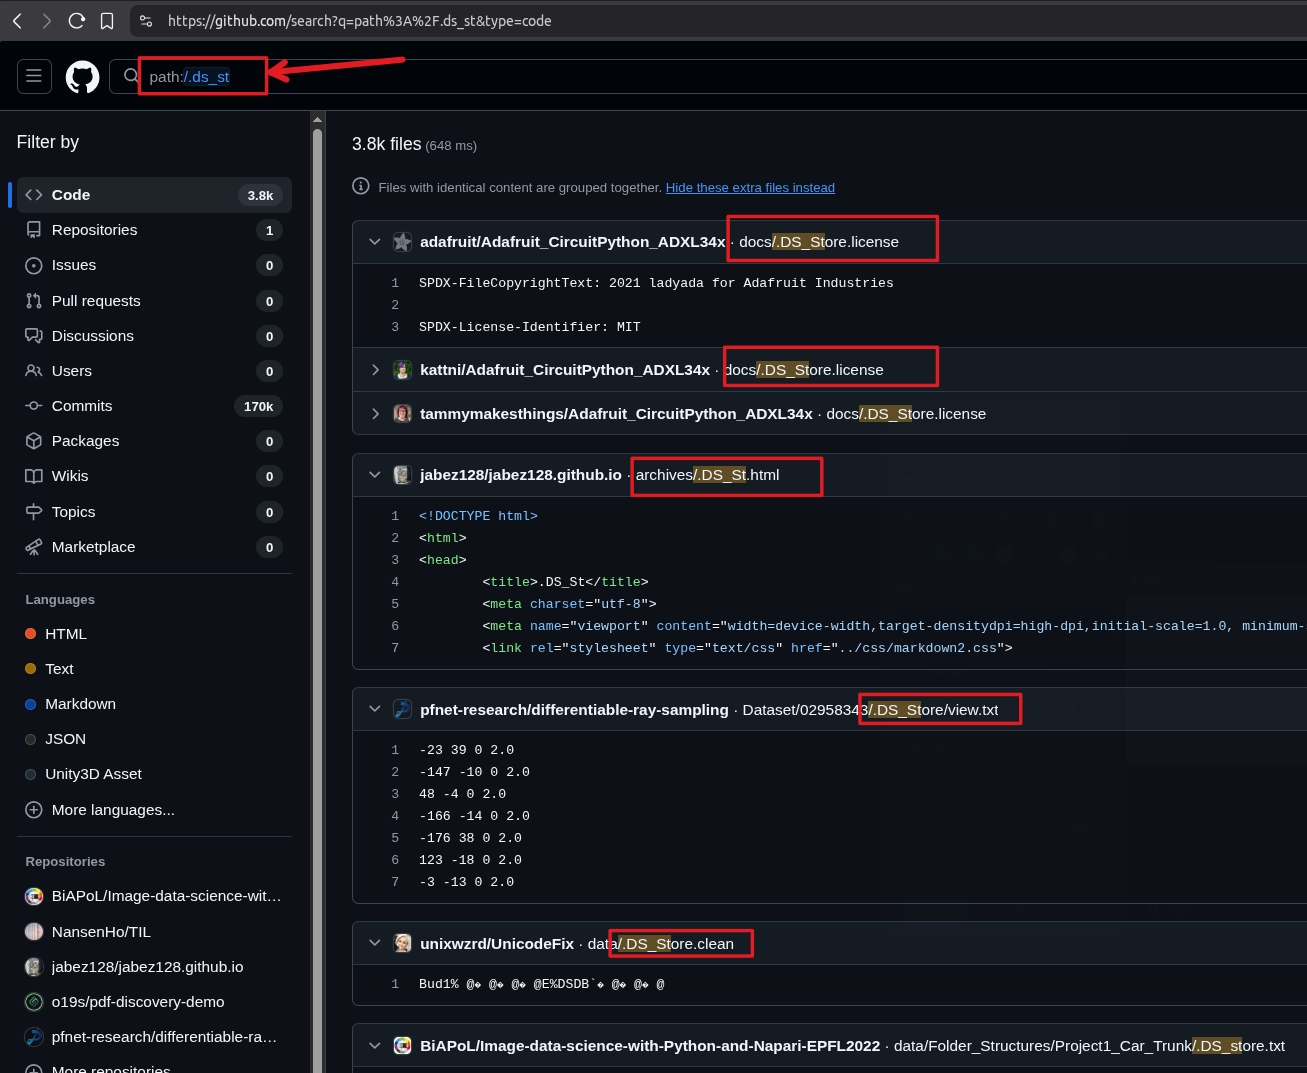
github dorks to resolve shortnames
using BigQuery to resolve shortnames
bruteforcing the rest with crunch
fuzzing: the IIS-specific wordlist matters
web.config: the keys to the kingdom path traversal to web.config
bin directory DLL exposure via cookieless sessions
reverse proxy…