Blog
Security Research
Spoofing DNS Records by Abusing DHCP DNS Dynamic Updates
Ori David is a Security Researcher at Akamai. His research is focused on offensive security, malware analysis, and threat hunting.
Executive summary
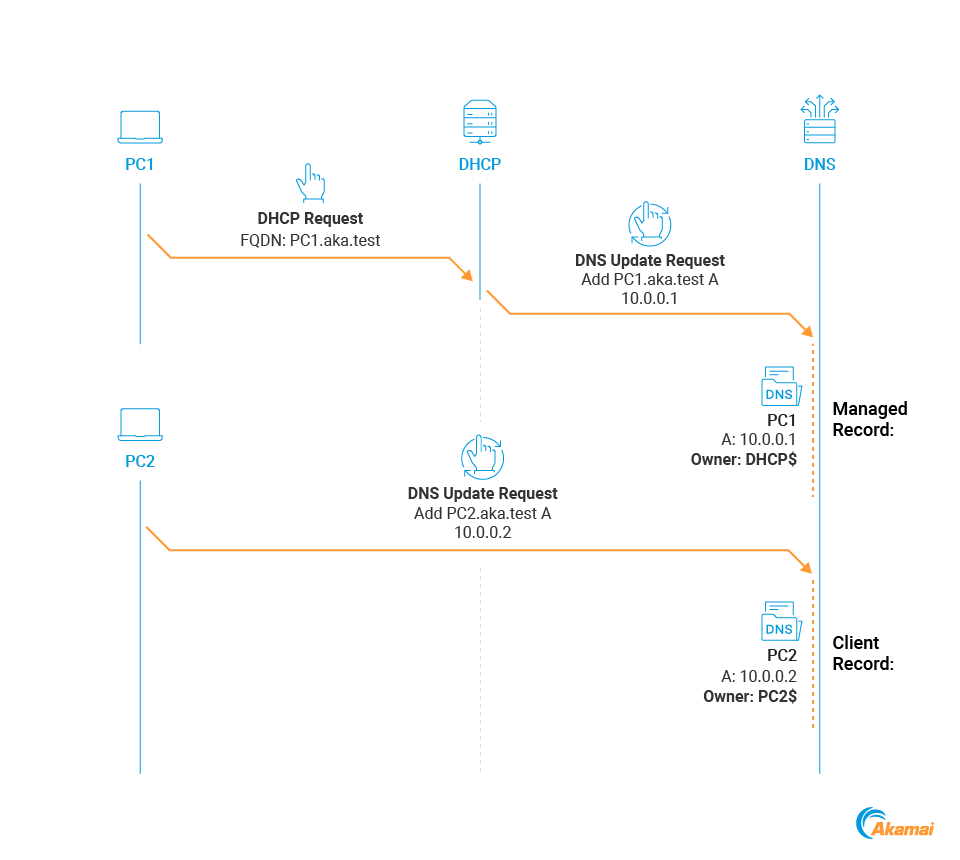
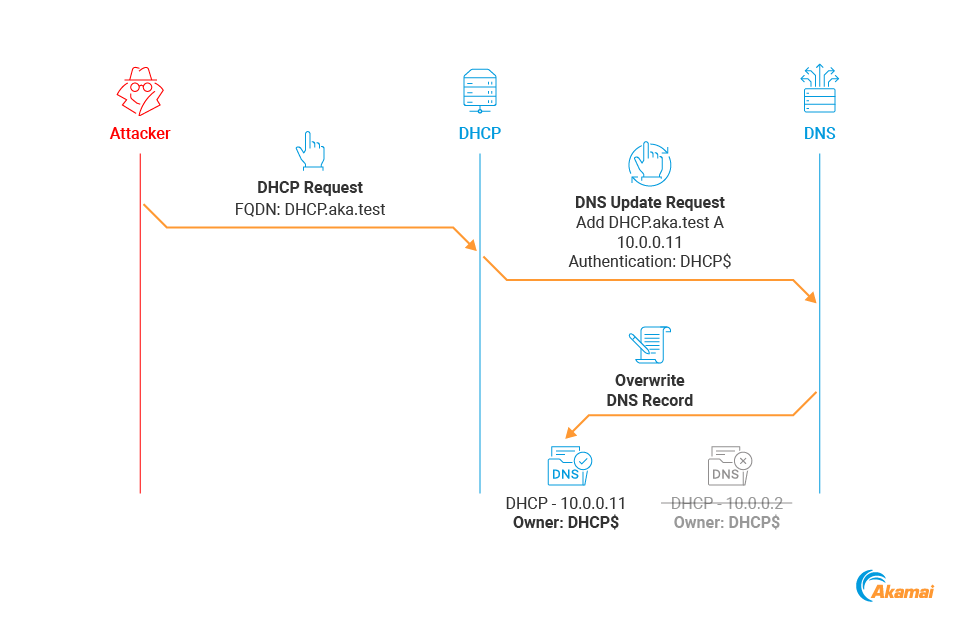
\r\n \r\n Akamai researchers discovered a new set of attacks against Active Directory domains that use Microsoft Dynamic Host Configuration Protocol (DHCP) servers.
\r\n
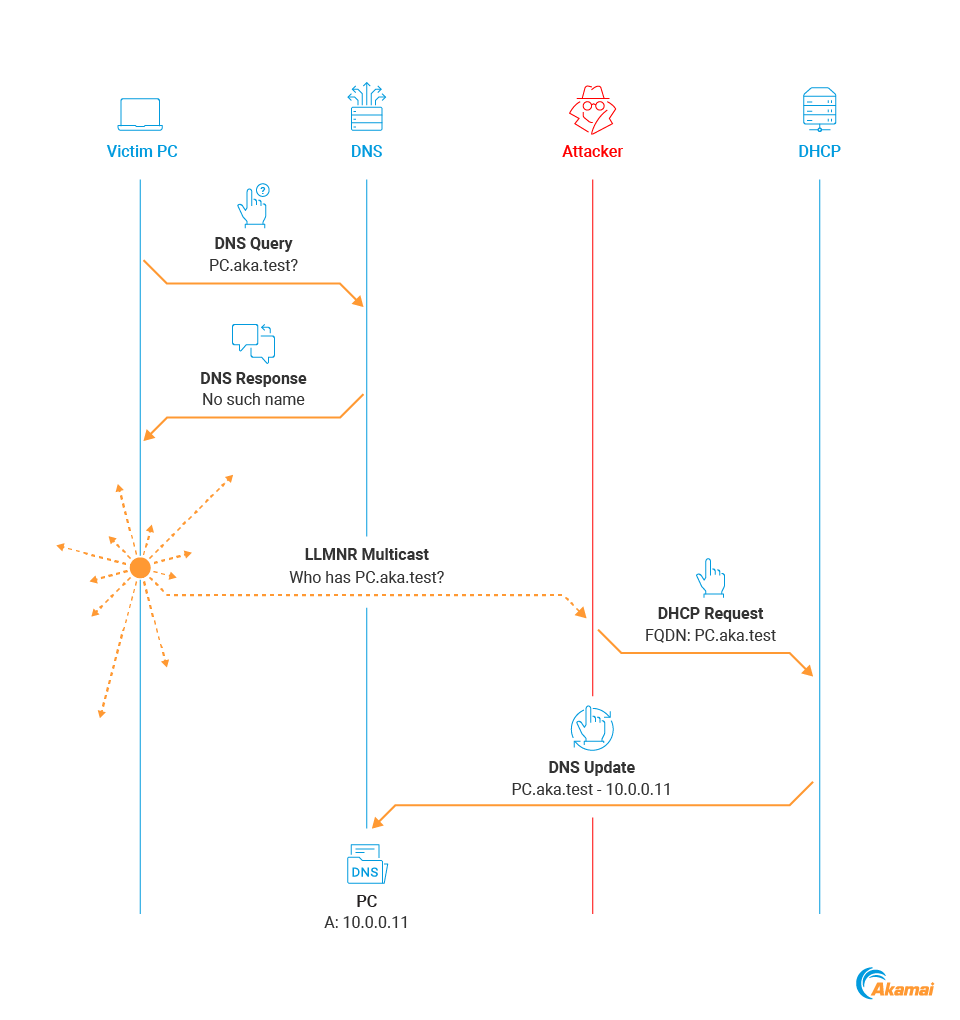
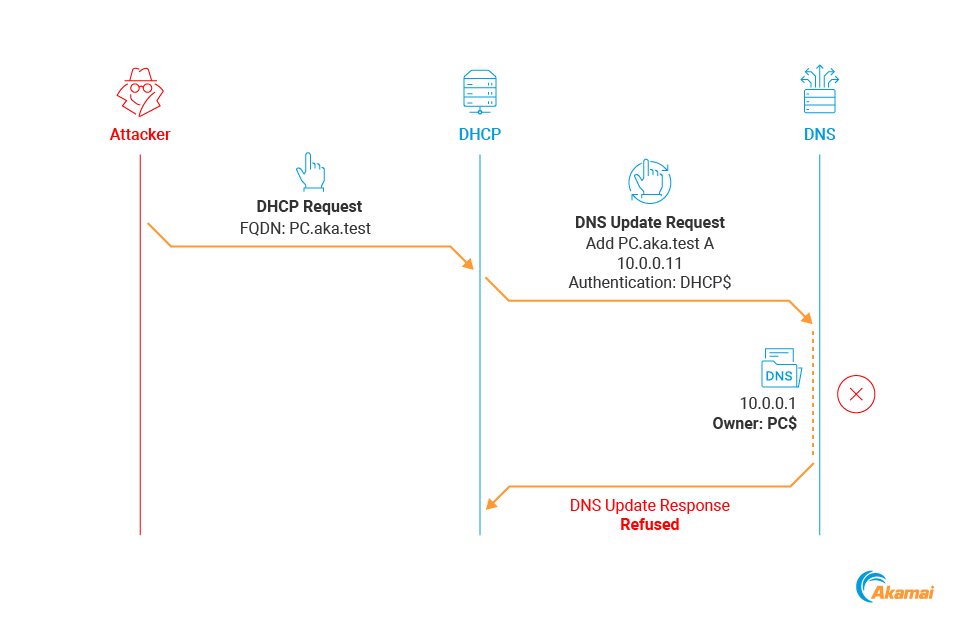
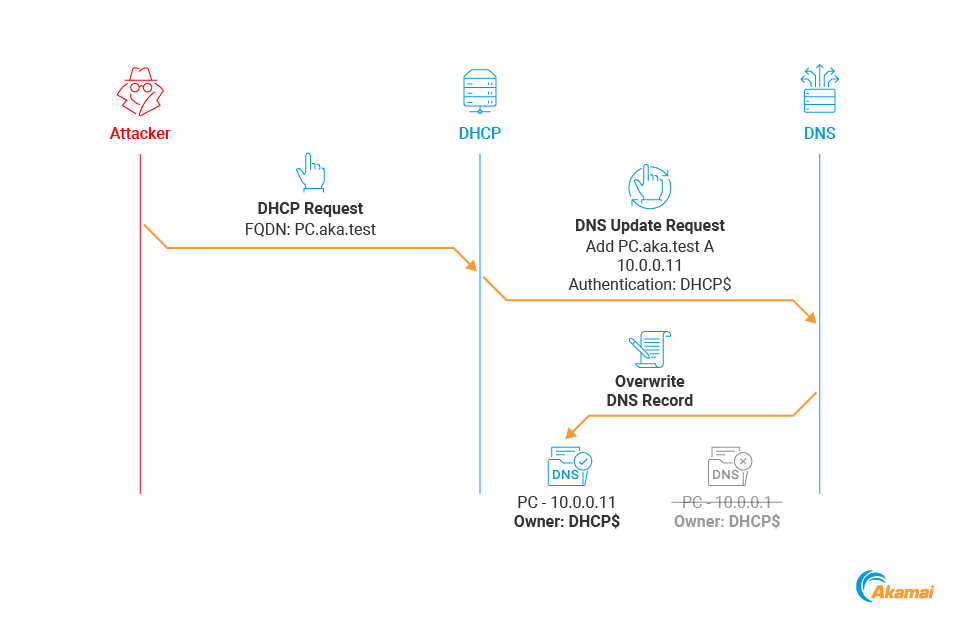
\r\n These attacks could allow attackers to spoof sensitive DNS records, resulting in varying consequences from credential theft to full Active Directory domain compromise. The attacks don't require any credentials, and work with the default configuration of Microsoft DHCP server.
\r\n
\r\n The number of impacted organizations can be significant.…