Blog
Security Research
Detecting and Mitigating the Apache Camel Vulnerabilities
The vulnerability is trivial to exploit and could lead to devastating results, including remote code execution.
Executive summary
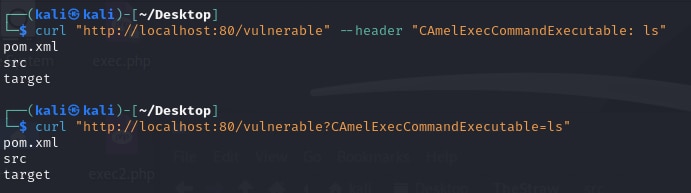
\r\n On March 9, 2025, Apache Camel disclosed CVE-2025–27636 , a vulnerability that stems from incorrect filtering of request headers that can lead to remote code execution.
\r\n
\r\n This vulnerability lies in a library, creating both direct and indirect dependency and complicating detection and mitigation.
\r\n
\r\n In this blog post, Akamai researchers provide in-depth details about the vulnerability, exploitation techniques, and detection strategies.
\r\n
\r\n An Akamai Adaptive Security Engine Rapid Rule is automatically providing protection for Akamai App & API Protector customers .
\r\n
\r\n We also provide an Akamai Guardicore Segmentation Insight query for detection .
\r\n
\r\n \r\n \r\n Akamai Hunt customers who were affected have already received…