Ophir leads the security research team in Akamai's Enterprise Security Group.
Peleg is a security researcher.
Executive summary
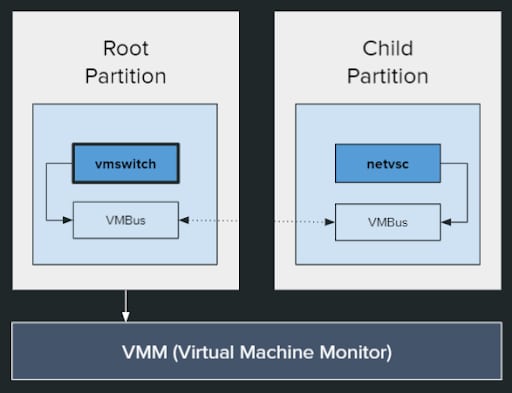
\r\n \r\n Guardicore Labs, in collaboration with SafeBreach Labs, found a critical vulnerability in Hyper-V’s virtual network switch driver ( vmswitch.sys ).
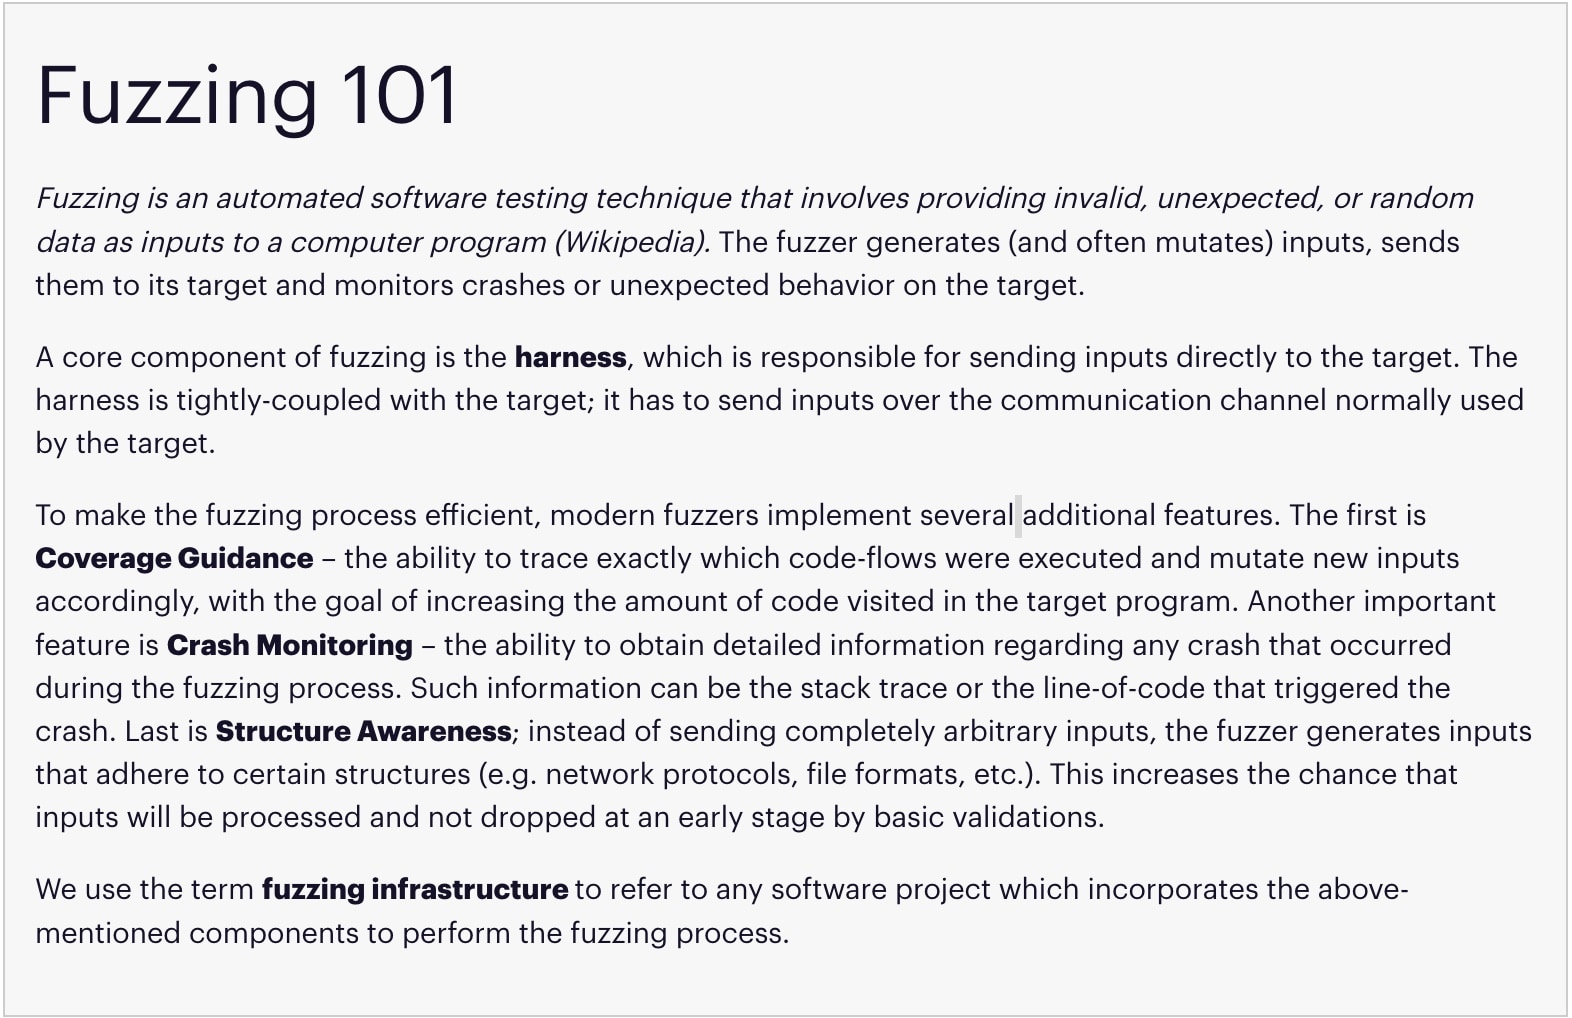
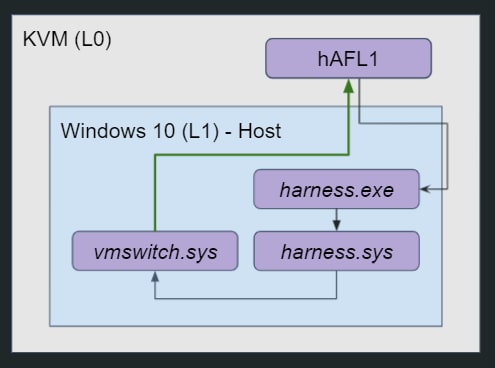
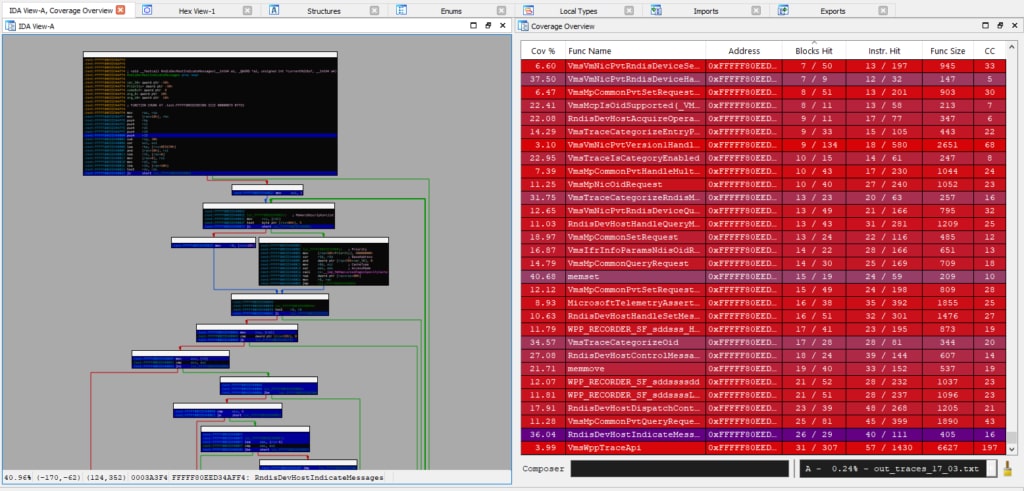
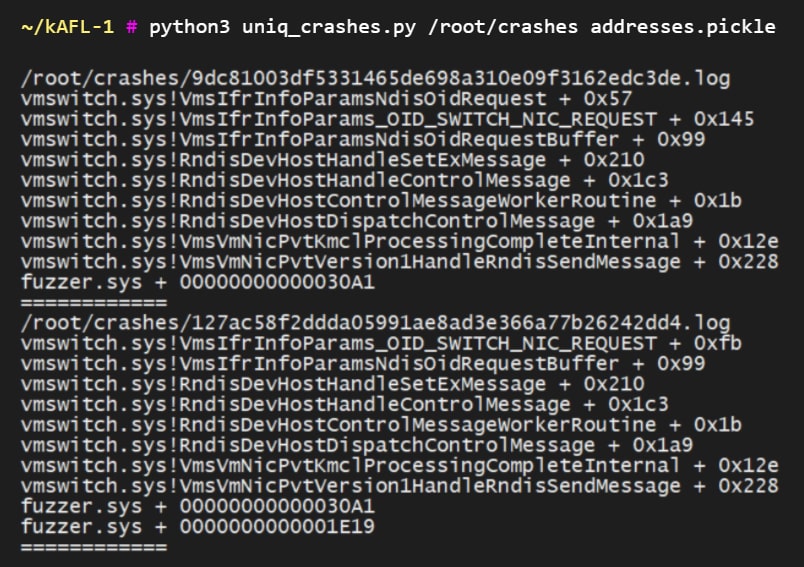
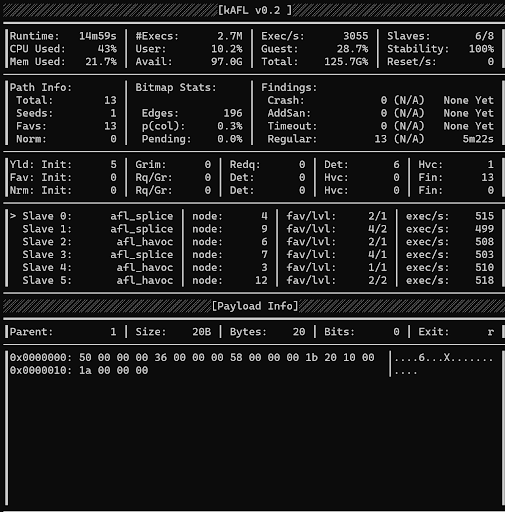
\r\n The vulnerability was found using an in-house built fuzzer we named hAFL1 and which we open-source today . The repository includes detailed, step-by-step instructions on how to deploy and run the fuzzer on a Linux server.
\r\n hAFL1 is a modified version of kAFL which enables fuzzing Hyper-V paravirtualized devices and adds structure awareness, detailed crash monitoring and coverage guidance.
\r\n The RCE vulnerability we found ( CVE-2021-28476 ) was assigned a CVSS score of 9.9 and is detailed in a separate blog post.
\r\n \r\n"}}"> Executive summary
Guardicore Labs, in collaboration with SafeBreach Labs, found a critical vulnerability in Hyper-V’s virtual network switch driver ( vmswitch.sys ).
The vulnerability…