Akamai acquired LayerX. This previously published blog post reflects the product and feature names on the original date of publication.
A New Vector for Prompt Injection Attacks That Threatens Both Commercial and Internal AI Tools
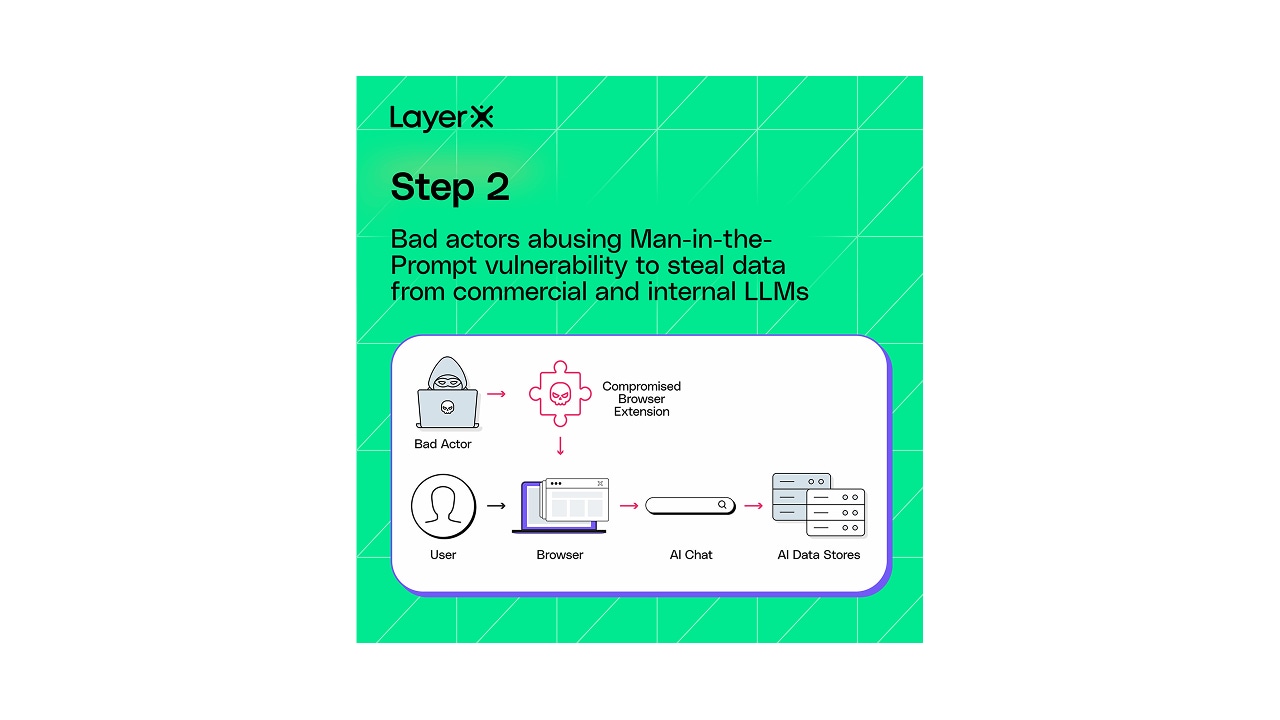
LayerX researchers have identified a new class of exploit that directly targets these tools through a previously overlooked vector: the browser extension. This means that practically any user or organization that have browser extensions installed on their browsers (as 99% of enterprise users do) are potentially exposed to this attack vector.
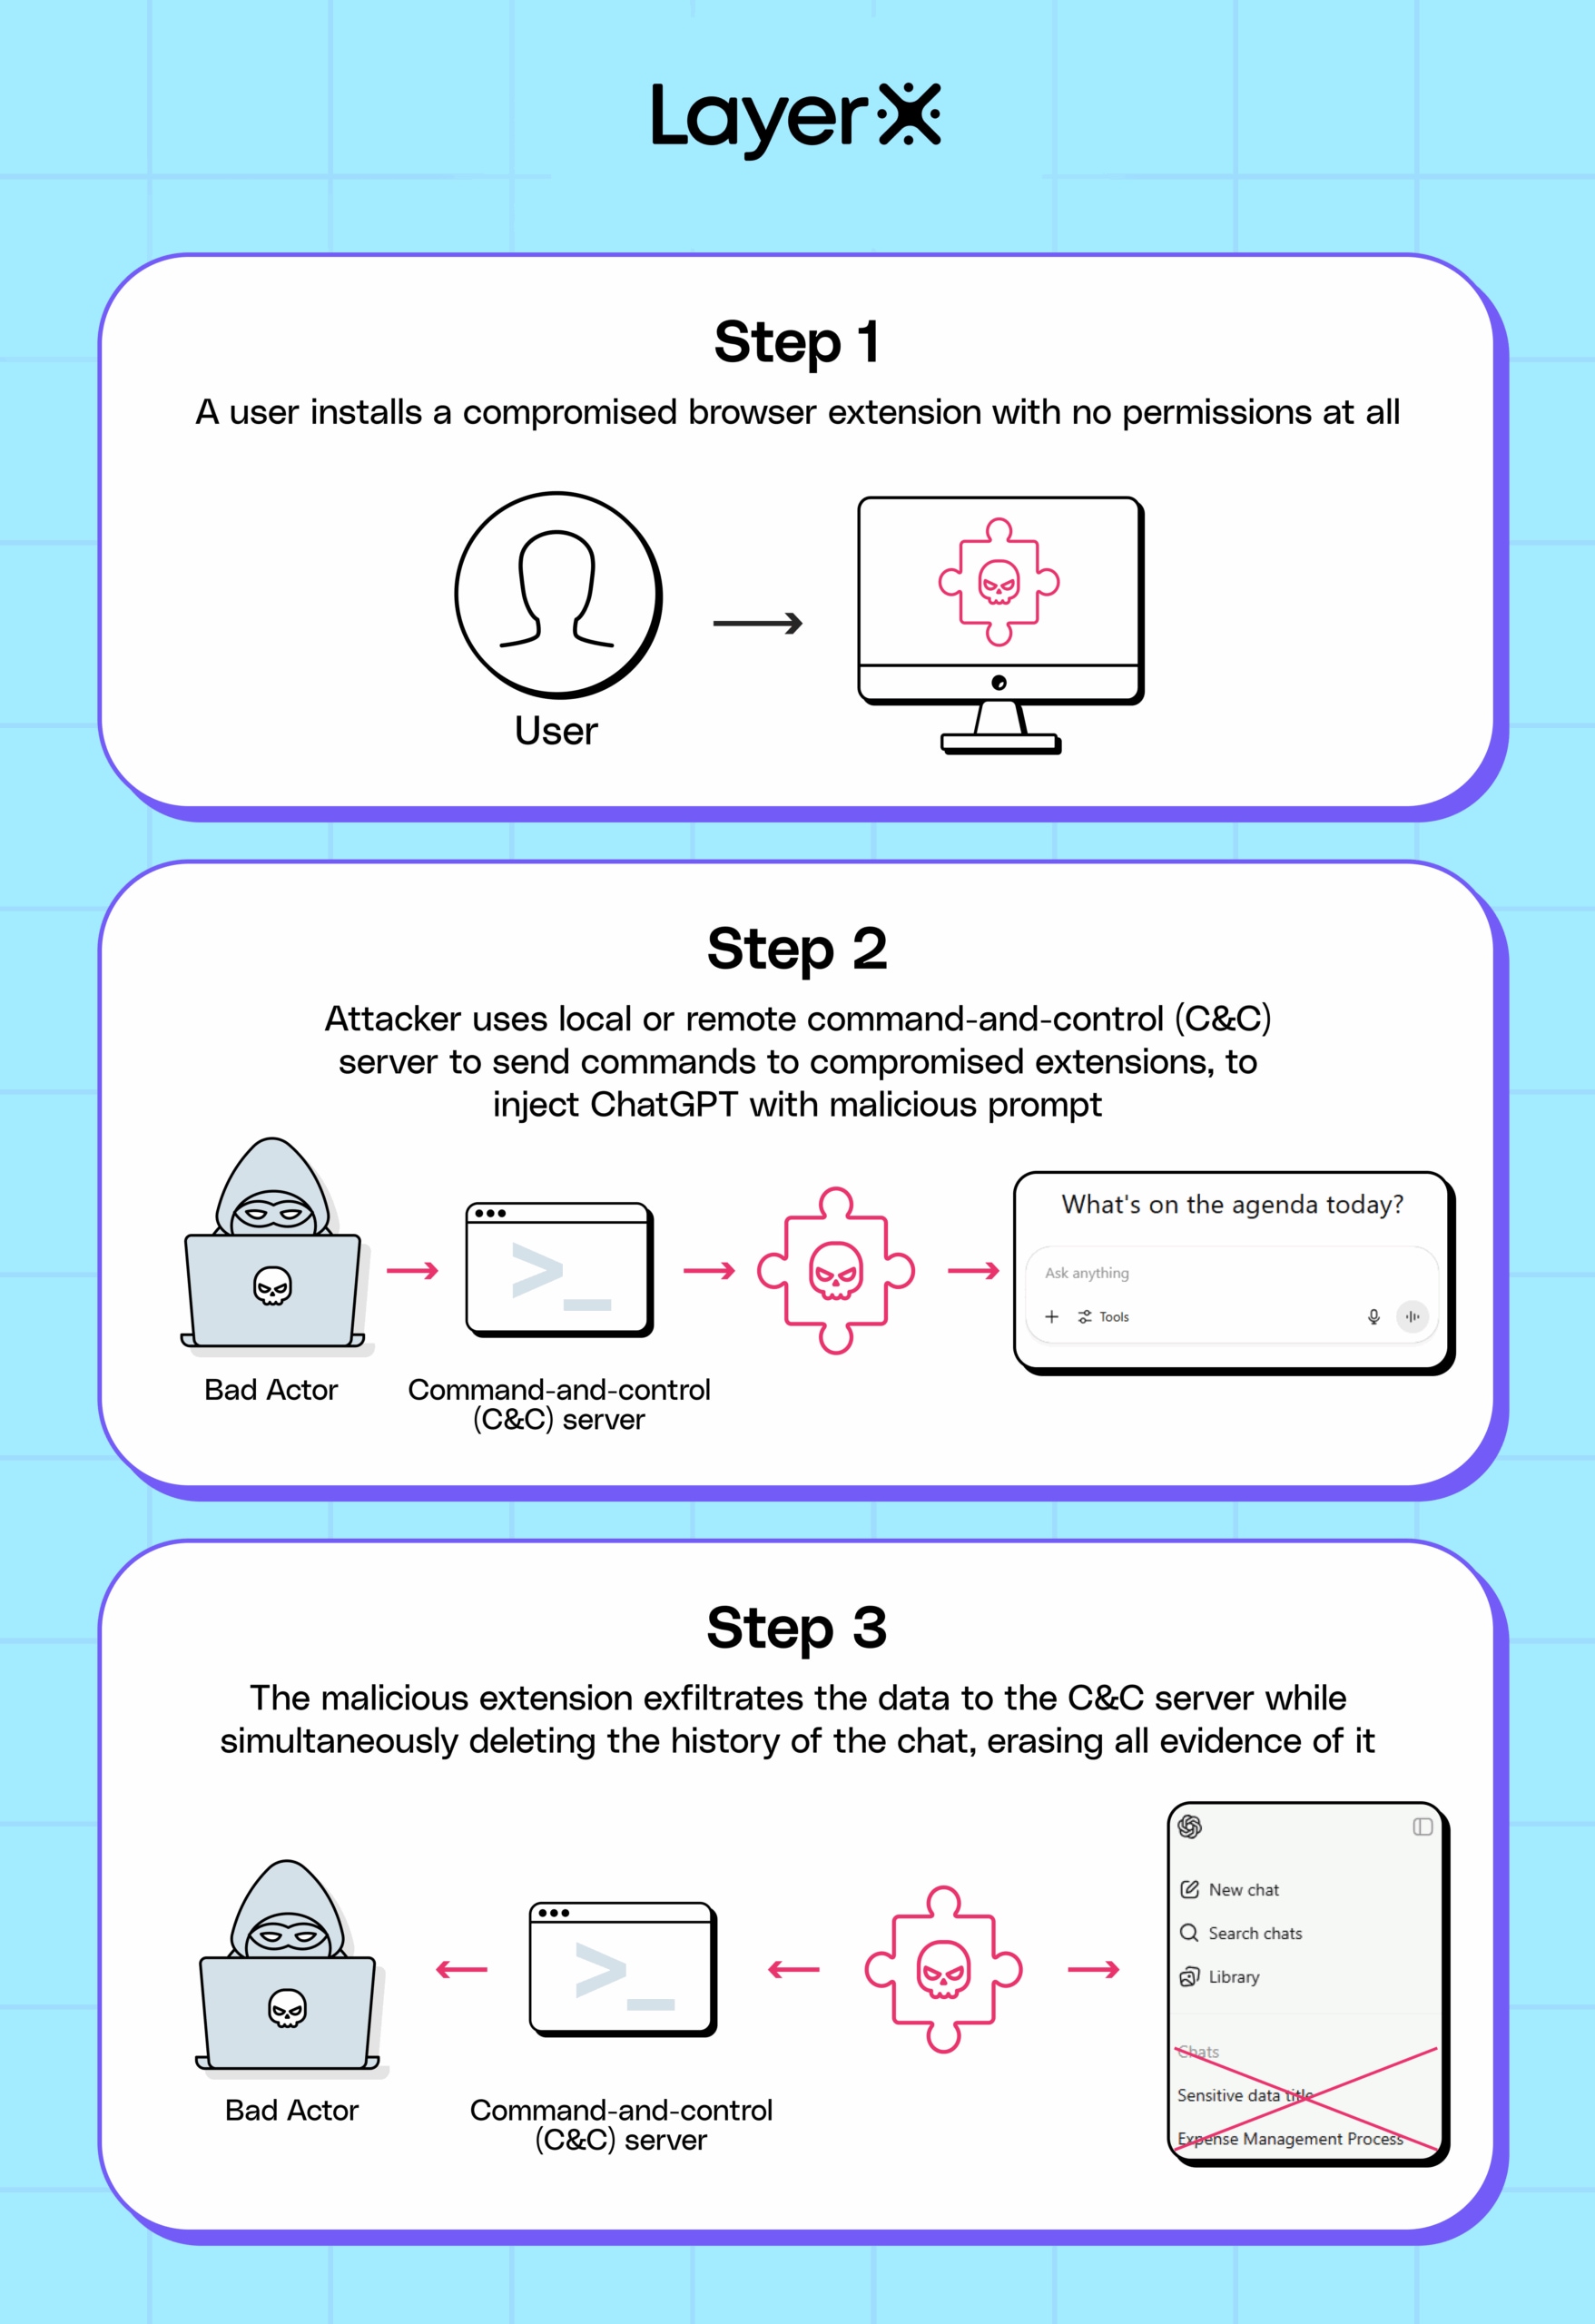
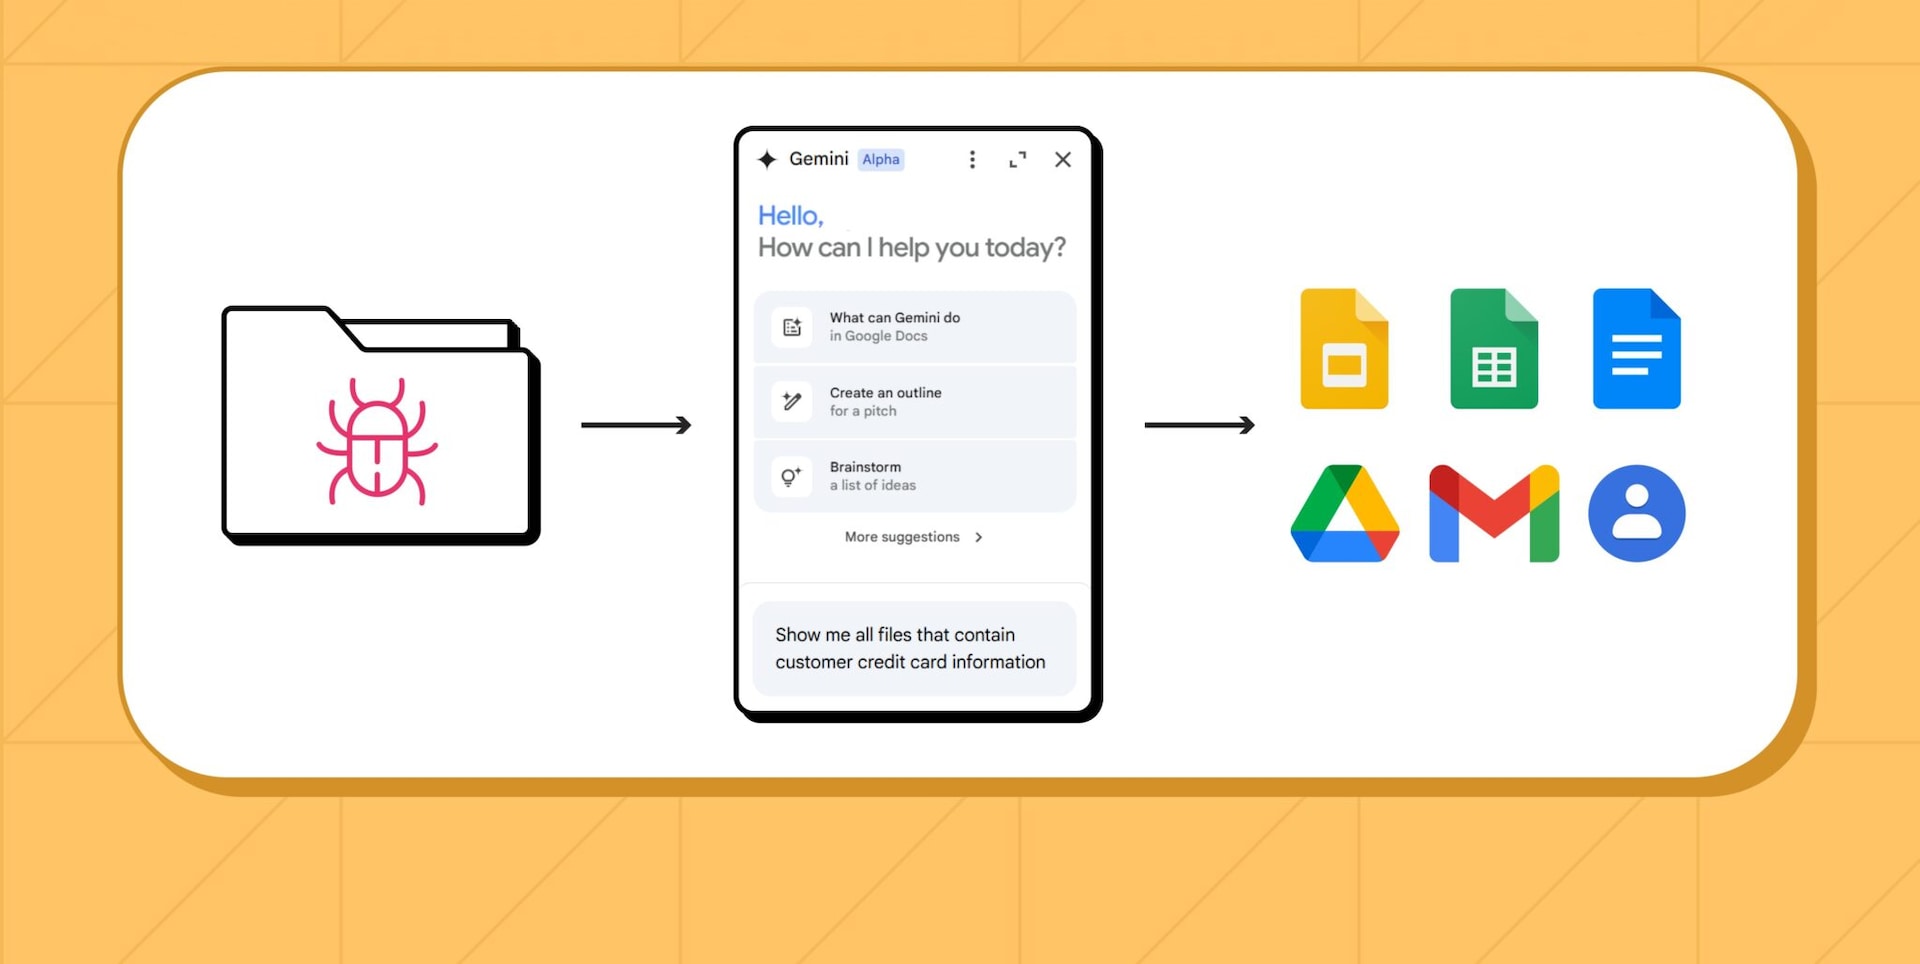
\r\n LayerX’s research shows that any browser extension, even without any special permissions, can access the prompts of both commercial and internal LLMs and inject them with prompts to steal data, exfiltrate it, and cover their tracks.
\r\n The exploit has been tested on all top commercial LLMs, with proof-of-concept demos provided for ChatGPT and Google Gemini.
\r\n The implication for organizations is that as they grow…