Preprint: https://arxiv.org/abs/2607.26390
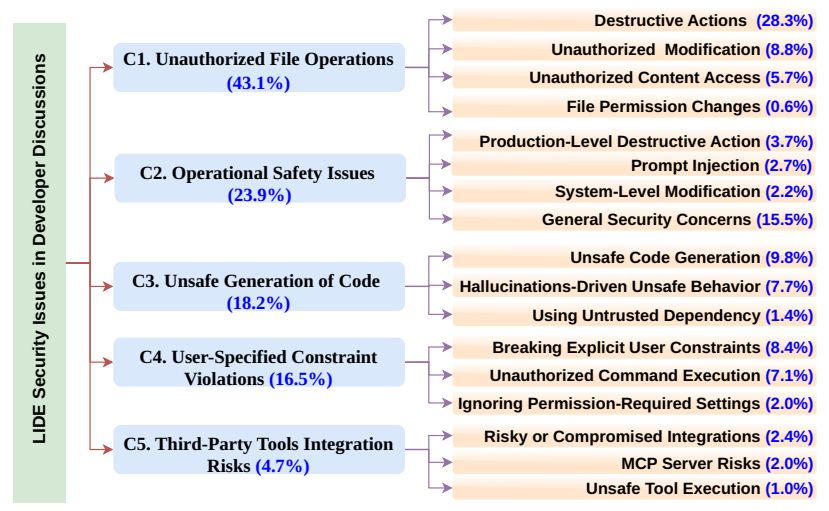
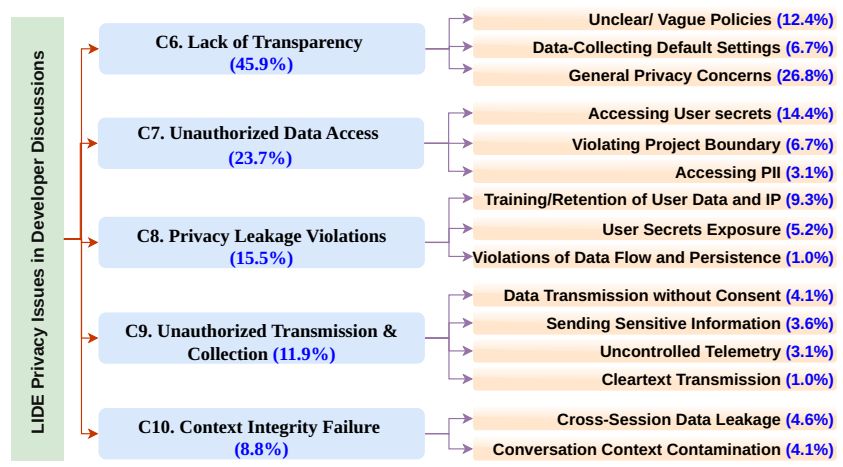
LLM-native IDEs (LIDEs) increasingly allow AI agents to read repositories, execute commands, and modify code, introducing significant security and privacy risks. Developers regularly report incidents on Reddit involving leaked API secrets, unauthorized access to system files, and file deletion on live servers. In one case, despite configuring both .gitignore and .copilotignore to exclude a secrets file, Copilot read and attempted to modify it while debugging a database connection issue, exposing live API keys and credentials. This study systematically analyzes such incidents and develops a taxonomy to characterize the reported security and privacy risks.
The authors followed a three-stage selection pipeline. First, they collected 15.4 million posts and comments from 46 subreddits related to LLM coding tools (January 2023–March 2026). Second, a high-recall LLM classifier filtered these to 3,801 candidate posts.…