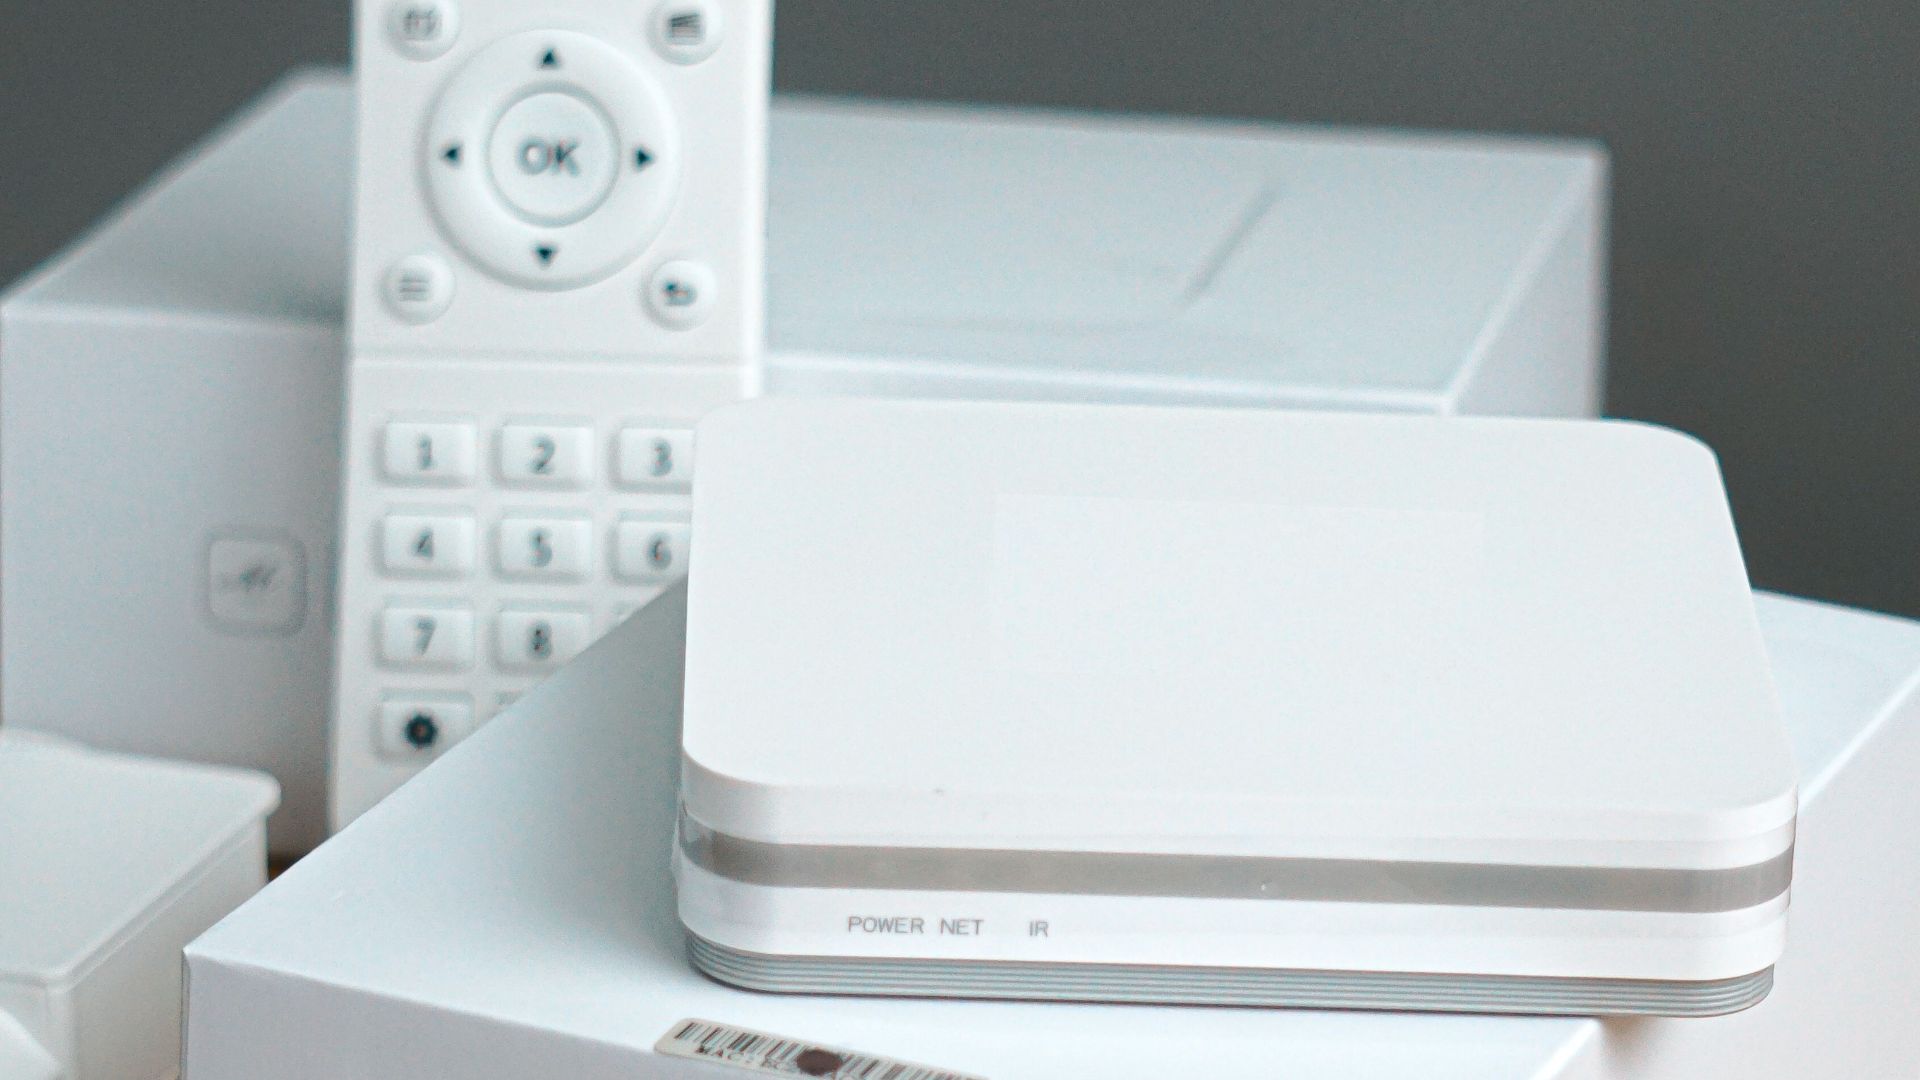
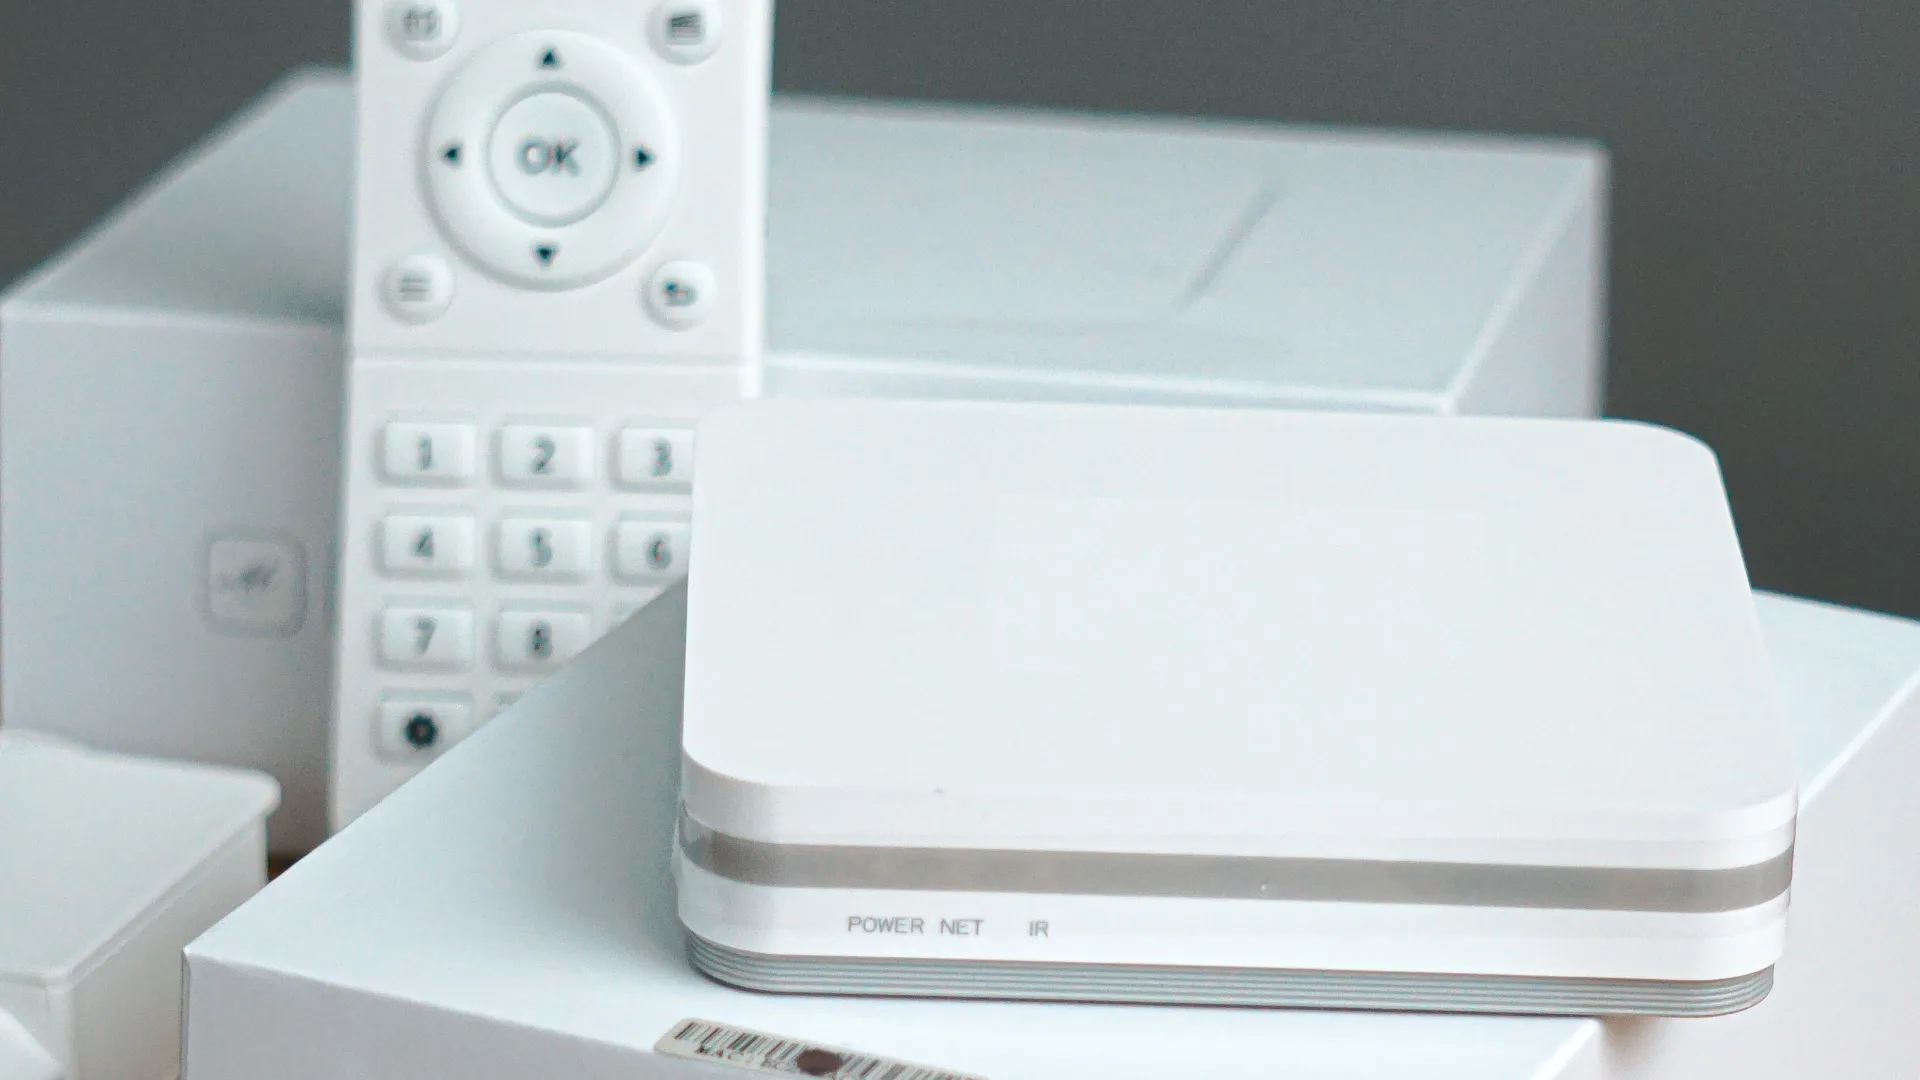
Google just shut down a massive botnet operation involving an OEM and ODM manufacturer. According to the company blog , Videostrong Technology Co., which was a certified Android TV partner, purposefully installed a backdoor into 1.3 million set-top boxes and then sold access to criminal affiliates. This allowed for the installation of hidden software that the bad actors could use to conduct ad fraud, build residential proxy networks, and even remotely install malware on the device itself to target the end-user.
“Videostrong monetized the backdoor by selling access to criminal affiliates and loading those affiliates’ malware modules onto infected devices,” the company said in the Google Cloud blog post. It also added, “We found this malicious software built directly into many different device models and brands over multiple years, supported by dedicated infrastructure and constantly evolving configurations to evade detection and manage their affiliates.…