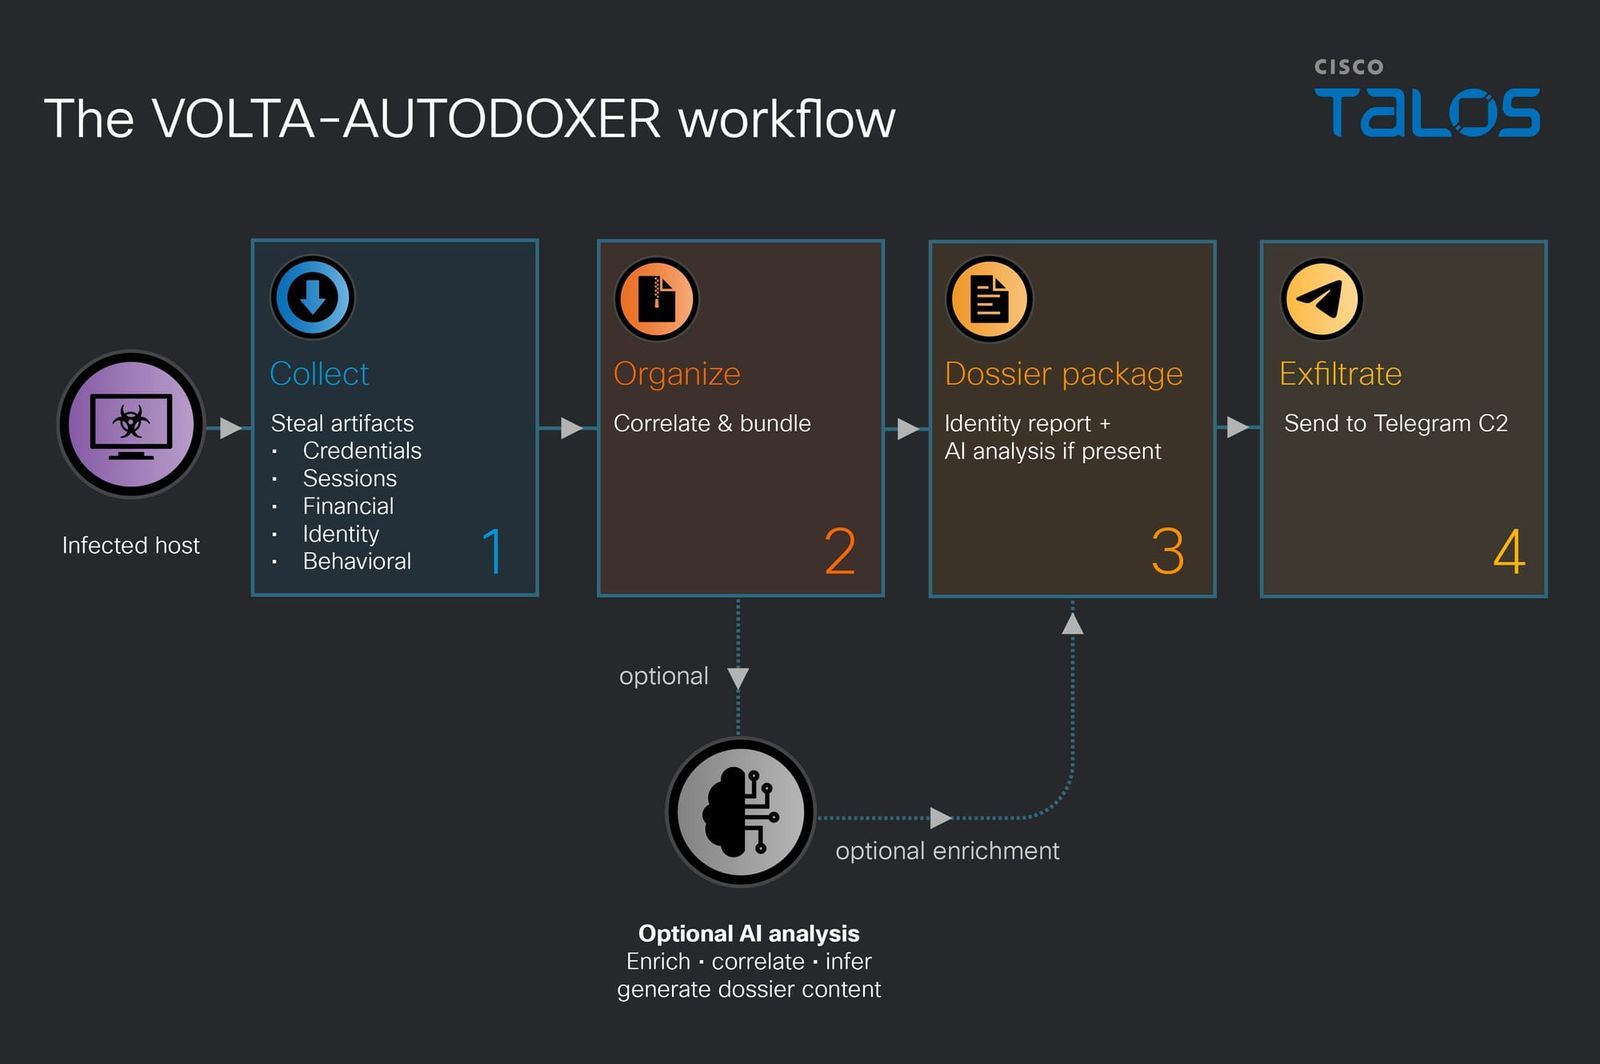
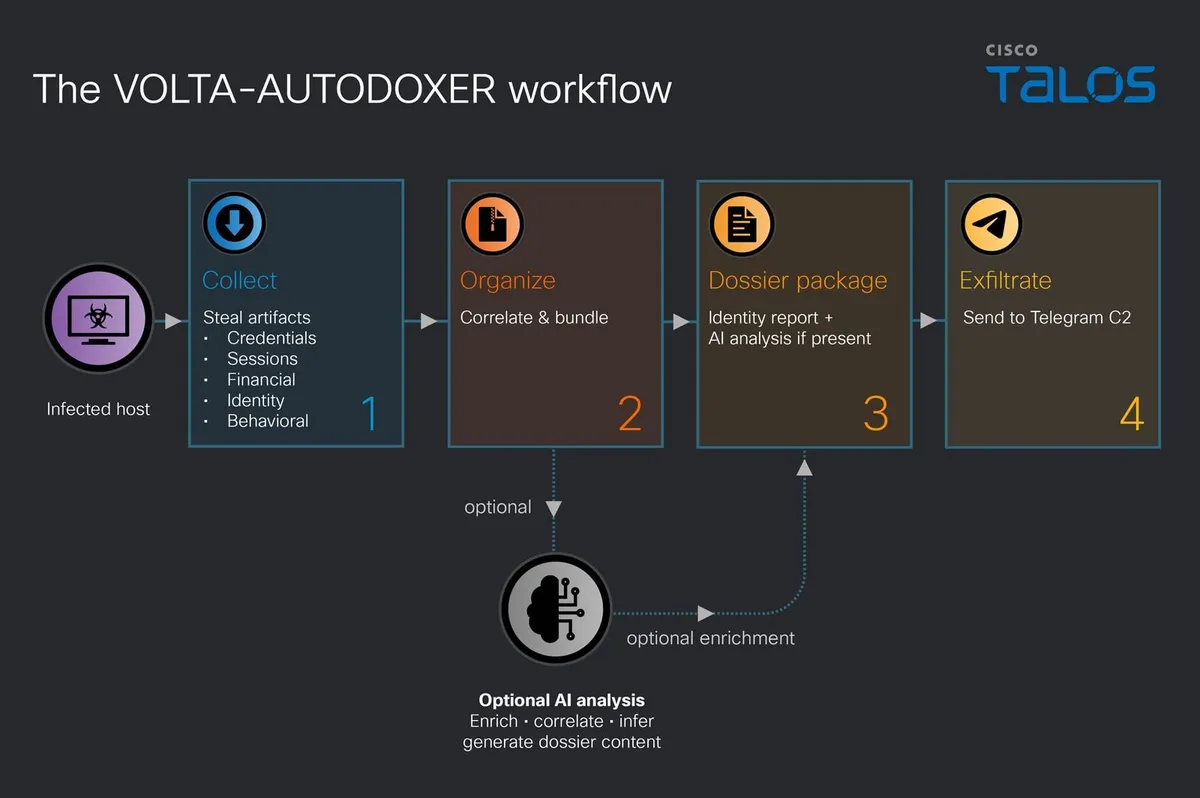
A self-deleting Windows infostealer that calls itself VOLTA-AUTODOXER steals everything it can from a victim’s PC, then asks an AI model, Anthropic’s Claude by default, to turn the haul into a target assessment, Cisco’s Talos research organization reports . The malware builds a structured “evidence bundle” on the person and asks the model for a list of their valuables ranked by how much they could be cashed out for, to see what’s worth the effort. VOLTA operates with a prompt to act as “a forensic intelligence analyst” and to be “blunt, specific, accurate,” and can switch models if one refuses, or even do without.
VOLTA steals browser passwords, cookies, and saved payment cards, Thunderbird and Outlook email profiles, Roblox accounts, Microsoft OAuth tokens, screenshots, and even SSH and cloud-provider configuration files. Every saved Wi-Fi password gets pulled in plaintext. Cryptocurrency wallets, when present, are not just copied, as the malware attempts to crack their vaults inline.…