Key takeaways
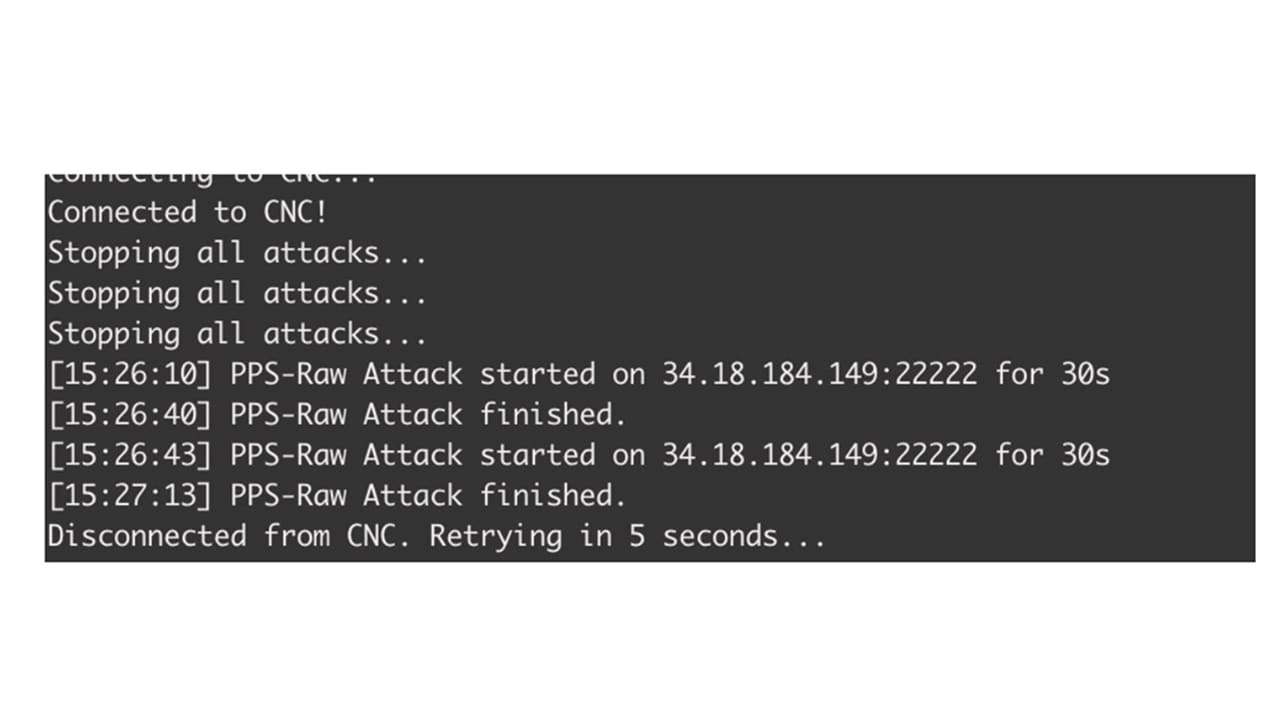
This Go-based Internet of Things (IoT) botnet combines an independently operating scanner with a command and control (C2) client, allowing it to both expand the botnet and receive attack instructions.
The malware uses multiple router vulnerabilities and an observed Langflow CVE-2026-33017 infection path to compromise additional devices.
Its Botnet_Methods package contains roughly 30 distributed denial-of-service (DDoS) techniques spanning volumetric, packet rate, game server, HTTPS, TLS, and evasion-oriented attacks.
Several of the malware’s capabilities are designed to make attack traffic harder to identify using static signatures, underscoring the need for behavioral threat intelligence and distributed DDoS mitigation.
What is this botnet capable of?
The sample we analyzed is a self-propagating IoT DDoS botnet written in Go.…