Serving tech enthusiasts for over 25 years.
TechSpot means tech analysis and advice you can trust .
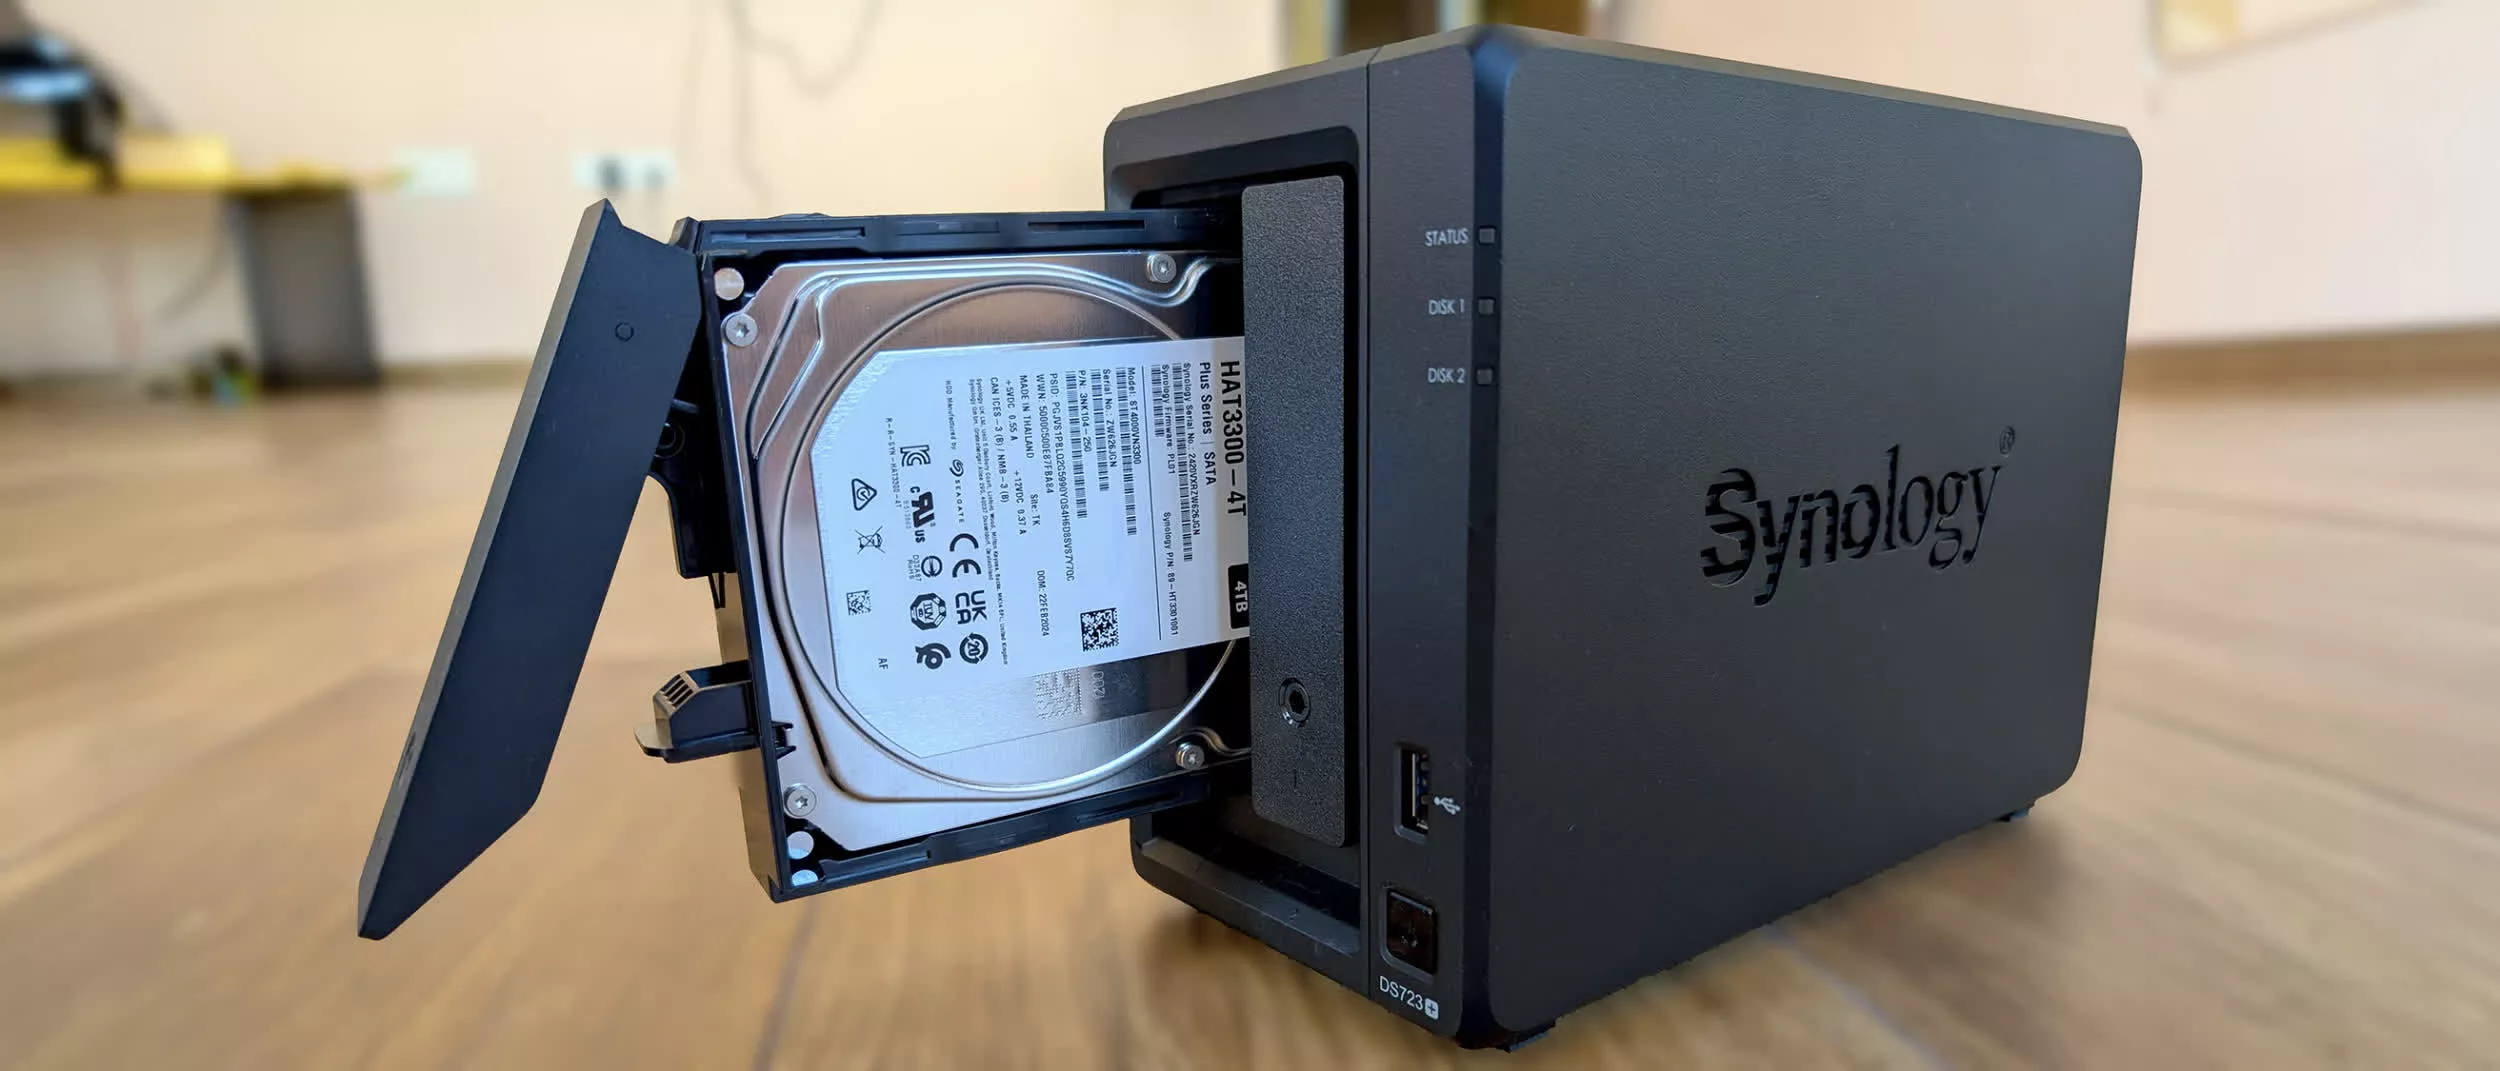
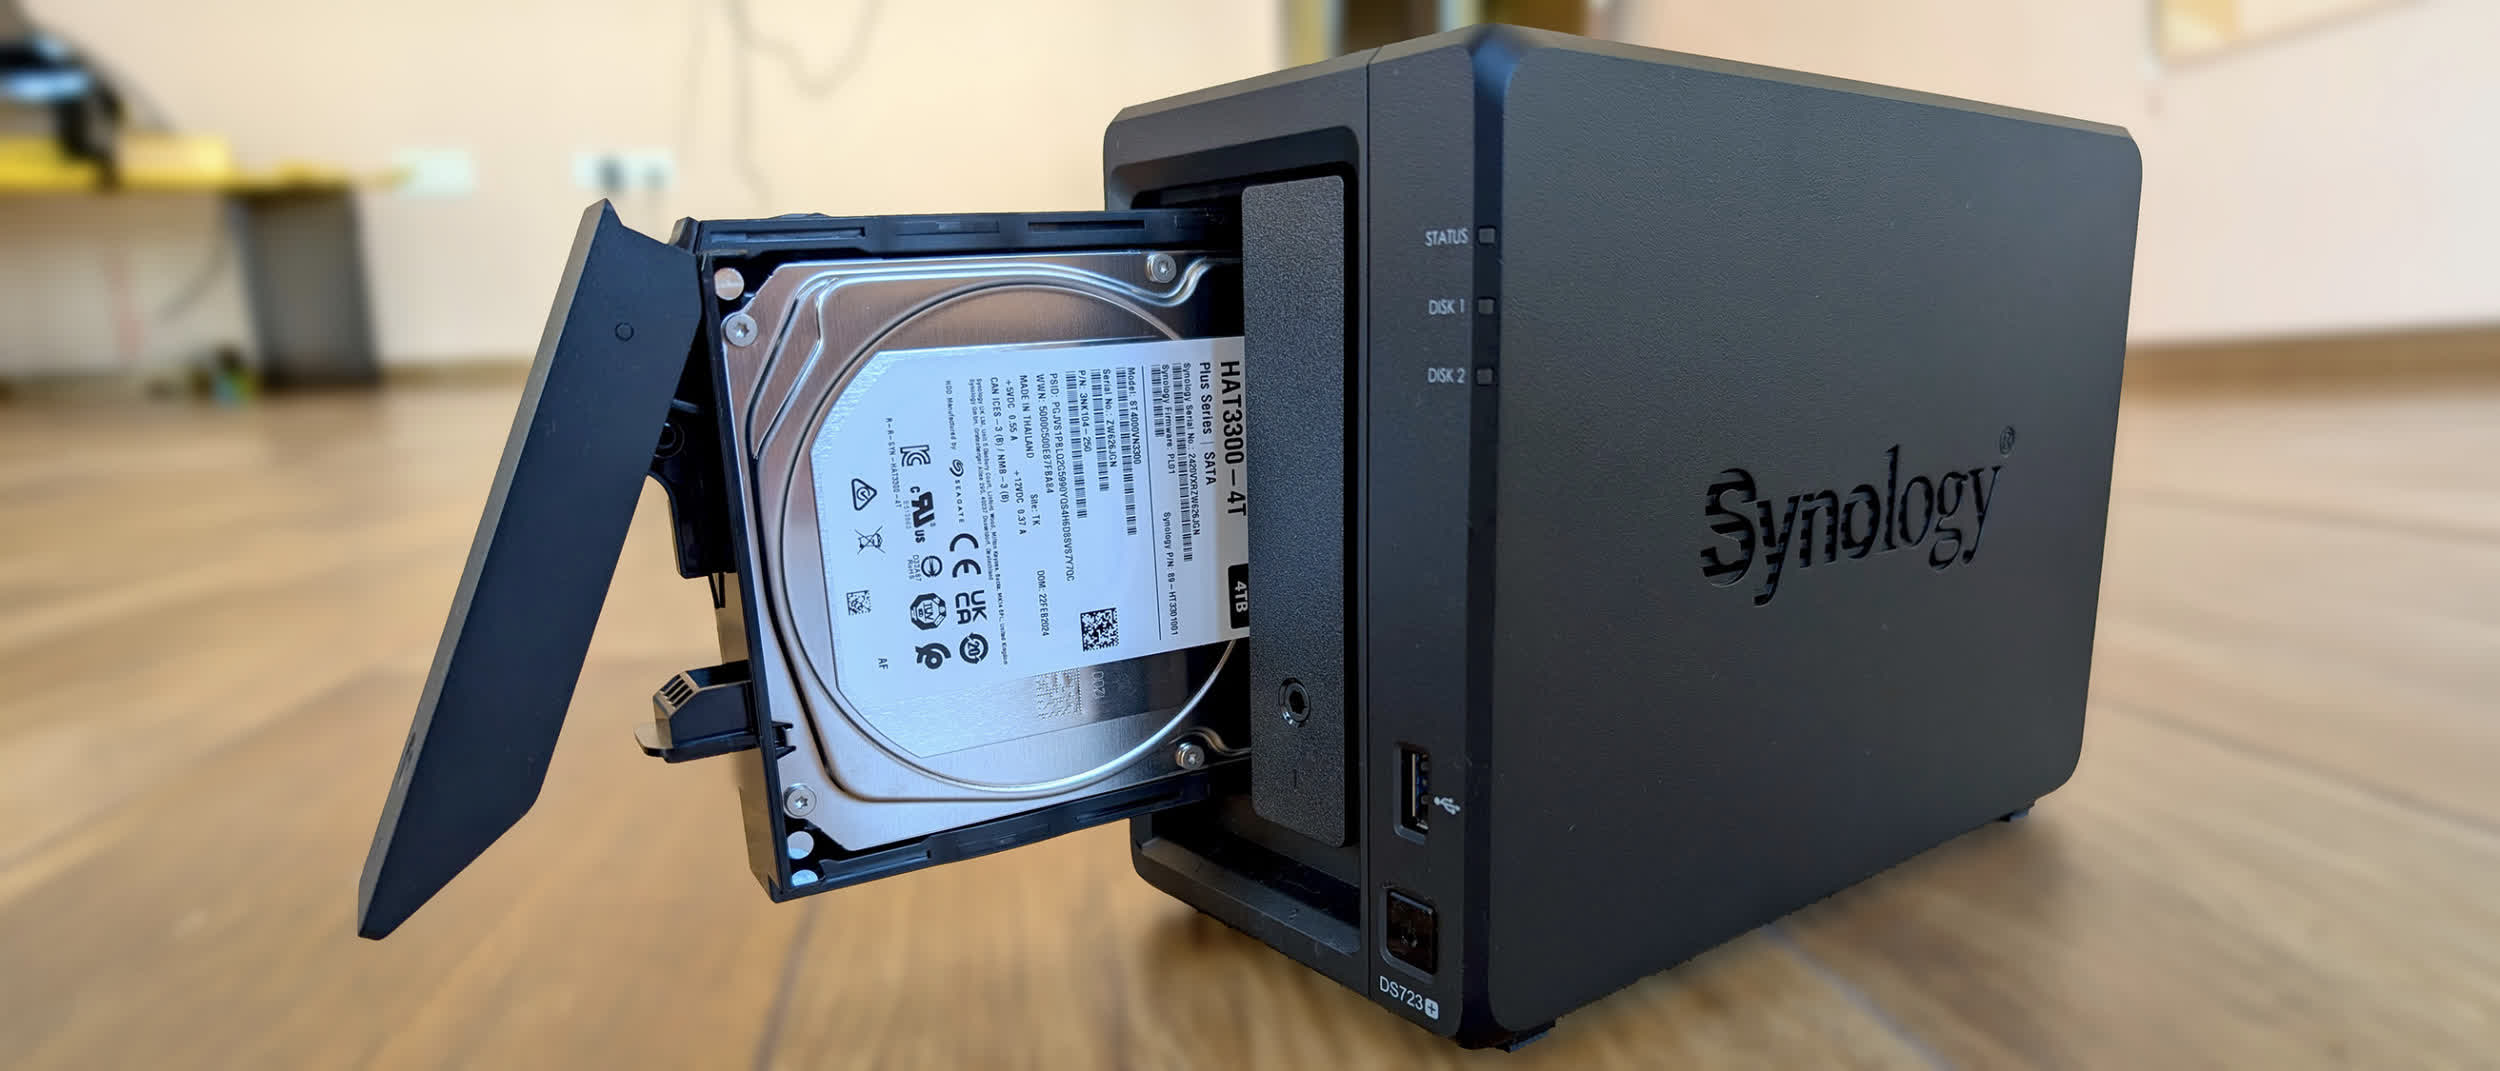
A hot potato: Despite recent controversies over its corporate policies, Synology still holds a large slice of the increasingly popular NAS market. When its devices are hit by dangerous security flaws, customers should take note. Hackers and cyber-criminals certainly will.
A newly published security advisory discloses two serious vulnerabilities in DiskStation Manager (DSM), the Linux-based OS used in Synology NAS products, one of them rated critical. The storage maker warned that the flaws could be abused to remotely access and attack vulnerable devices, giving cyber-criminals – or rogue AI agents, for that matter – an easy avenue to wreak havoc on users' data and local IT infrastructure.
Synology rates the SQL injection flaw "critical," with a 9.8 out of 10 score – the flaw could be abused to remotely access and attack vulnerable devices.
The advisory focuses on two vulnerabilities, tracked as…