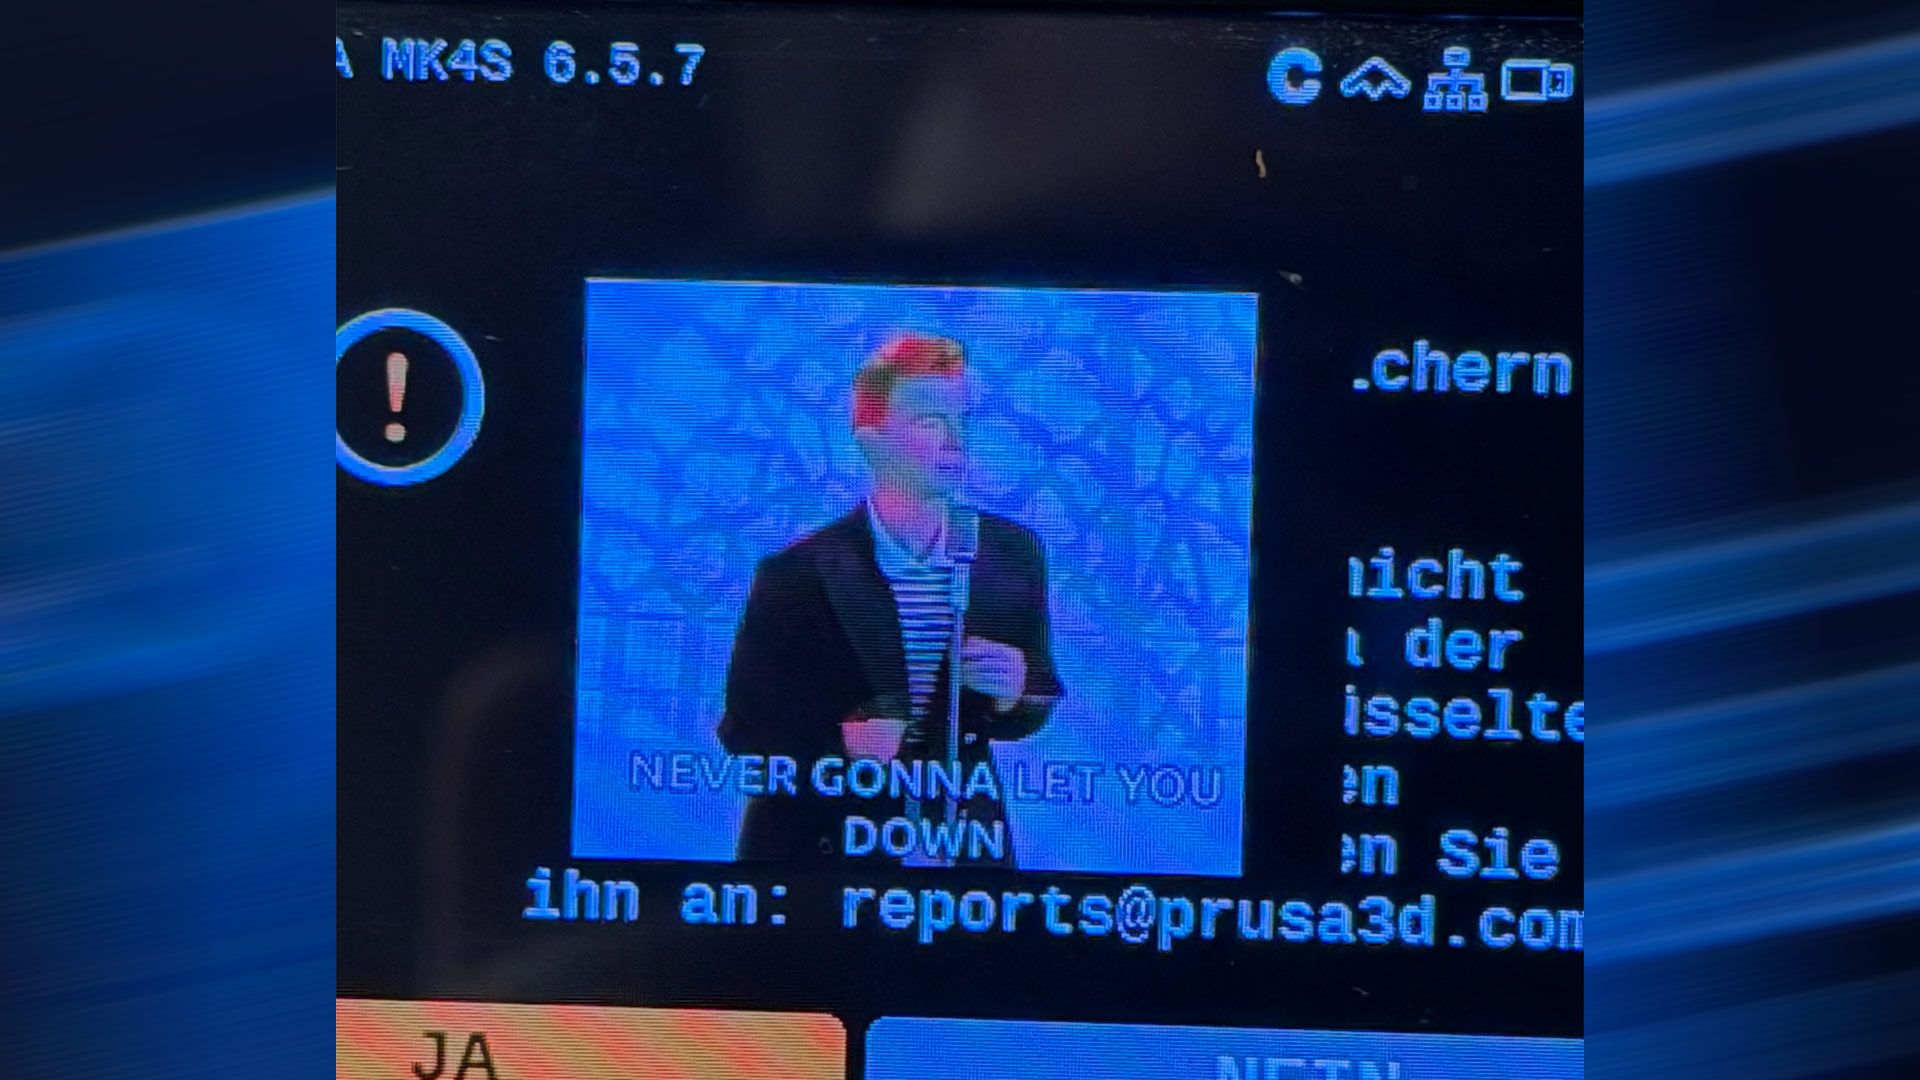
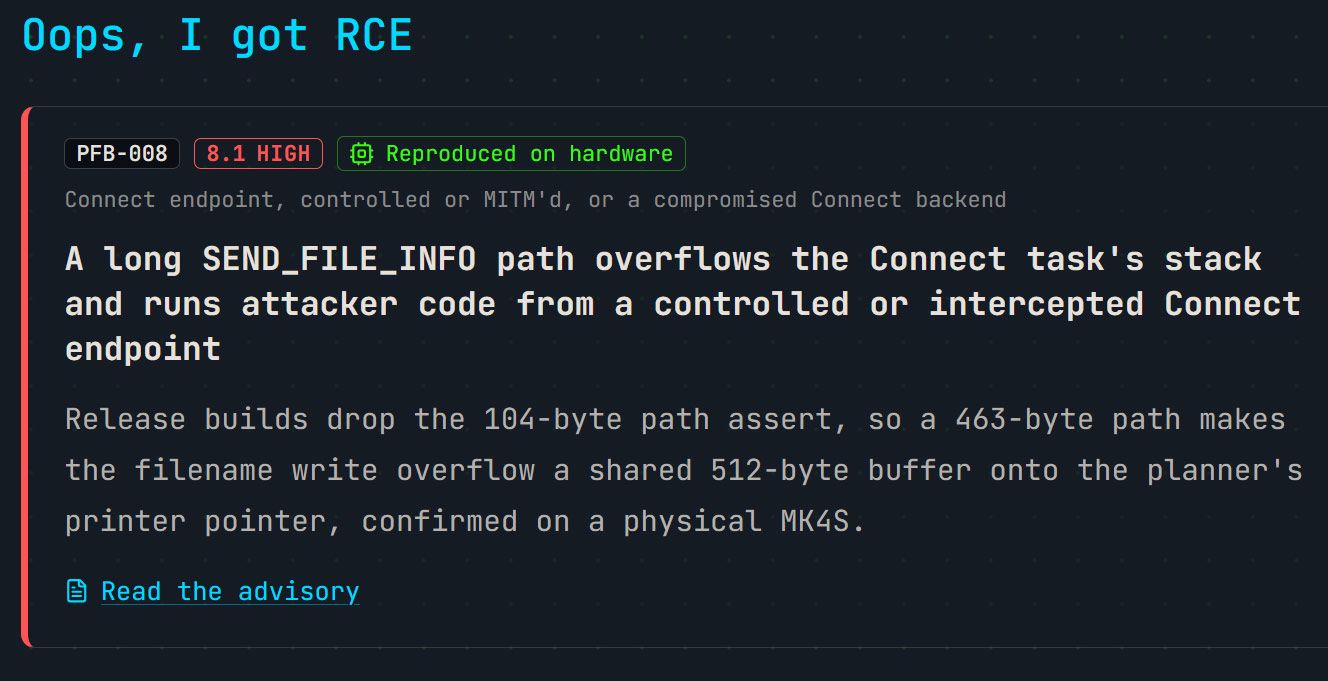
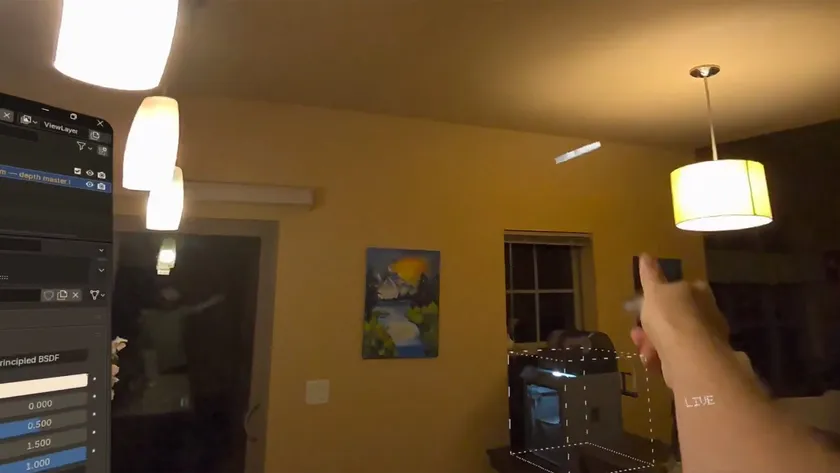Software engineer Yannick Dixken spent a week attacking his Prusa MK4S 3D printer in the name of science. At the end of the relatively short but intense period, he produced a video demonstrating the ability to Rickroll the printer via remote code execution (RCE). Dixken shared the video and findings – charting “roughly 23 individual defects” with Prusa and published his amusing but detailed Never gonna print you up! blog in coordination with the 3D printer maker. Yes, all the vulnerabilities are now patched in the Buddy firmware versions >7.0.0.
Get Tom's Hardware's best news and in-depth reviews, straight to your inbox.