Key takeaways
DNS over HTTPS (DoH) is now a core privacy control, encrypting DNS queries inside HTTPS to prevent interception, manipulation, and mass surveillance.
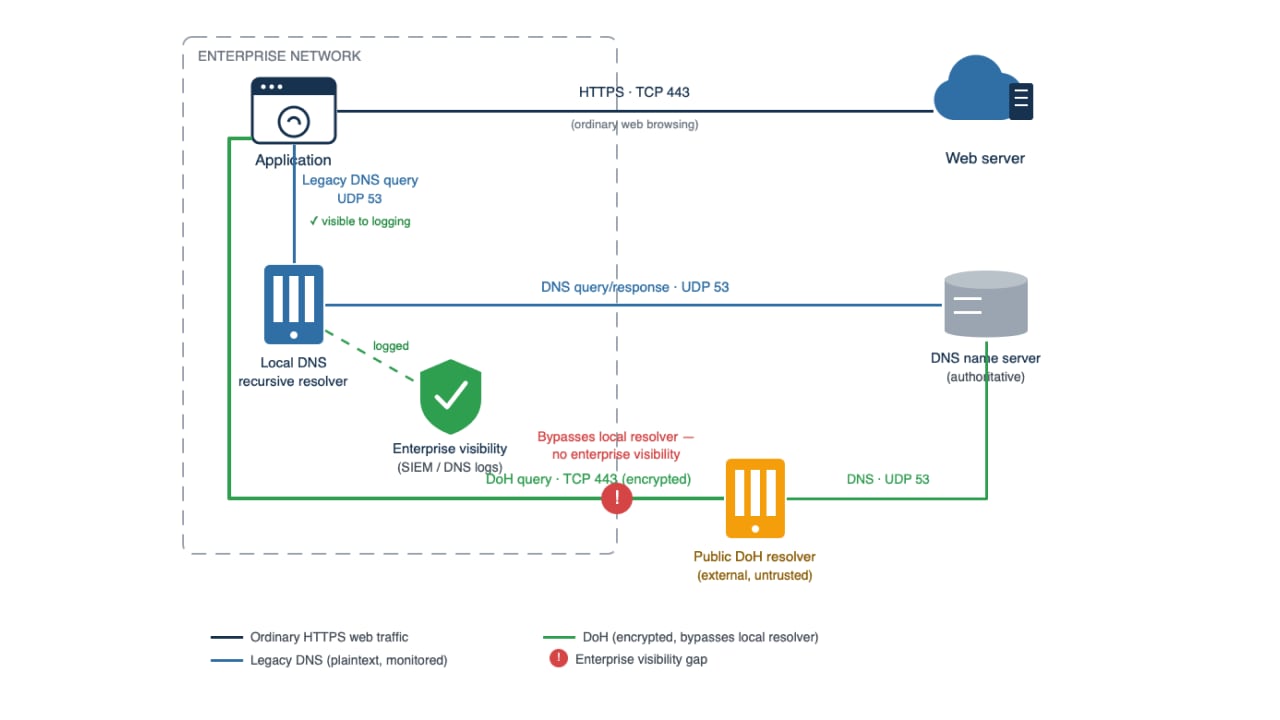
The same encryption that protects users also masks defenders. DoH makes DNS traffic look like normal web traffic and bypasses legacy DNS and network security controls focused on port 53.
Simply blocking DoH is not a sustainable strategy as operating systems and browsers increasingly default to encrypted DNS, and privacy expectations keep growing.
The right approach is to take back control of DoH.
Encrypted DNS (DoT, DoH, DoQ): Essential privacy, new visibility gaps
DNS over TLS (DoT) and DNS over HTTPS (DoH) were introduced as Internet Engineering Task Force proposed standards in May 2016 and October 2018, respectively, to address the surveillance and spoofing risks of unencrypted DNS.…