Blog
Security Research
Coyote in the Wild: First-Ever Malware That Abuses UI Automation
Tomer Peled is a Security Researcher at Akamai. In his daily job, he conducts research ranging from vulnerability research to OS internals. In his free time, he likes to cook, do Krav Maga, and game on his PC.
This UIA abuse is the latest of these malicious Coyote tracks in their digital habitat since its discovery in February 2024.
Executive summary
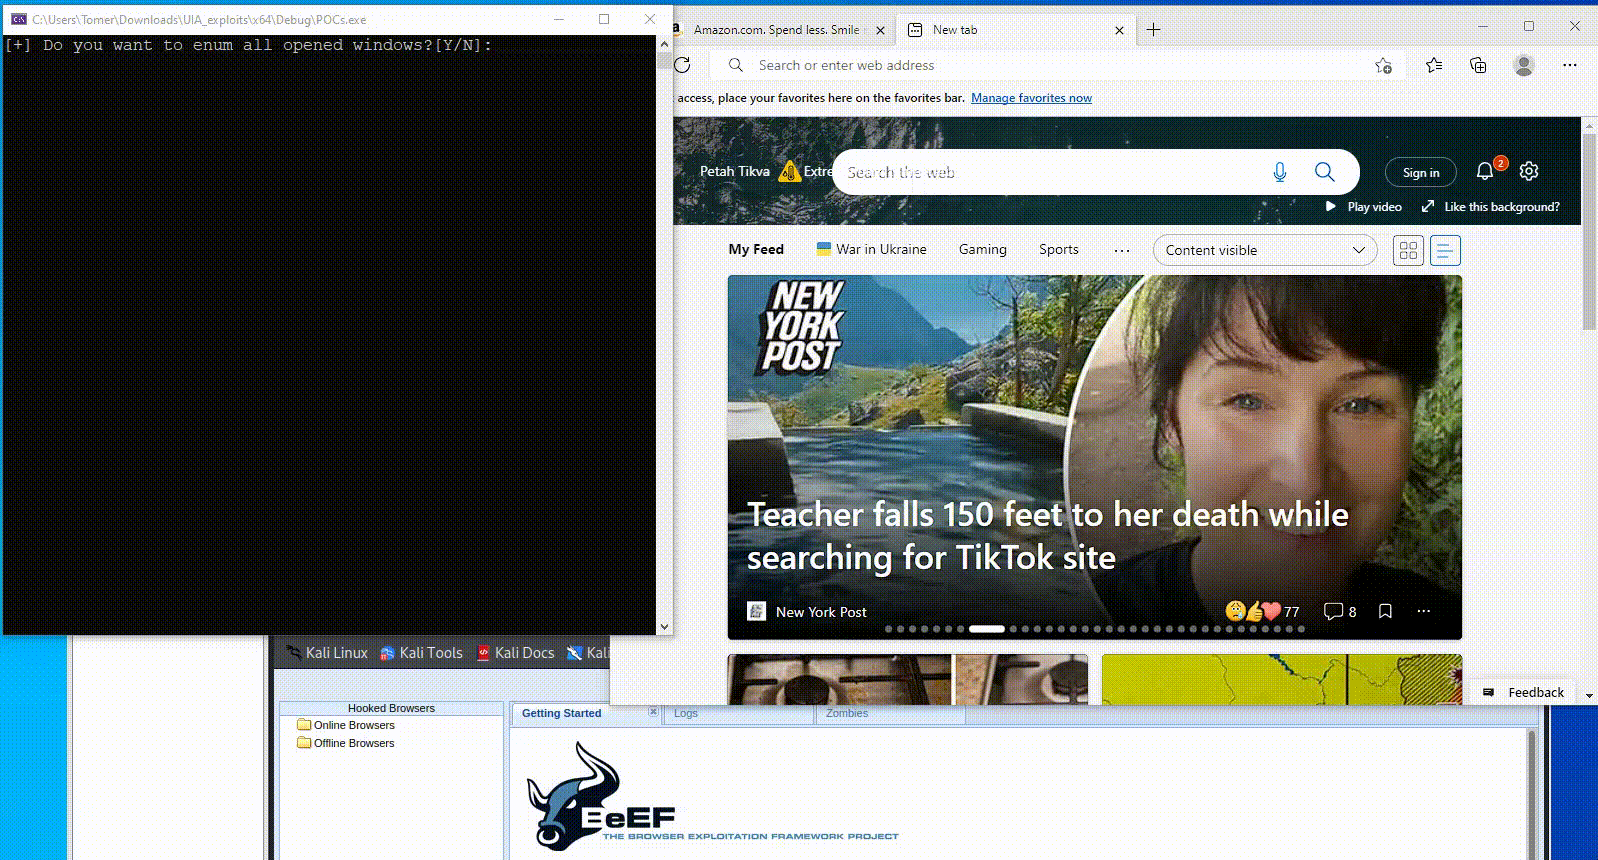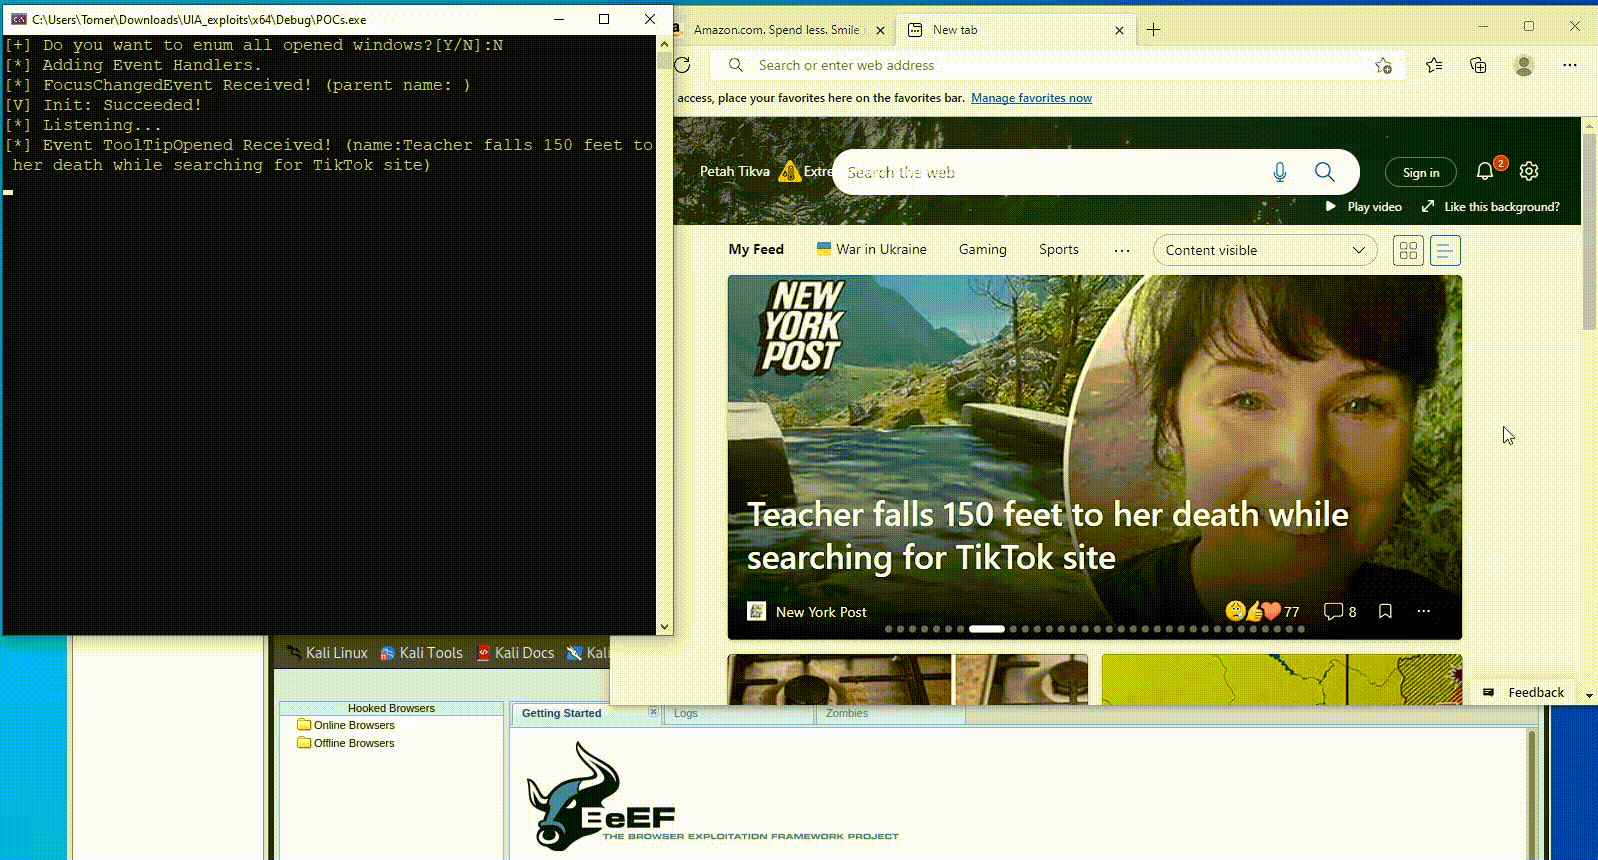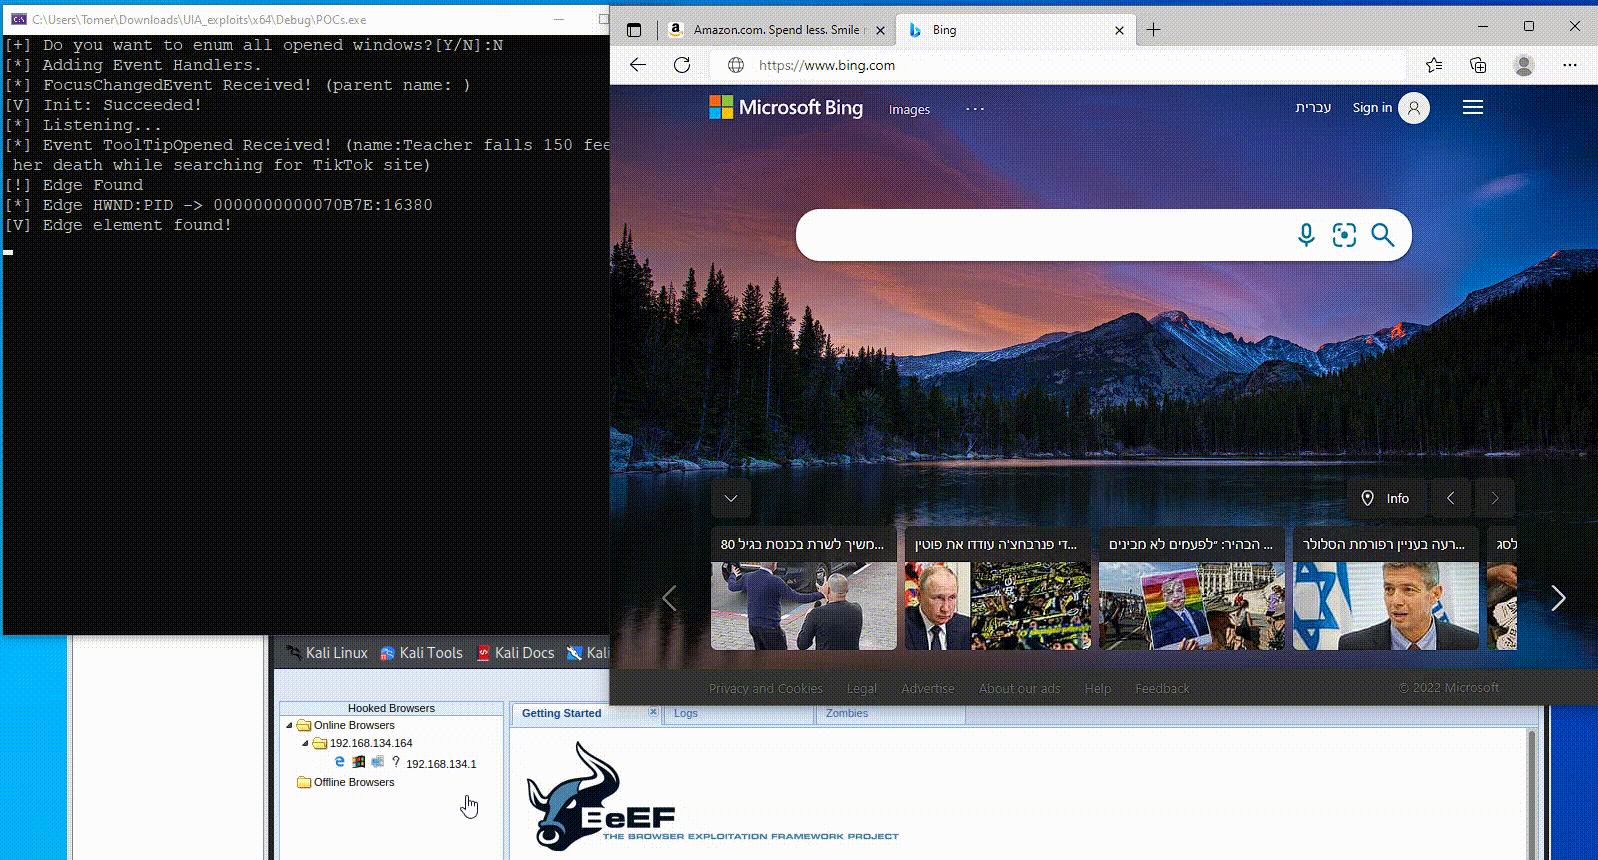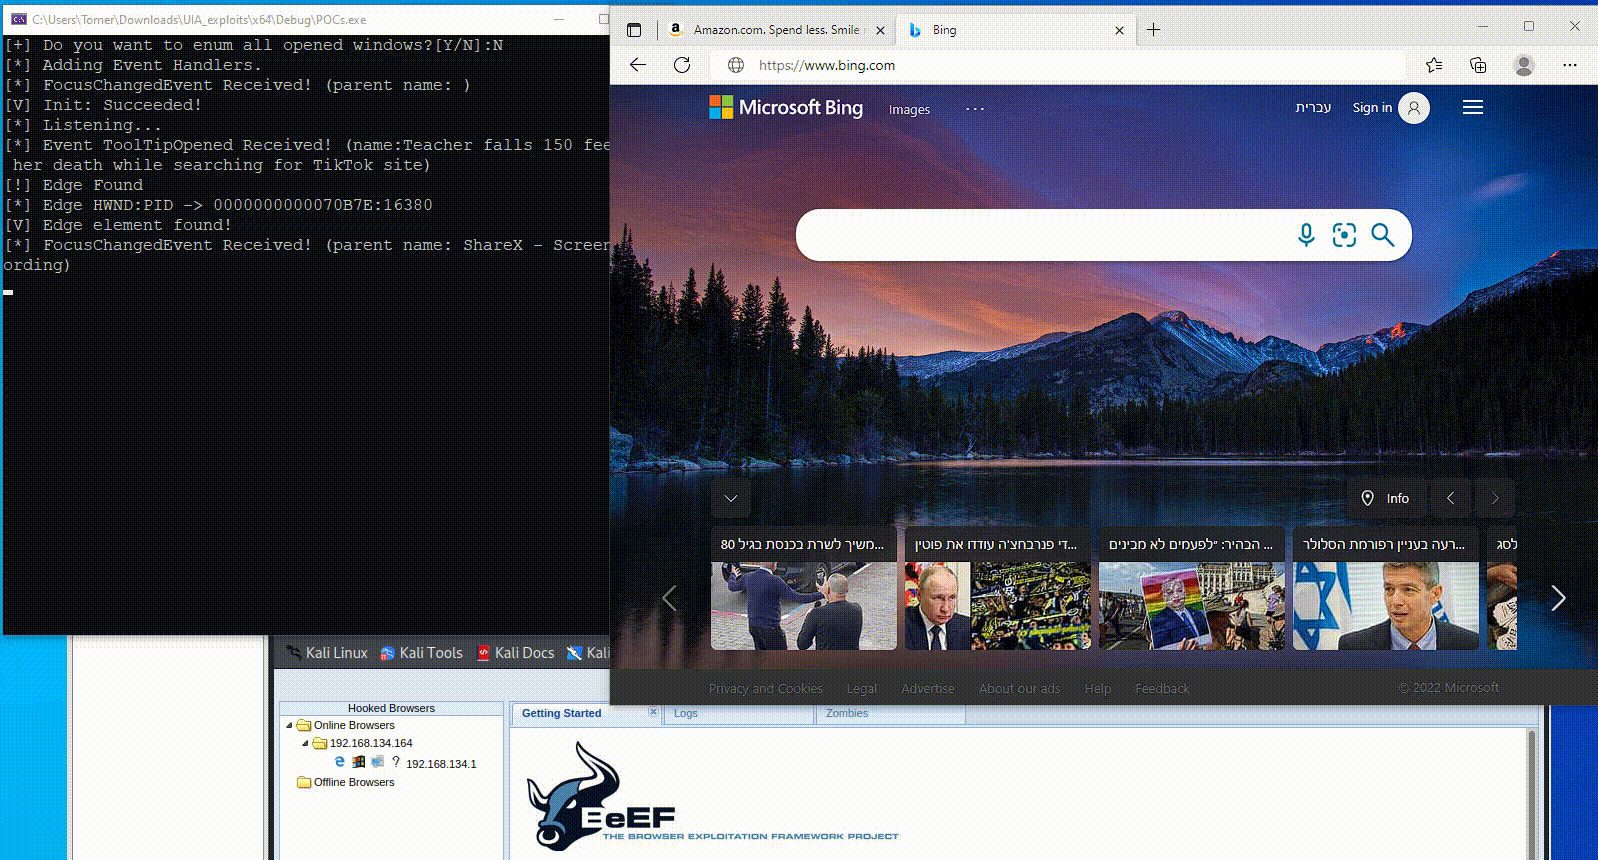
\r\n Akamai researchers previously outlined the potential for malicious use of UIA.
\r\n
\r\n Now, Akamai researchers have analyzed a new variant of the Coyote malware that is the first confirmed case of maliciously using Microsoft’s UI Automation (UIA) framework in the wild .
\r\n
\r\n The new Coyote variant is targeting Brazilian users, and uses UIA to extract credentials linked to 75 banking institutes’ web addresses and cryptocurrency exchanges.
\r\n
\r\n To help prevent Coyote infections and UIA abuse more broadly, we’ve included indicators of…