
Menu

1 / 5

OMB M-26-14 Compliance: Adaptive Edge Logging for Federal CISOs

Blog·Kendrick Daniel·6 days ago
#Q277zB6f
Reading 0:00
15s threshold

Key takeaways

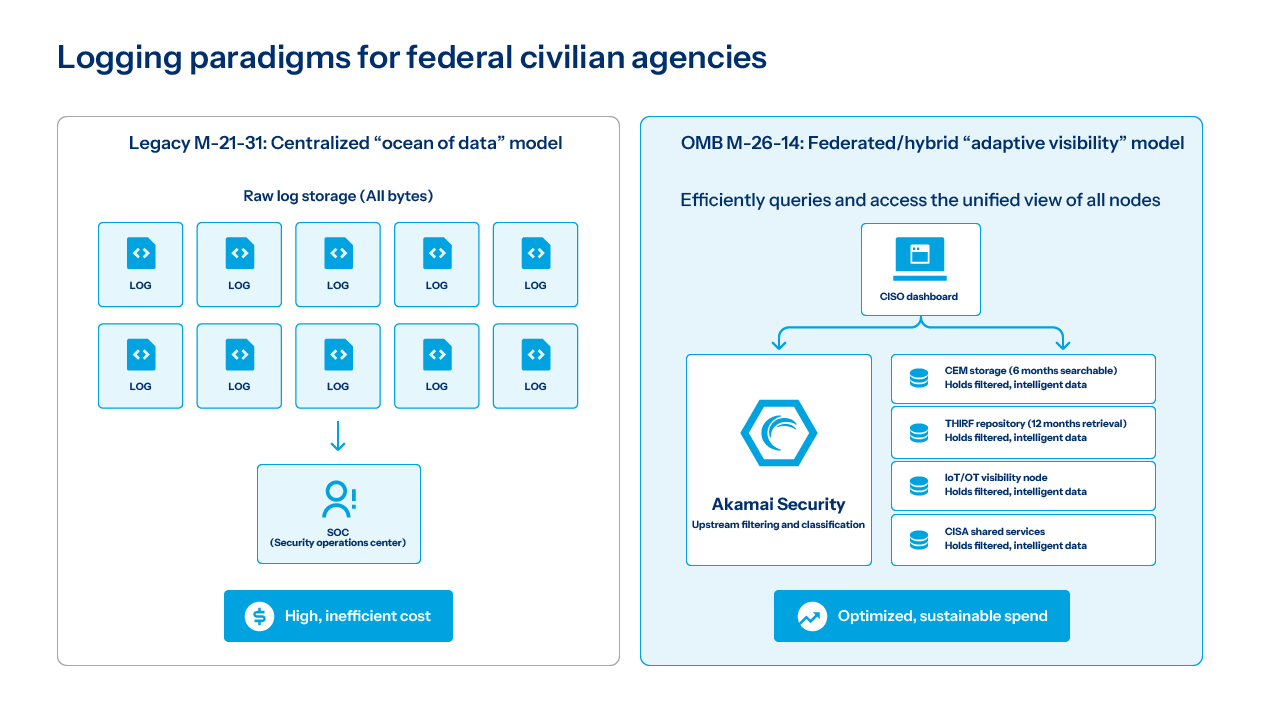
OMB M-26-14 officially rescinds M-21-31 , replacing the requirement to hoard all raw log data with a flexible, risk-based maturity model. This transition helps agencies adapt to tightening fiscal constraints, including a 10% nondefense spending cut for fiscal year 2027 (FY27).

Compliance is now divided into two distinct operational goals: Continuous Event Monitoring (CEM; real-time detection that’s searchable for 6+ months) and threat hunting, investigation, response, and forensics (THIRF; long-term data that’s retrievable for 12+ months).

Agencies are no longer required to pump all raw data into central repositories.…

Continue reading — create a free account

Join HashtagPLUS to read full articles, follow hashtags, vote, and join the conversation.