Akamai acquired LayerX. This previously published blog post reflects the product and feature names on the original date of publication.
Executive Summary
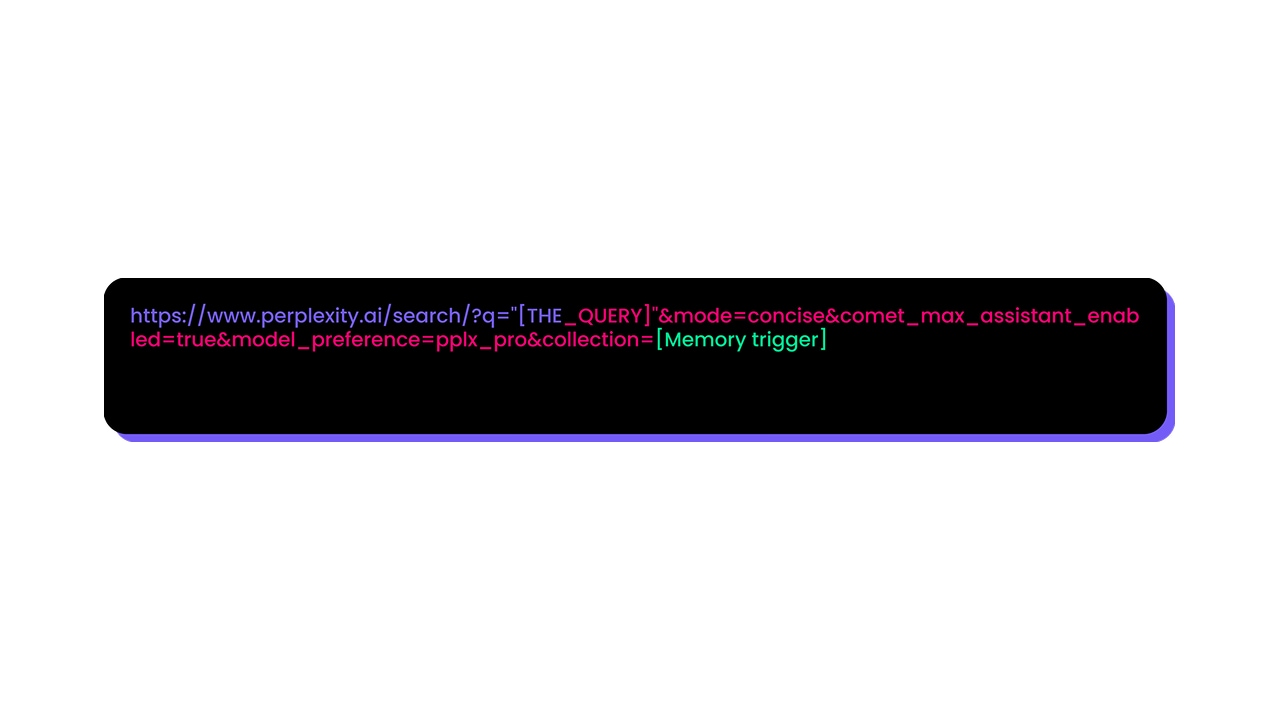
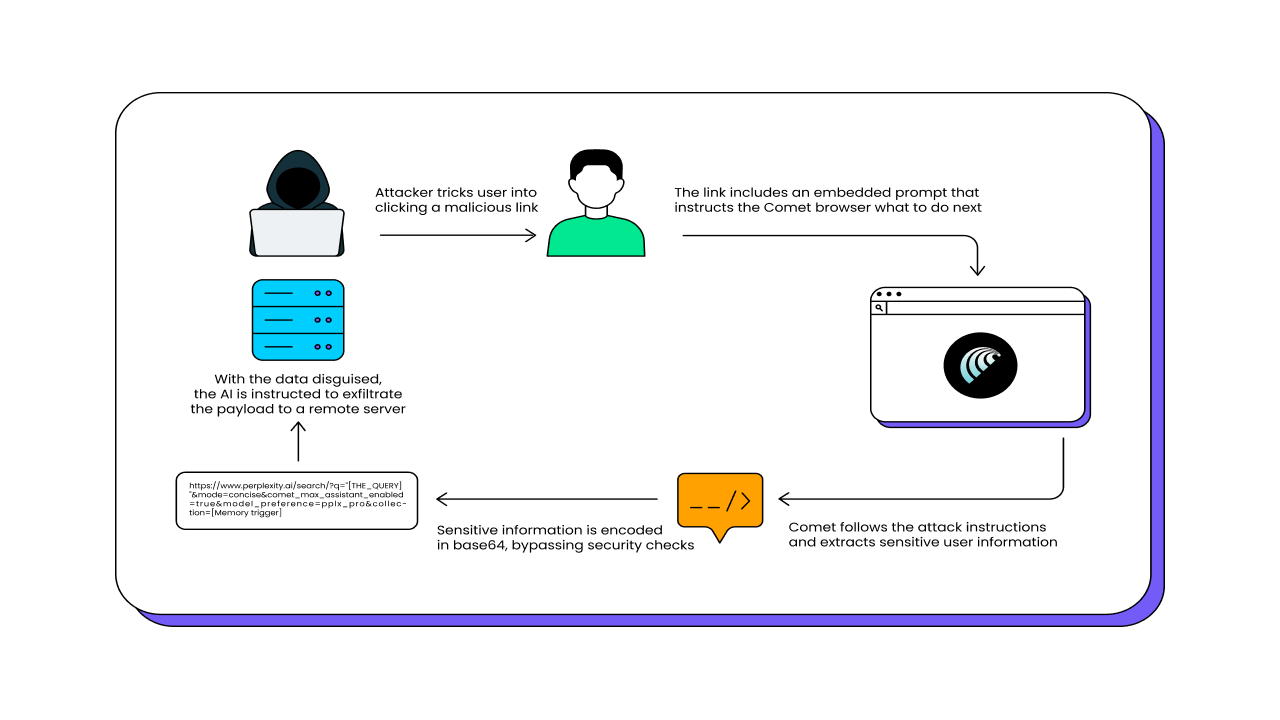
New research by LayerX shows how a single weaponized URL, without any malicious page content, is enough to let an attacker steal any sensitive data that has been exposed in the Comet browser.
\r\n For example, if the user asked Comet to rewrite an email or schedule an appointment, the email content and meeting metadata can be exfiltrated to the attacker.
\r\n An attacker only needs to get a user to open a crafted link, which can be sent via email, an extension, or a malicious site, and sensitive Comet data can be exposed, extracted, and exfiltrated.
\r\n"}}"> New research by LayerX shows how a single weaponized URL, without any malicious page content, is enough to let an attacker steal any sensitive data that has been exposed in the Comet browser.
For example, if the user asked Comet to rewrite an email or schedule an appointment, the email…