Key takeaways
On October 20, 2026, PHP announced that they would release a patch on October 21 at 14:00 UTC for two critical vulnerabilities.
These vulnerabilities are called PHP2Shell because they allow an attacker to achieve remote code execution (RCE).
The details were scheduled to be disclosed on October 22, but information about the vulnerabilities, including their CVE IDs ( CVE-2026-109619 and CVE-2026-109618 ), was leaked early.
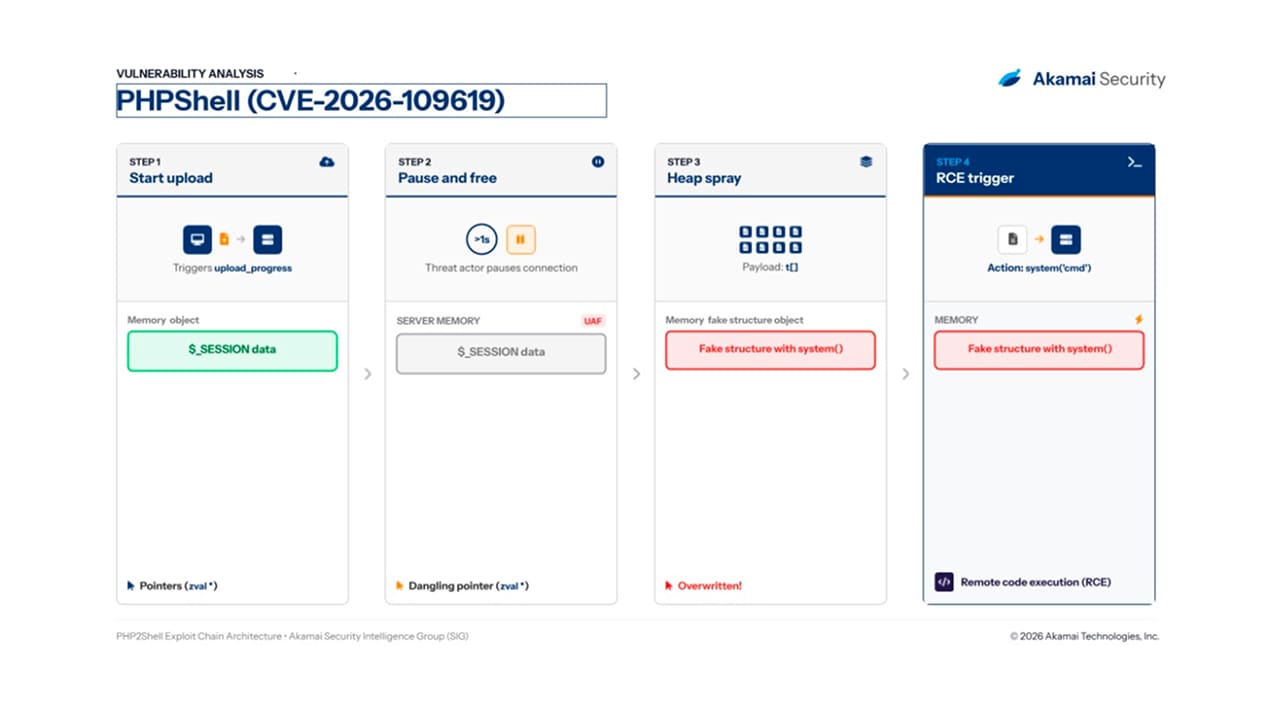
CVE-2026-109619 is a use-after-free (UAF) vulnerability in PHP core's upload progress feature.
CVE-2026-109618 is a memory corruption vulnerability triggered by an out-of-memory (OOM) condition.
This blog post provides the full details behind these two vulnerabilities.
Prerequisites for an attack
\r\n The target runs PHP 5 onward with session.upload_progress.enabled = On (the default)
\r\n
\r\n For any endpoint that accepts file uploads (even one that ignores them): PHP's session layer processes the upload progress before userland code runs
\r\n
\r\n Attackers need…