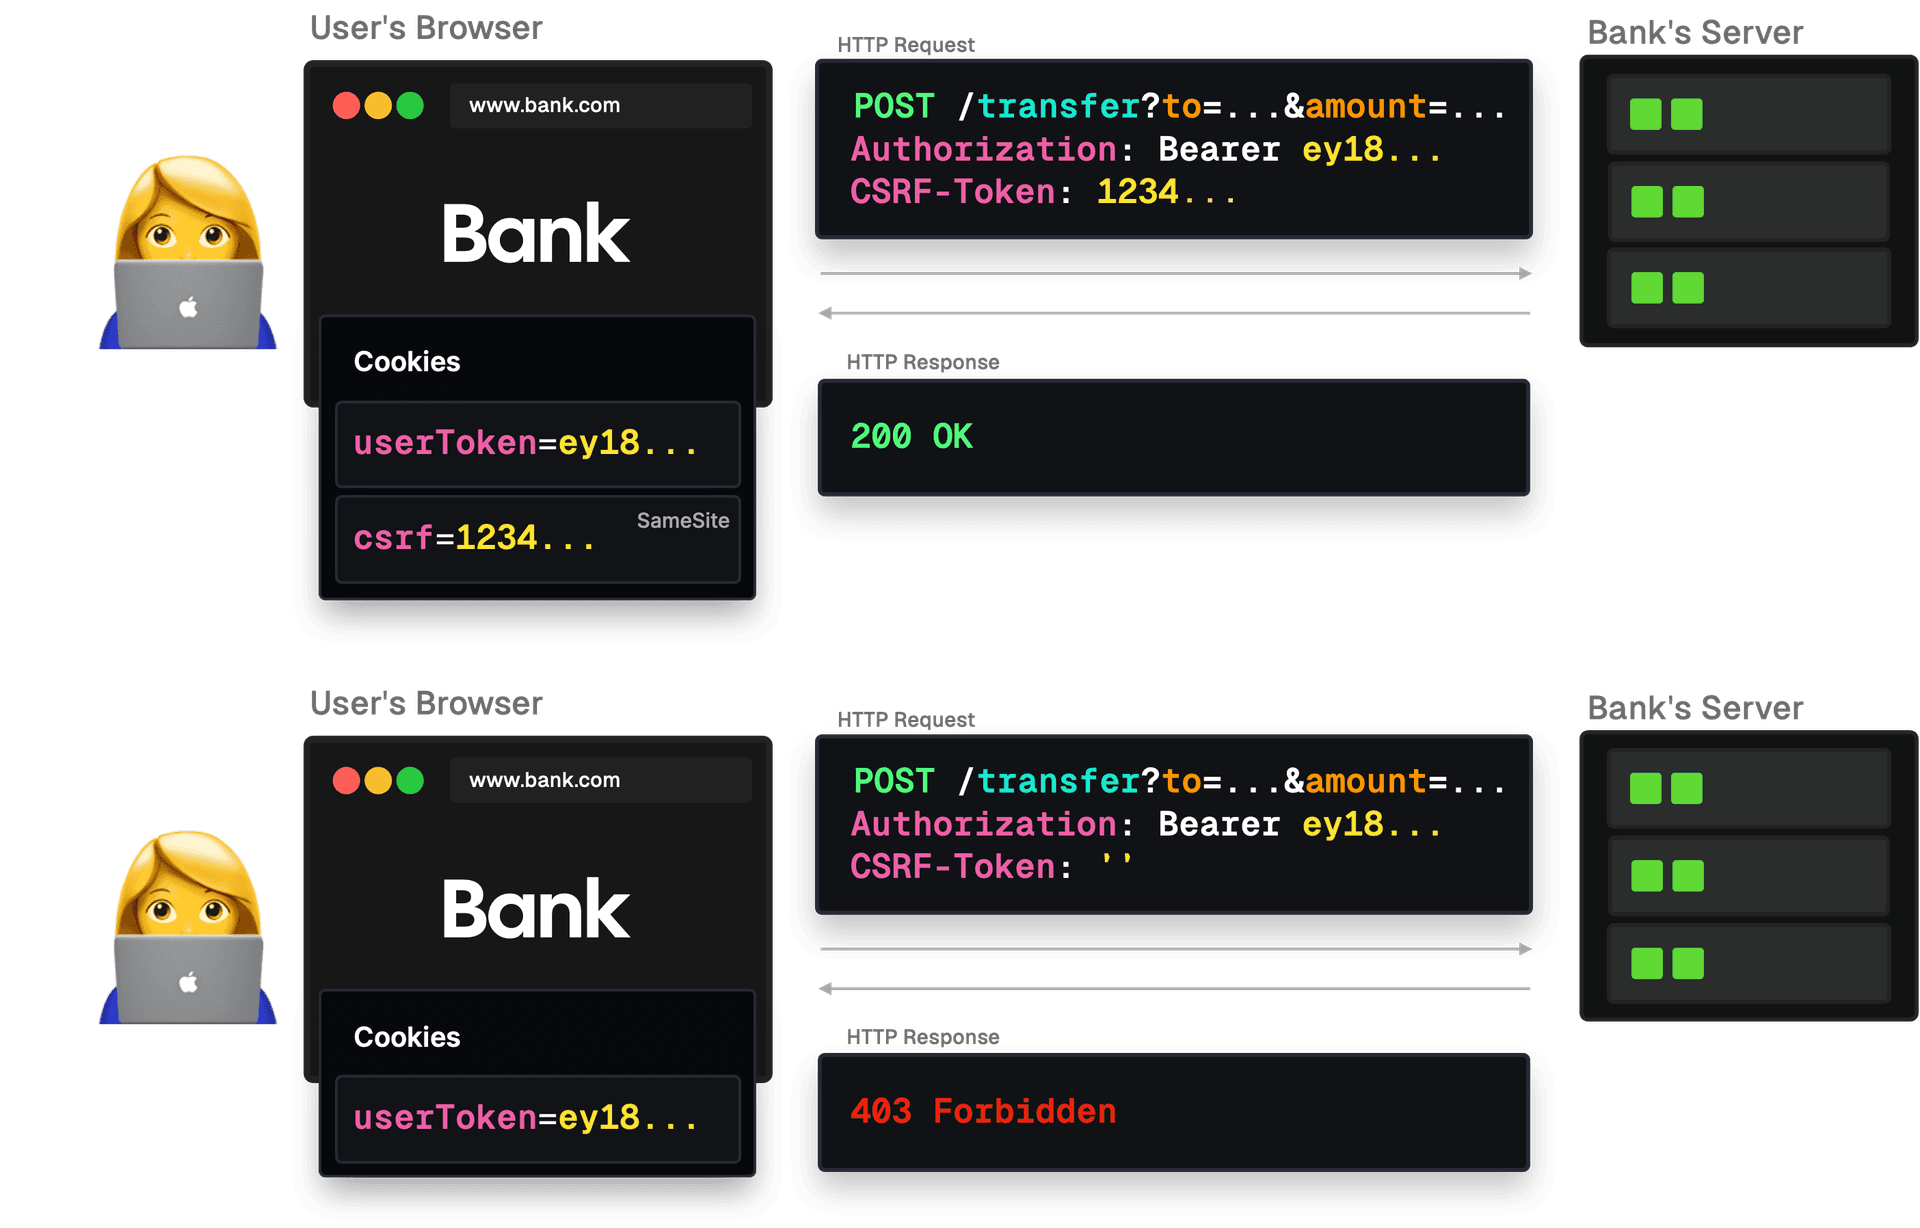
Understand the mechanics and risks of Cross-Site Request Forgery (CSRF) attacks, and discover crucial development practices.
Cross-Site Request Forgery (CSRF) is an attack that tricks users into executing unwanted actions on a web application where they're currently authenticated.
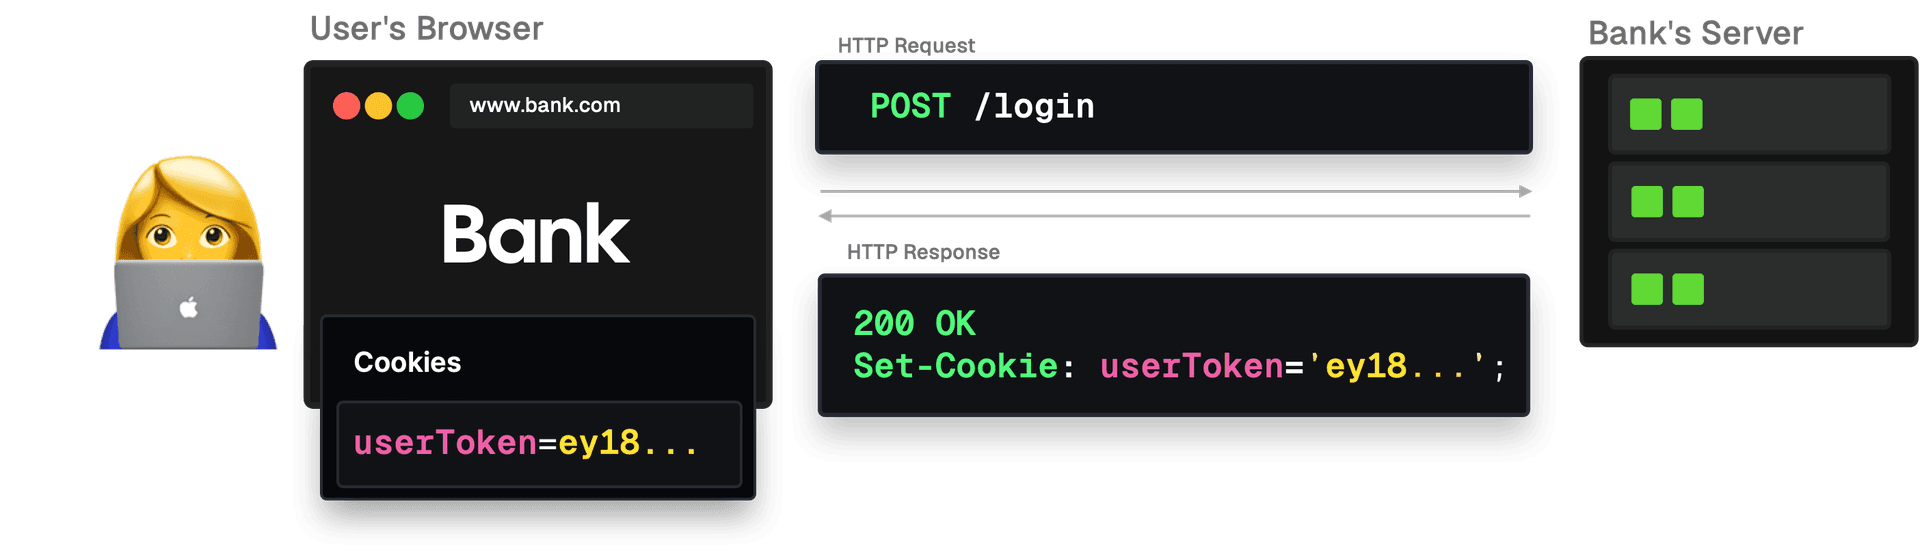
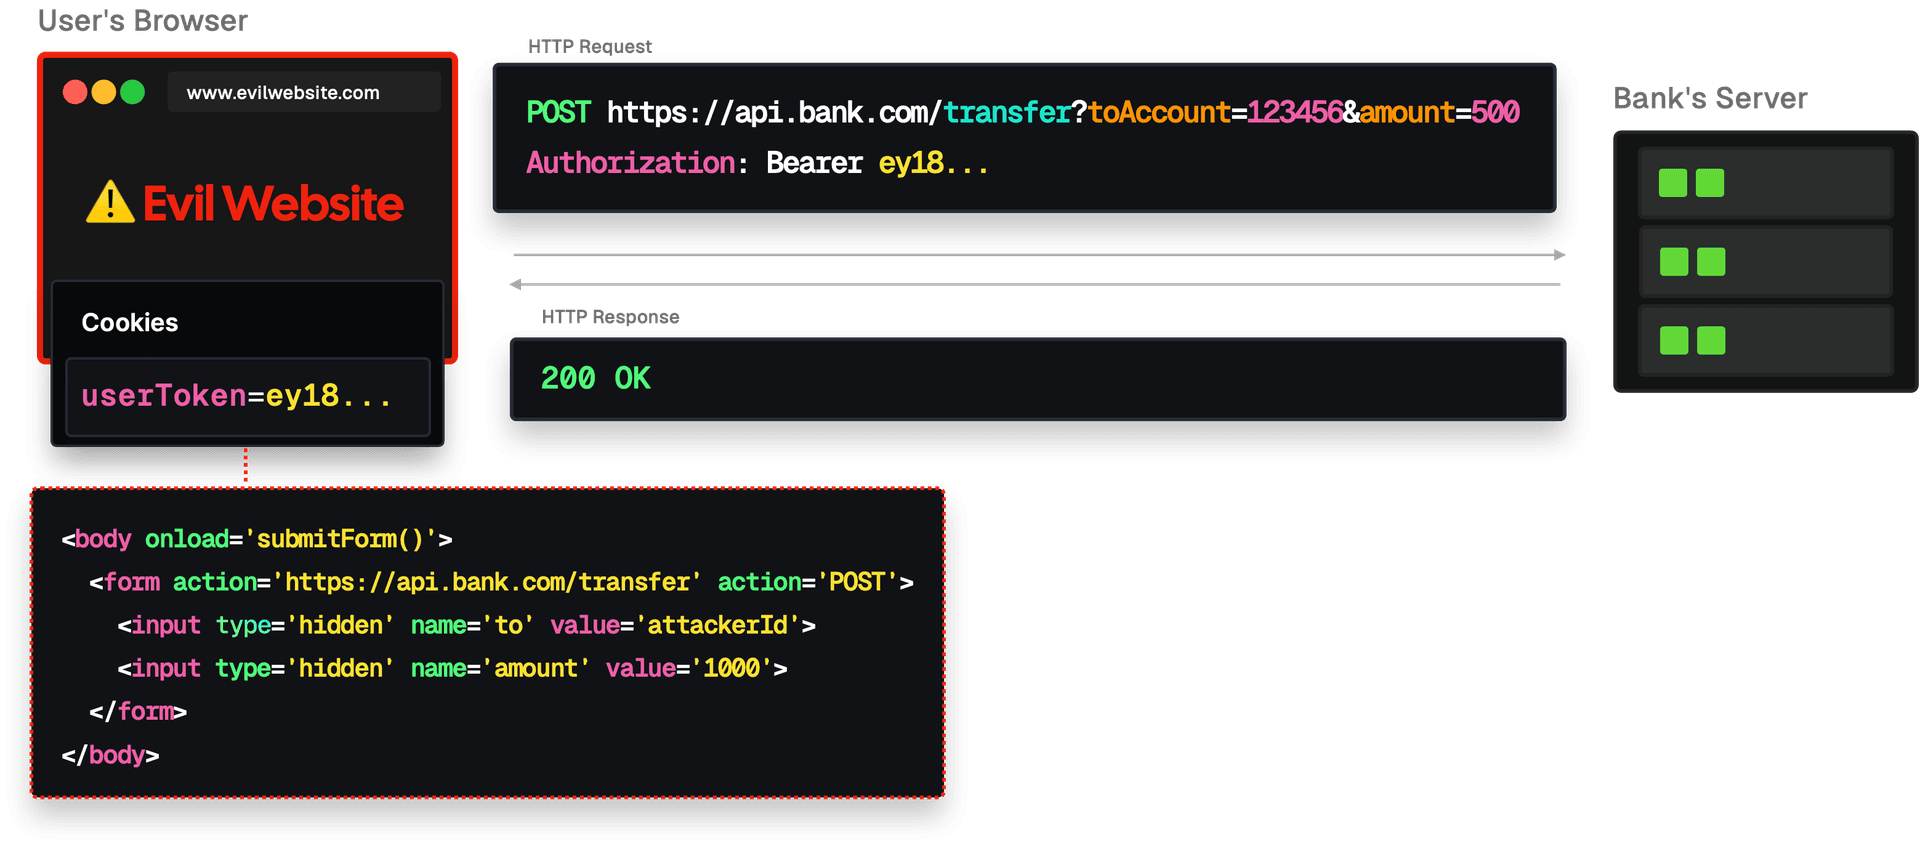
Imagine you're logged into your online banking platform. In another tab, you click on a seemingly harmless link. The next thing you know, money has been transferred out of your account without your knowledge. Oh no, you've just fallen victim to a CSRF attack! But how could this happen?
CSRF attacks occur in a few steps:
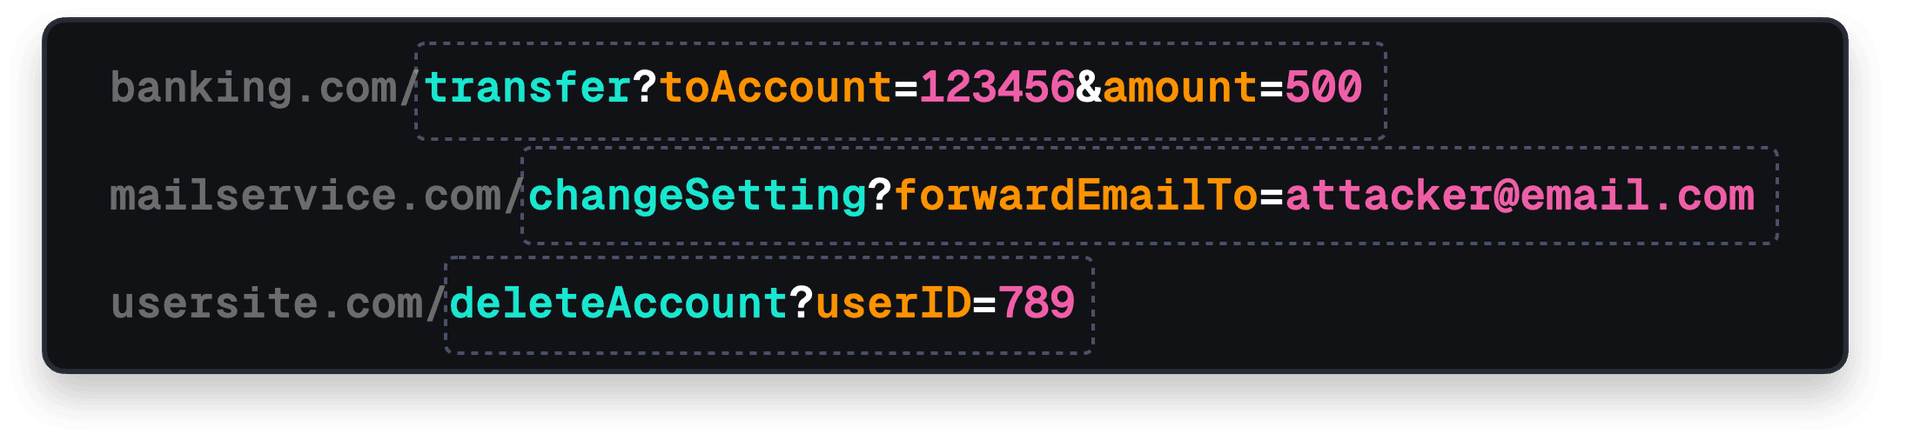
1. The attacker identifies a target site that is vulnerable to CSRF. Typically, this is a site where important actions occur through predictable URLs or requests.
2. The attacker creates a malicious request . For this demo, let's assume our bank's website transfers money using a simple URL like bank.com/transfer?amount=1000&toAccount=attackerAccountId .…