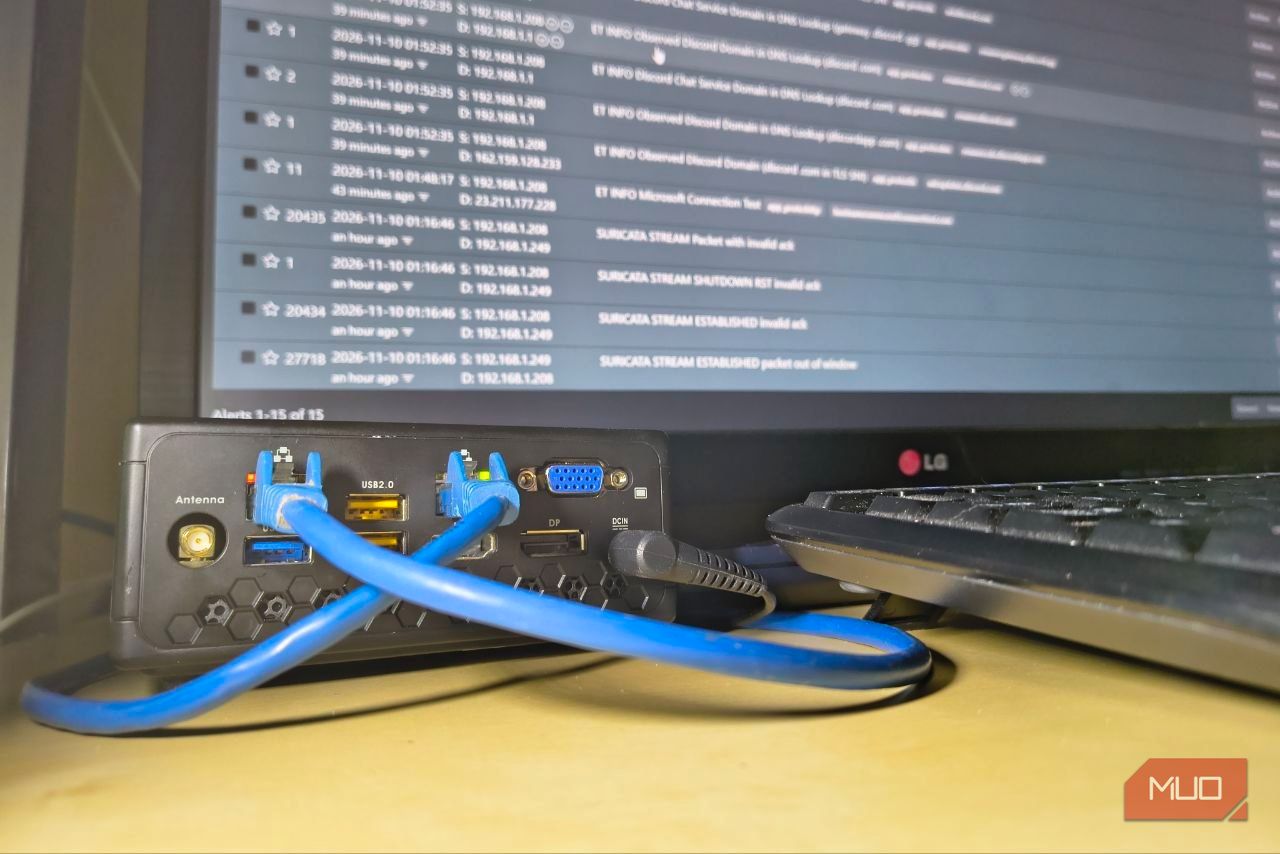
I built a DIY intrusion detection system (IDS) using a Zotac Nano mini PC with dual Ethernet ports. With my Windows laptop plugged into one NIC and the switch plugged into the other, the mini IDS could watch every single packet that came down the wire.
All I really needed was someone willing to do something suspicious, and thankfully I had a VM handy to do precisely that.
From a Linux box on the other side of the switch, I used Nmap to probe for 100 ports on my laptop. In under two seconds, it found four open ports. When I refreshed my IDS logs expecting to see the carnage, there wasn’t even a single new alert.
So, why didn’t the IDS see me?
I put the mini-IDS between my laptop and the switch
One wired client and two Ethernet ports
My cheap and, let’s face it, mediocre mini PC has a Celeron N3160 and 8 GB of RAM.…