Serving tech enthusiasts for over 25 years.
TechSpot means tech analysis and advice you can trust .
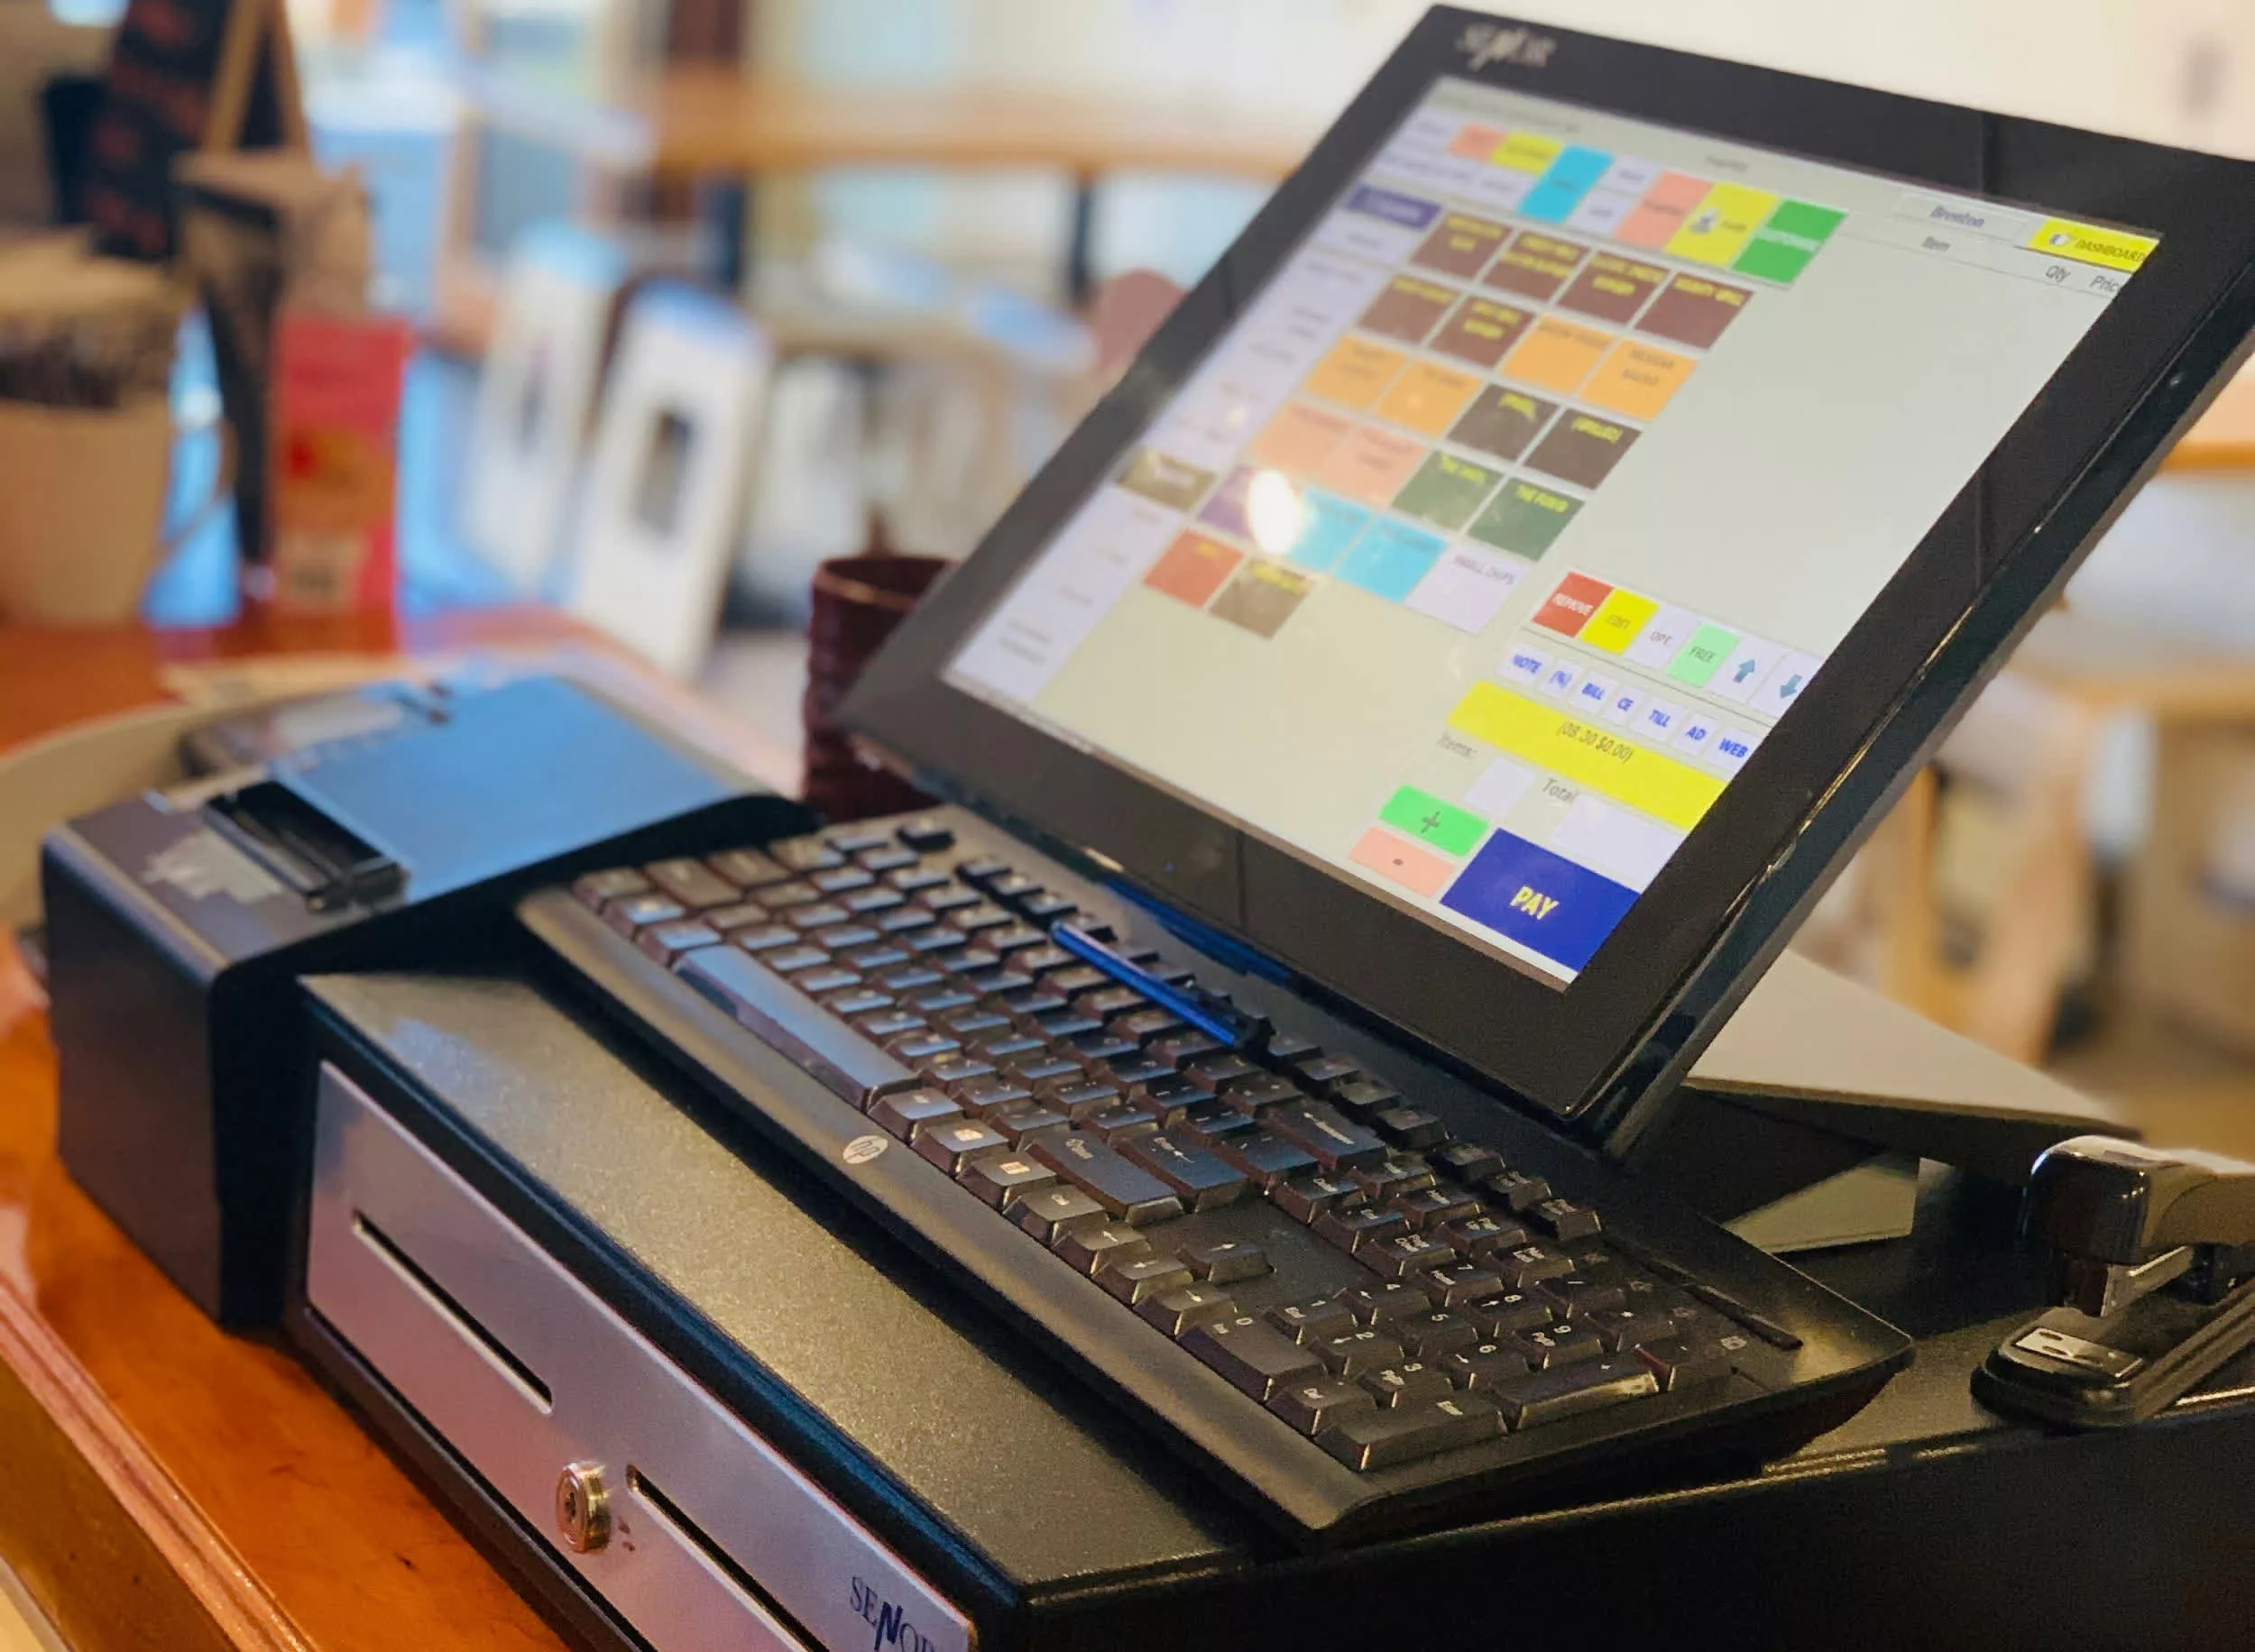
Facepalm: Security researchers recently discovered a peculiar cybersecurity incident involving POS systems using outdated Microsoft software. The operation relied on an old Windows bug and repurposed publicly available proof-of-concept exploit code, significantly increasing the risk of financial fraud for a large number of unsuspecting cardholders.
Unknown cybercriminals spent months or even years harvesting critical data about millions of credit card transactions on point-of-sale (POS) systems. The operation was eventually discovered because the crew left a server exposed to public access. After breaking in, security researchers found a massive trove of revealing data, including malware source code and details about how the operation came about.
The main culprit behind the malicious operation was a security vulnerability affecting several versions of Windows 10, 11, and Windows Server.…