This research was presented at DEF CON 34 in Las Vegas, Nevada. The vulnerability was fixed in SentinelOne Agent Version: 26.1.1.
Key takeaways
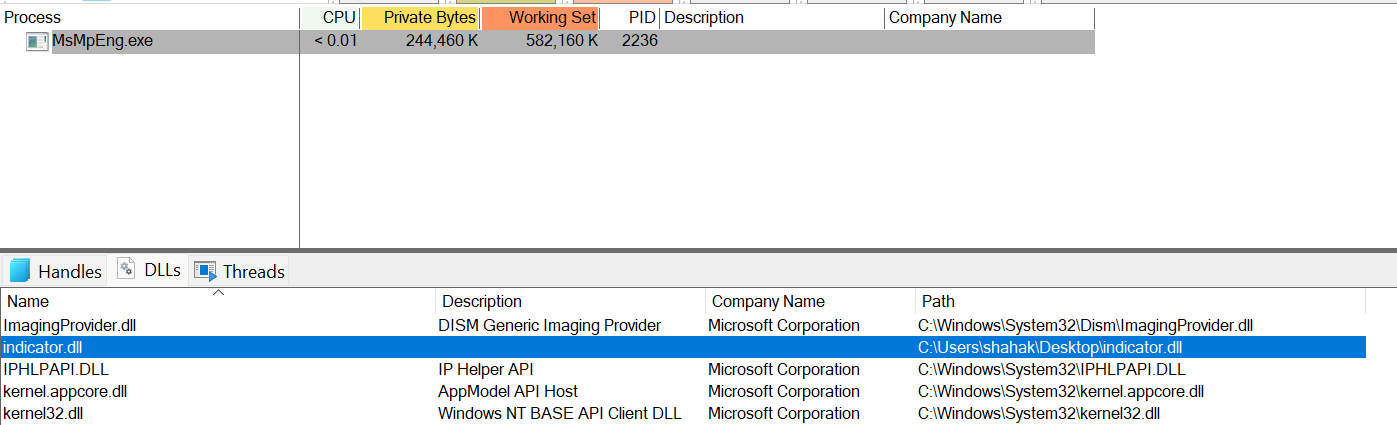
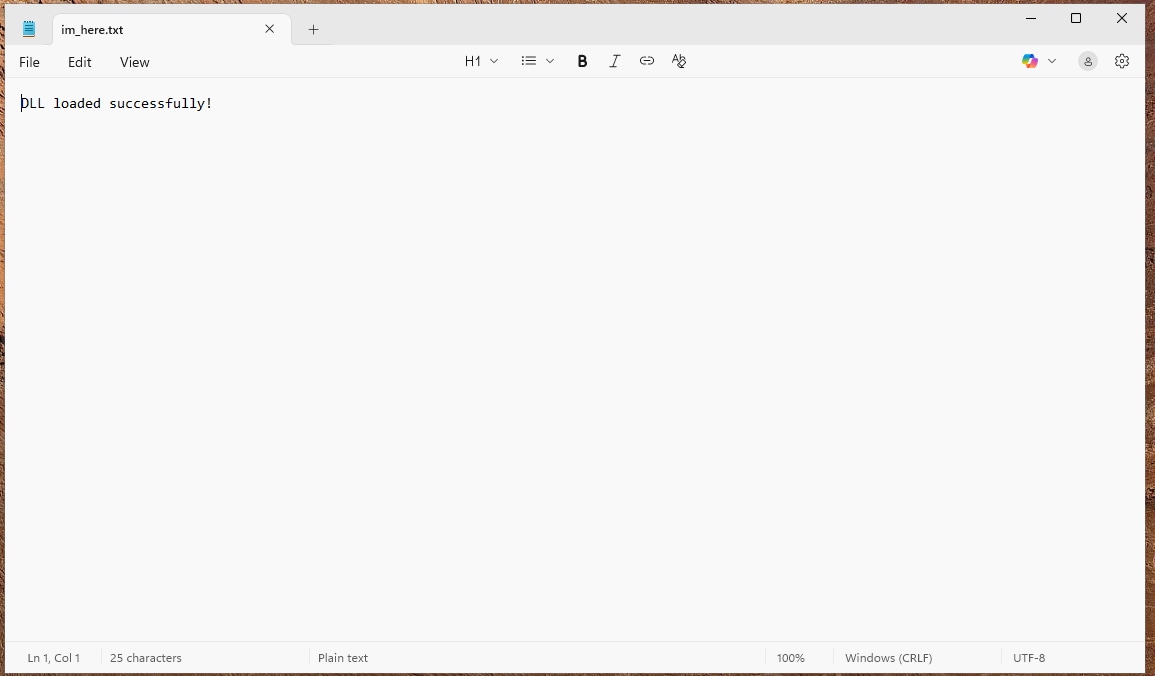
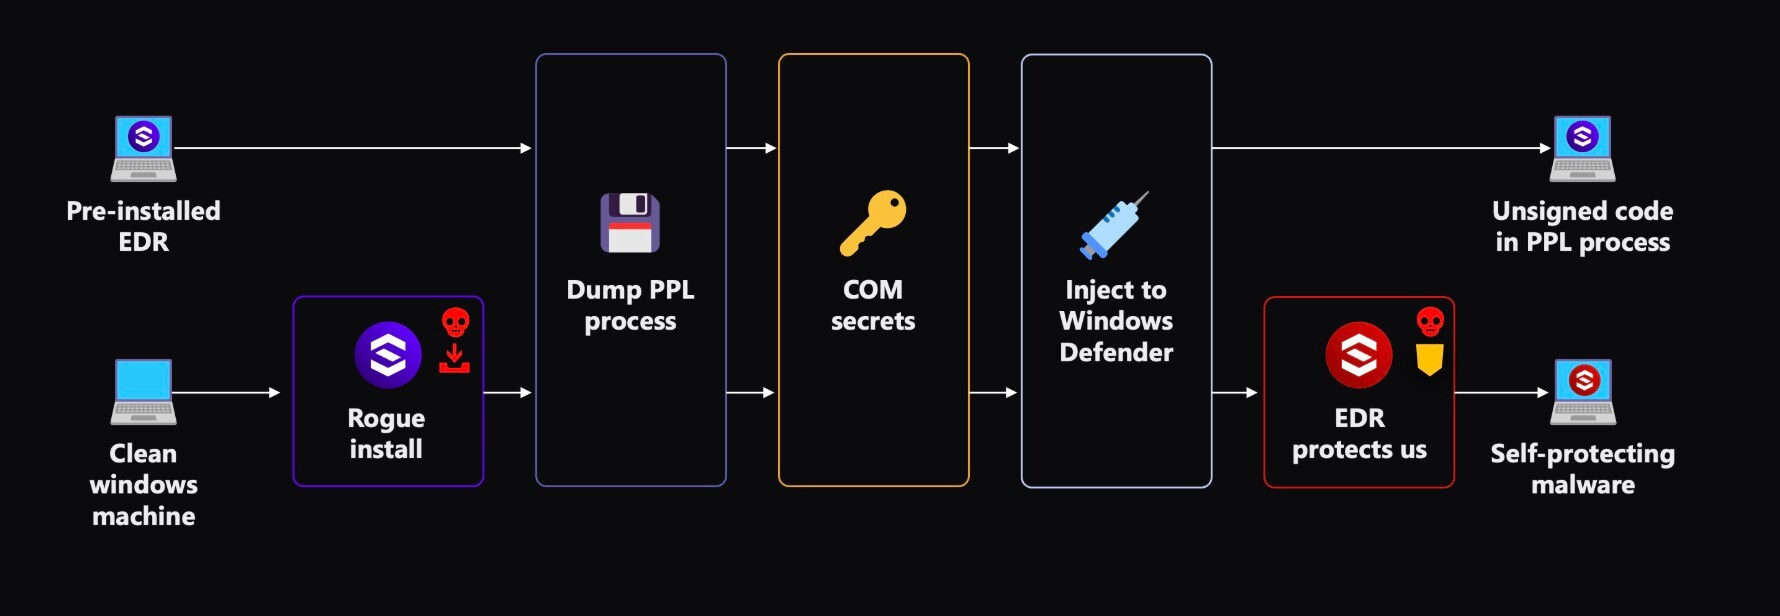
Legitimate SentinelOne installers and accessible COM interfaces can be abused to bypass Protected Process Light (PPL) protections and execute unsigned code — completely bypassing the need for kernel vulnerabilities or traditional exploits.
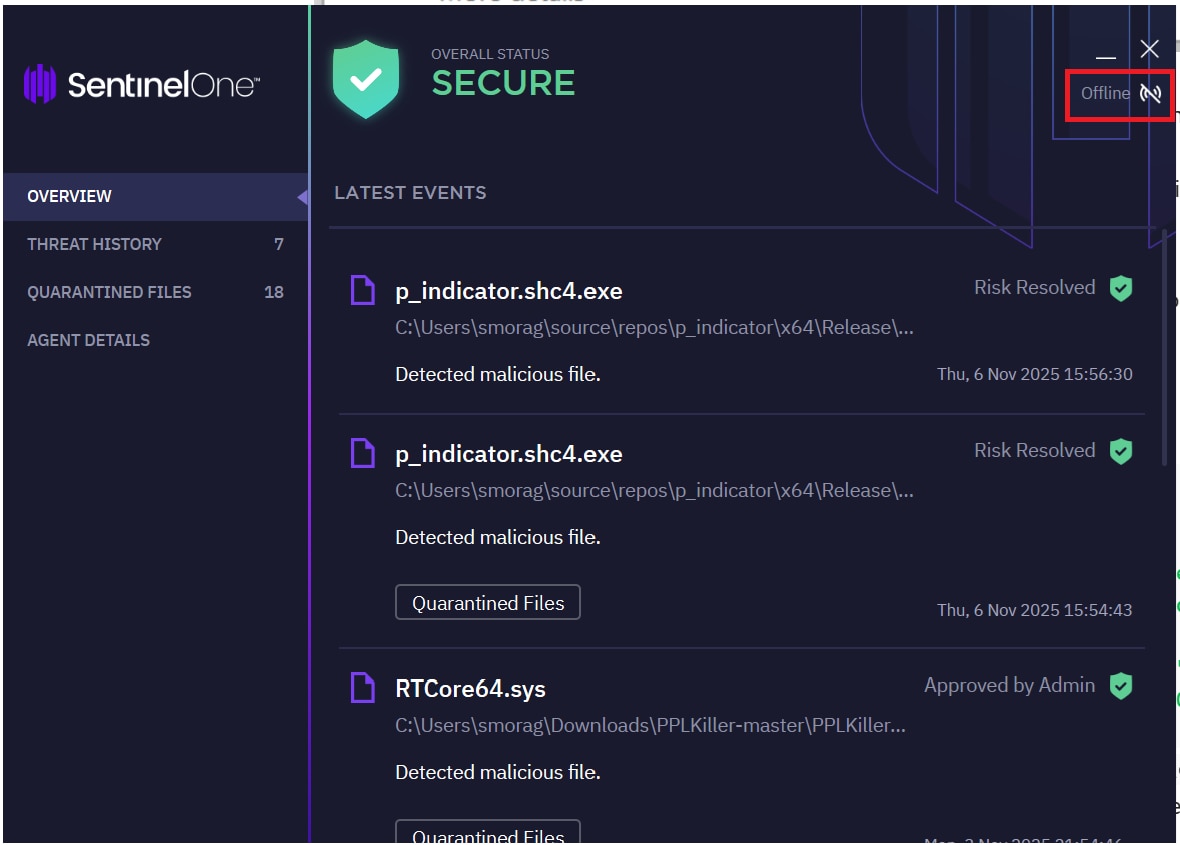
Management communications rely on user-configurable mechanisms like local DNS lookups, which allow an administrator to easily isolate the agent and block remote telemetry.
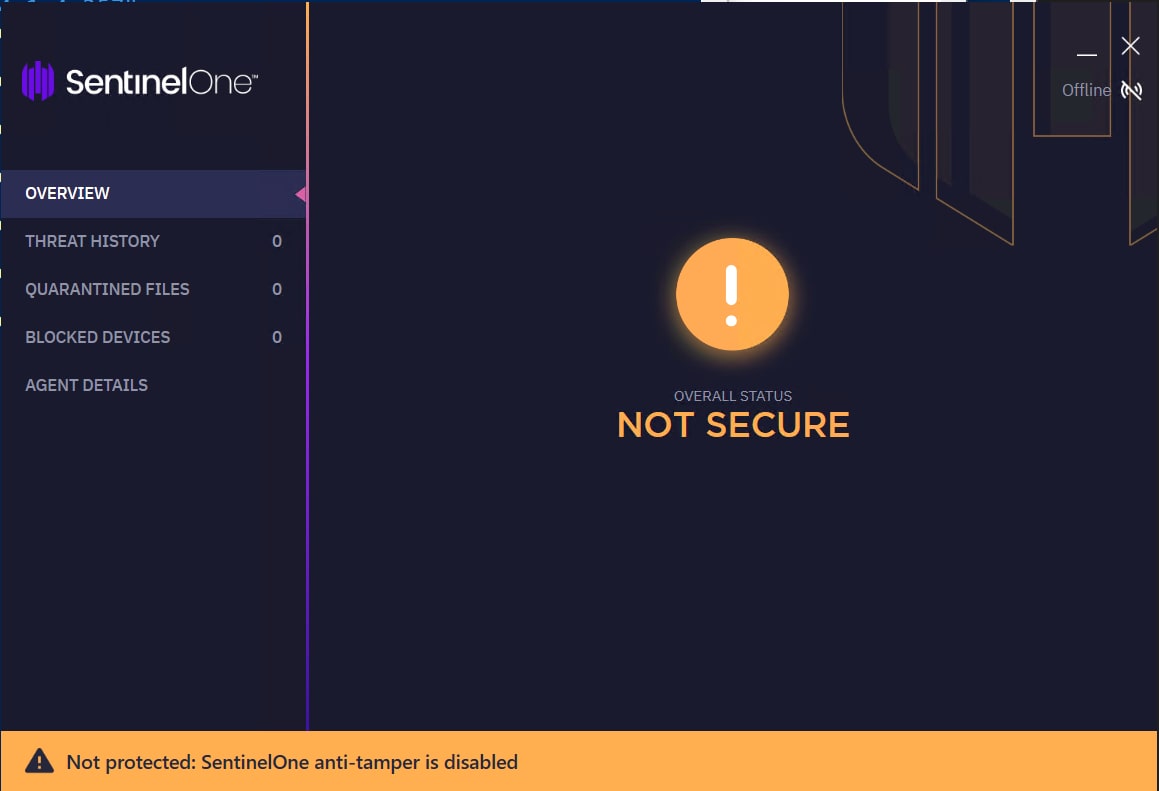
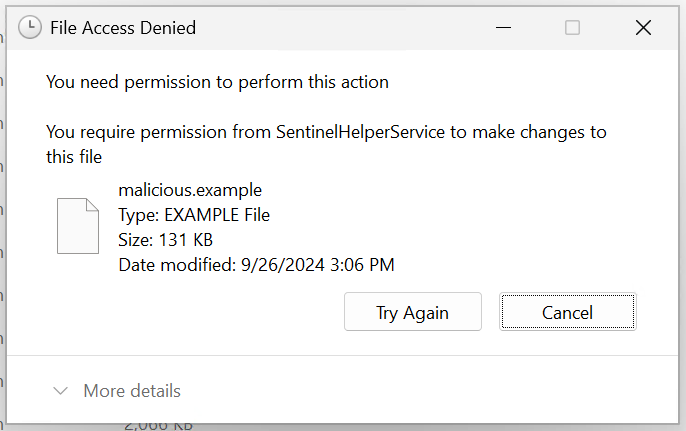
Built-in self-defense mechanisms can be inverted against the host system, rendering files inaccessible and processes untouchable.
Trusted endpoint detection and response (EDR) software can become a high-impact Trojan horse when local privilege escalation vectors and local trust assumptions are not properly hardened.
Endpoint detection and response (EDR) is one of the main defense layers in an enterprise organization and one of the first hurdles that a…