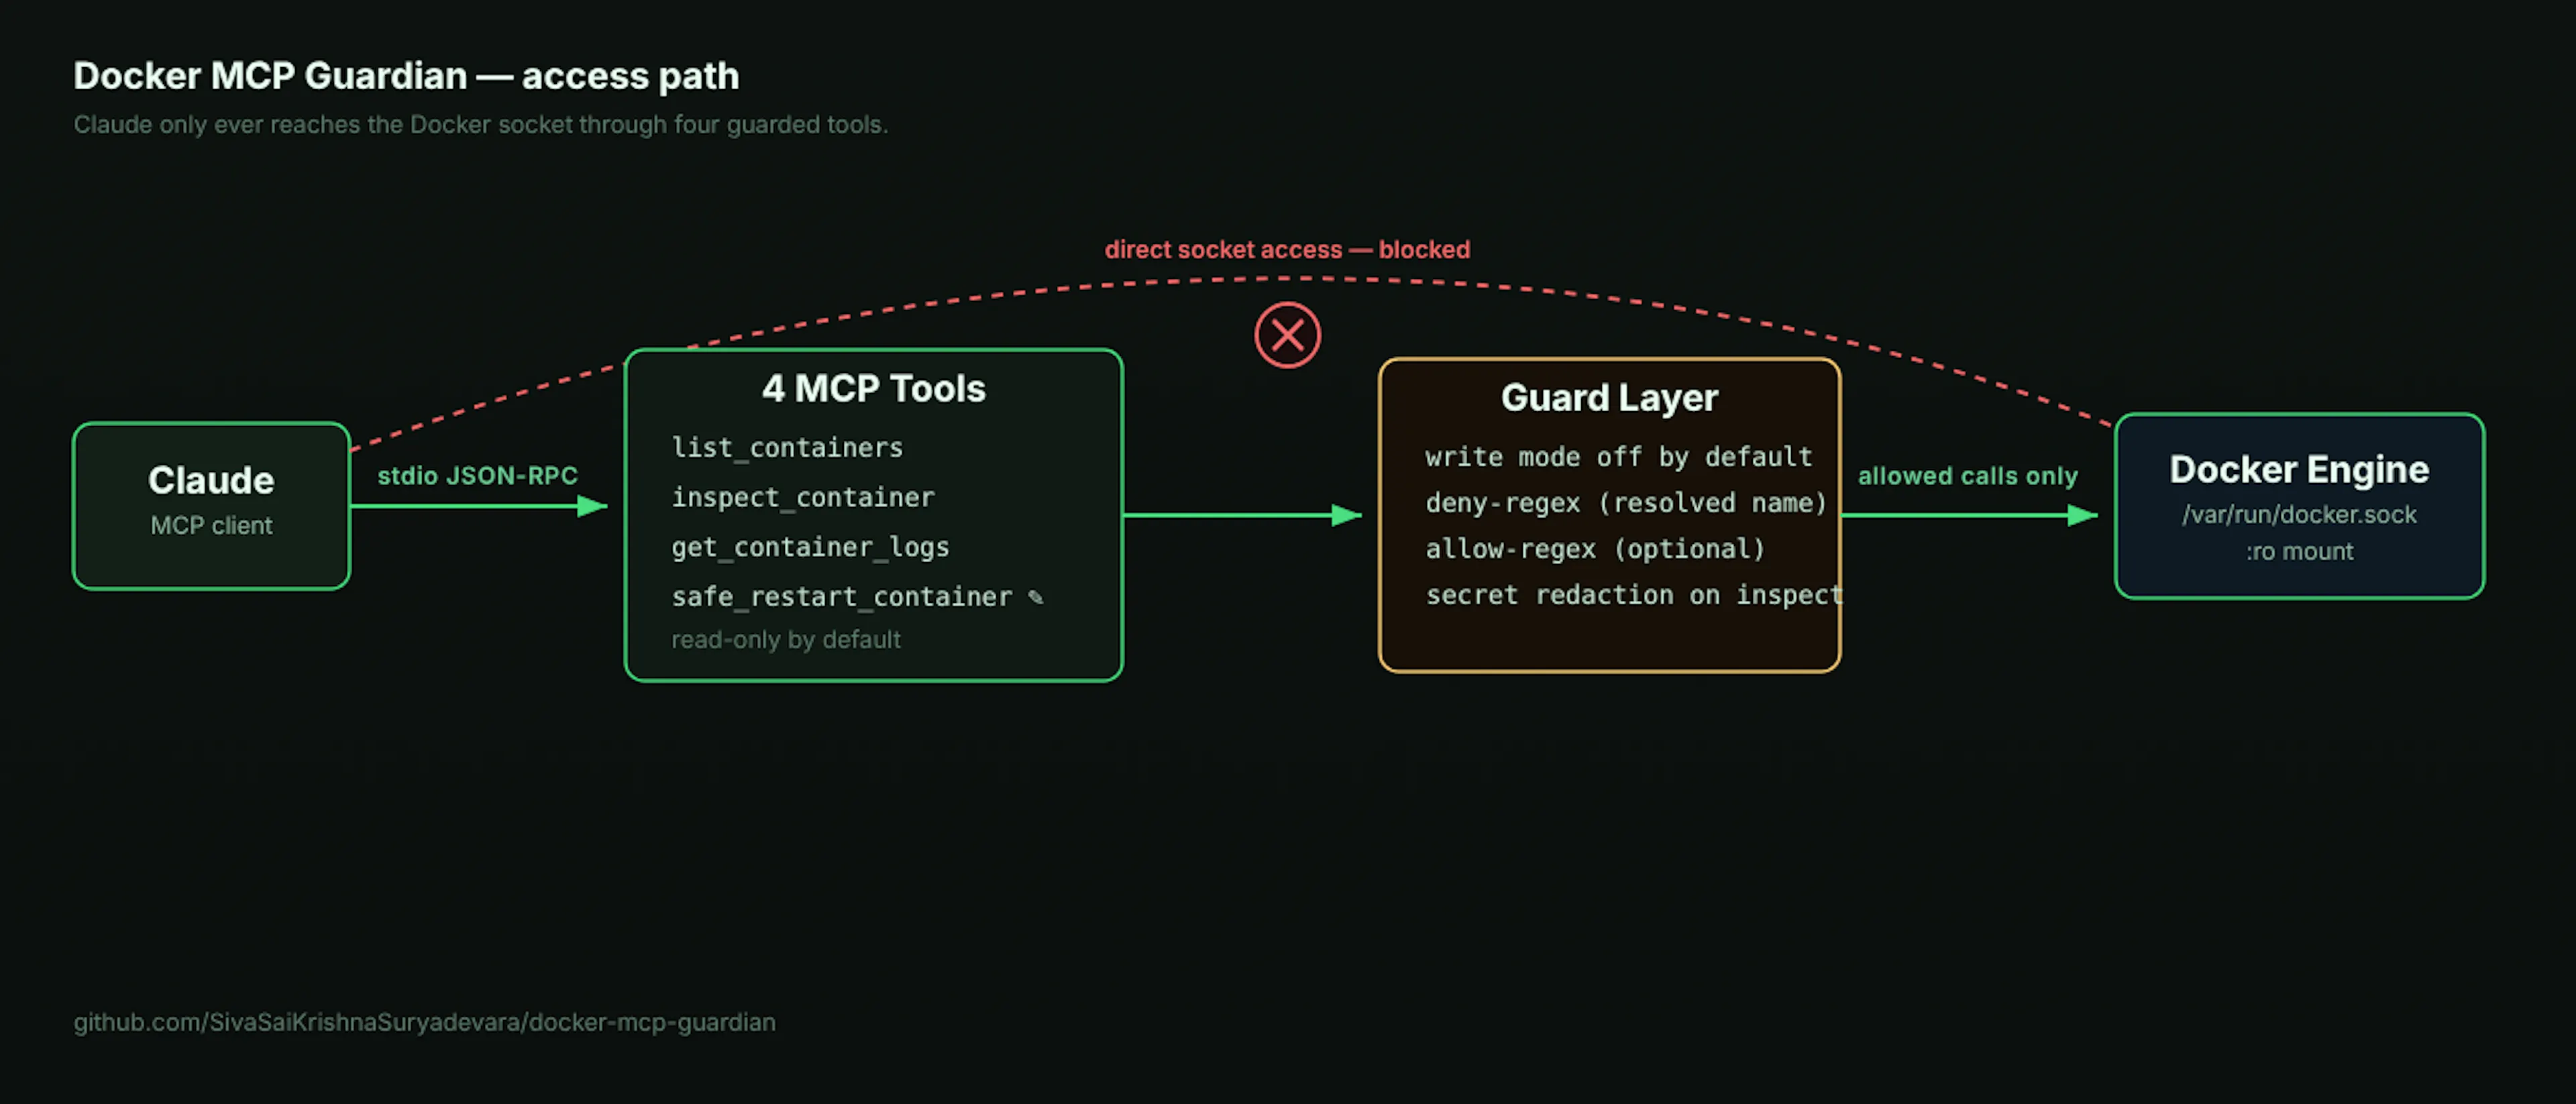
Source Code & Test Harness: The complete, tested codebase for this implementation is available on GitHub at SivaSaiKrishnaSuryadevara/docker-mcp-guardian .
Here is a line I keep finding in Docker MCP server setups:
volumes: - /var/run/docker.sock:/var/run/docker.sock:ro
The :ro reads like a safety guarantee. It isn't one. A read-only bind mount stops the container from replacing or deleting the socket file . It does nothing to the bytes you send through it. Once a process can connect() to that Unix socket, it is talking HTTP to the Docker Engine API, and the engine will happily accept POST /containers/{id}/restart , POST /containers/create , or DELETE /containers/{id} over a "read-only" mount.
Now hand that socket to an LLM agent through an MCP server, and the only thing standing between "summarize why my API container keeps crashing" and "restart the production database" is whatever checks you wrote in the tool layer.
I'm a platform engineer, and I wanted Claude to be able to look at my containers…