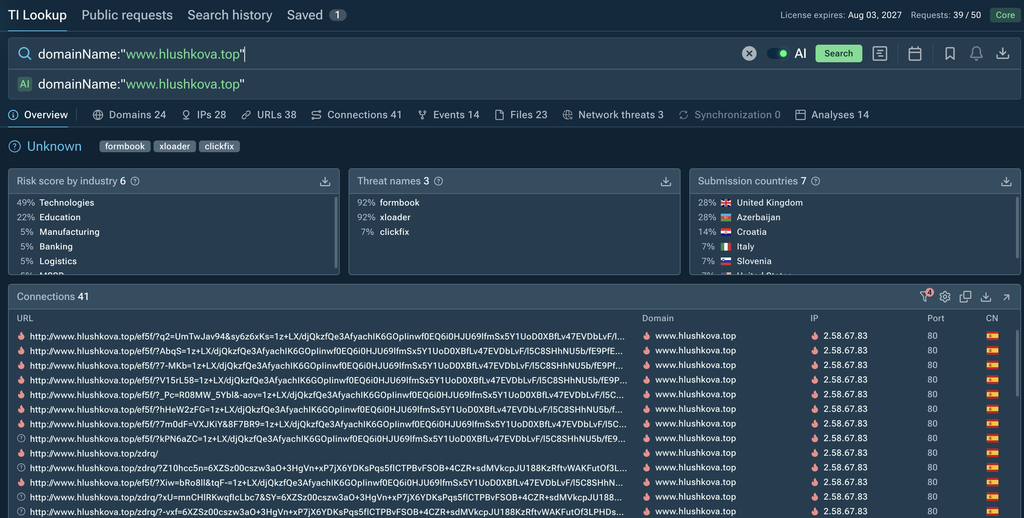
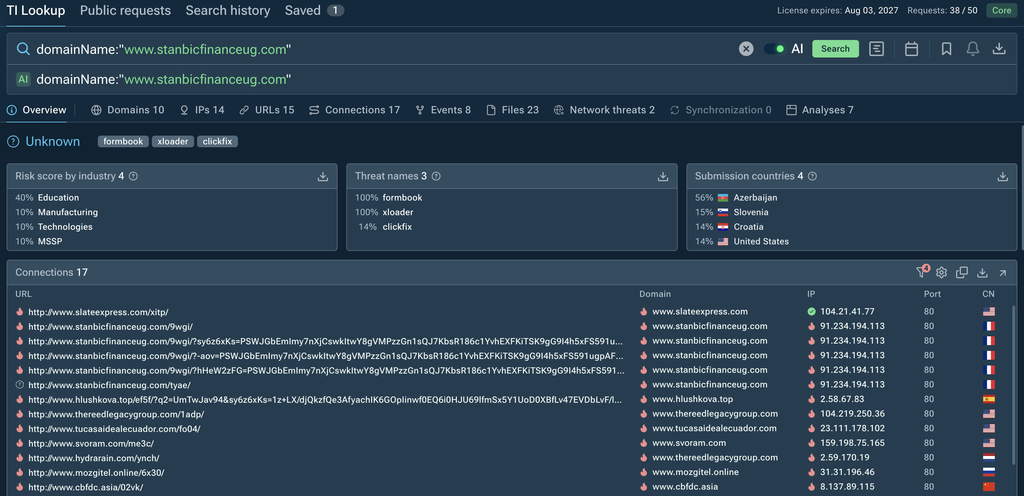
European businesses, particularly in the UK and Italy, face malware campaigns that exploit routine business correspondence. A recent Formbook (now also known as XLoader) campaign uses localized order and procurement lures to deliver an information stealer.
Manufacturing and technology companies are especially exposed because employees regularly handle purchase orders, supplier documents, and payment requests. A seemingly routine attachment can hide a JavaScript loader that ultimately deploys malware to steal browser-stored credentials.
The ANY.RUN team investigated the campaign, uncovering its infection chain, persistence methods, and links to other malware activity. These findings show how behavioral analysis and threat intelligence can help organizations strengthen their defenses.
Key Takeaways
Localized order lures target European businesses.…