2026-09-07
… from the 90s.
I’ve been thinking about the security of RSA lately. RSA’s cryptography relies on the difficulty of factoring a large semiprime number, but what “large” means is an interesting question. The Web PKI deprecated 1024-bit RSA over a decade ago, and while I don’t know of anyone factoring a key of that size, it’s within the realm of possibility for a government or other organization with a large number of computers. Just a few days ago, someone factored the 862-bit RSA-260 key from the RSA factoring challenge. That’s the largest factorization I’m aware of. Today, the world uses RSA of at least 2048 bits, but even that will be deprecated soon with the risk of quantum computers in the future.
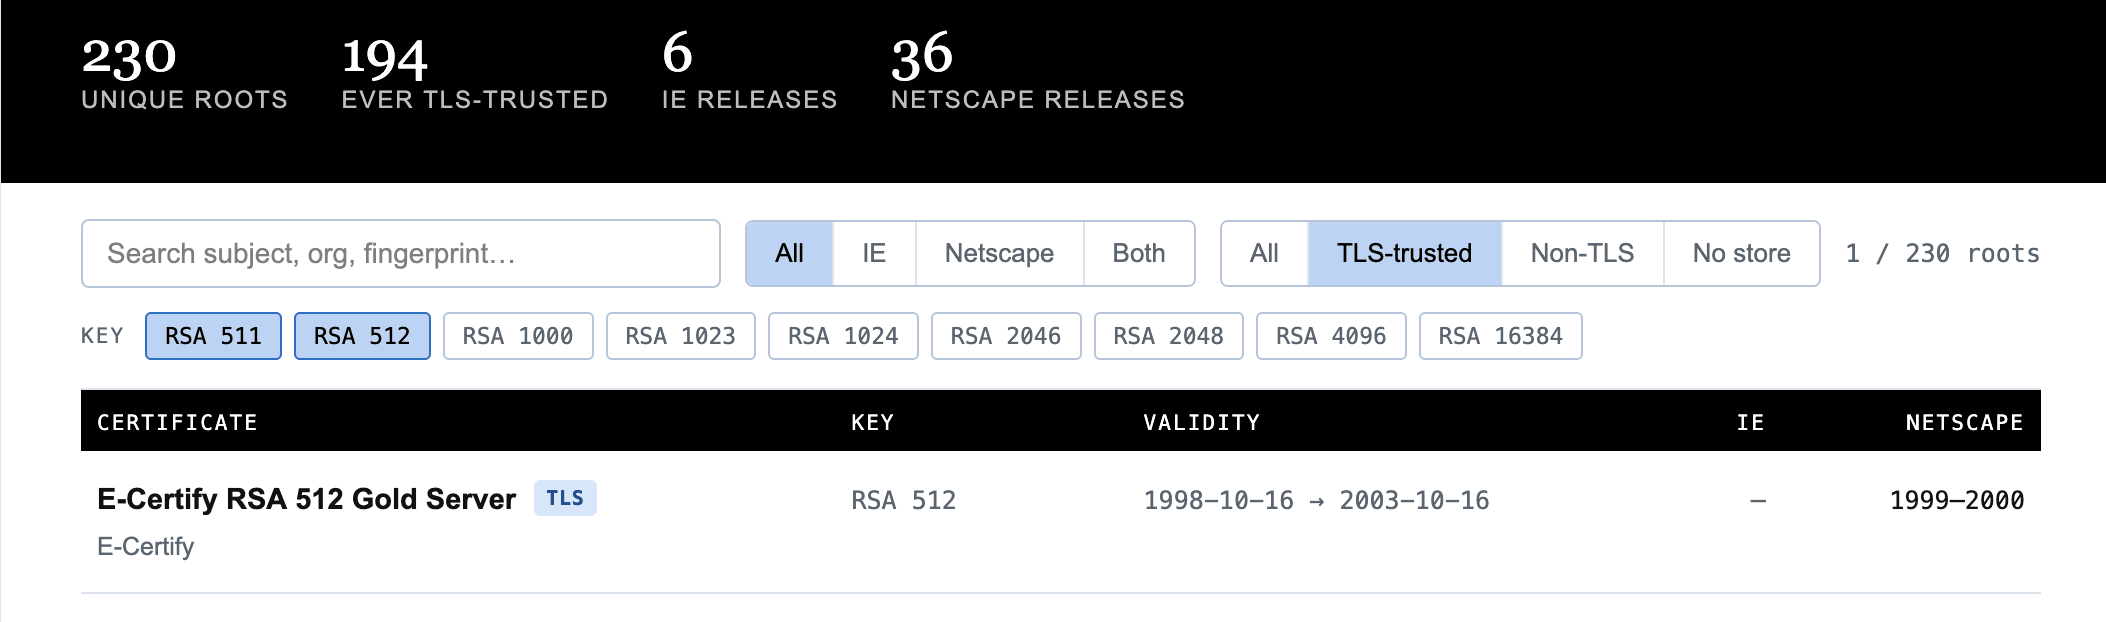
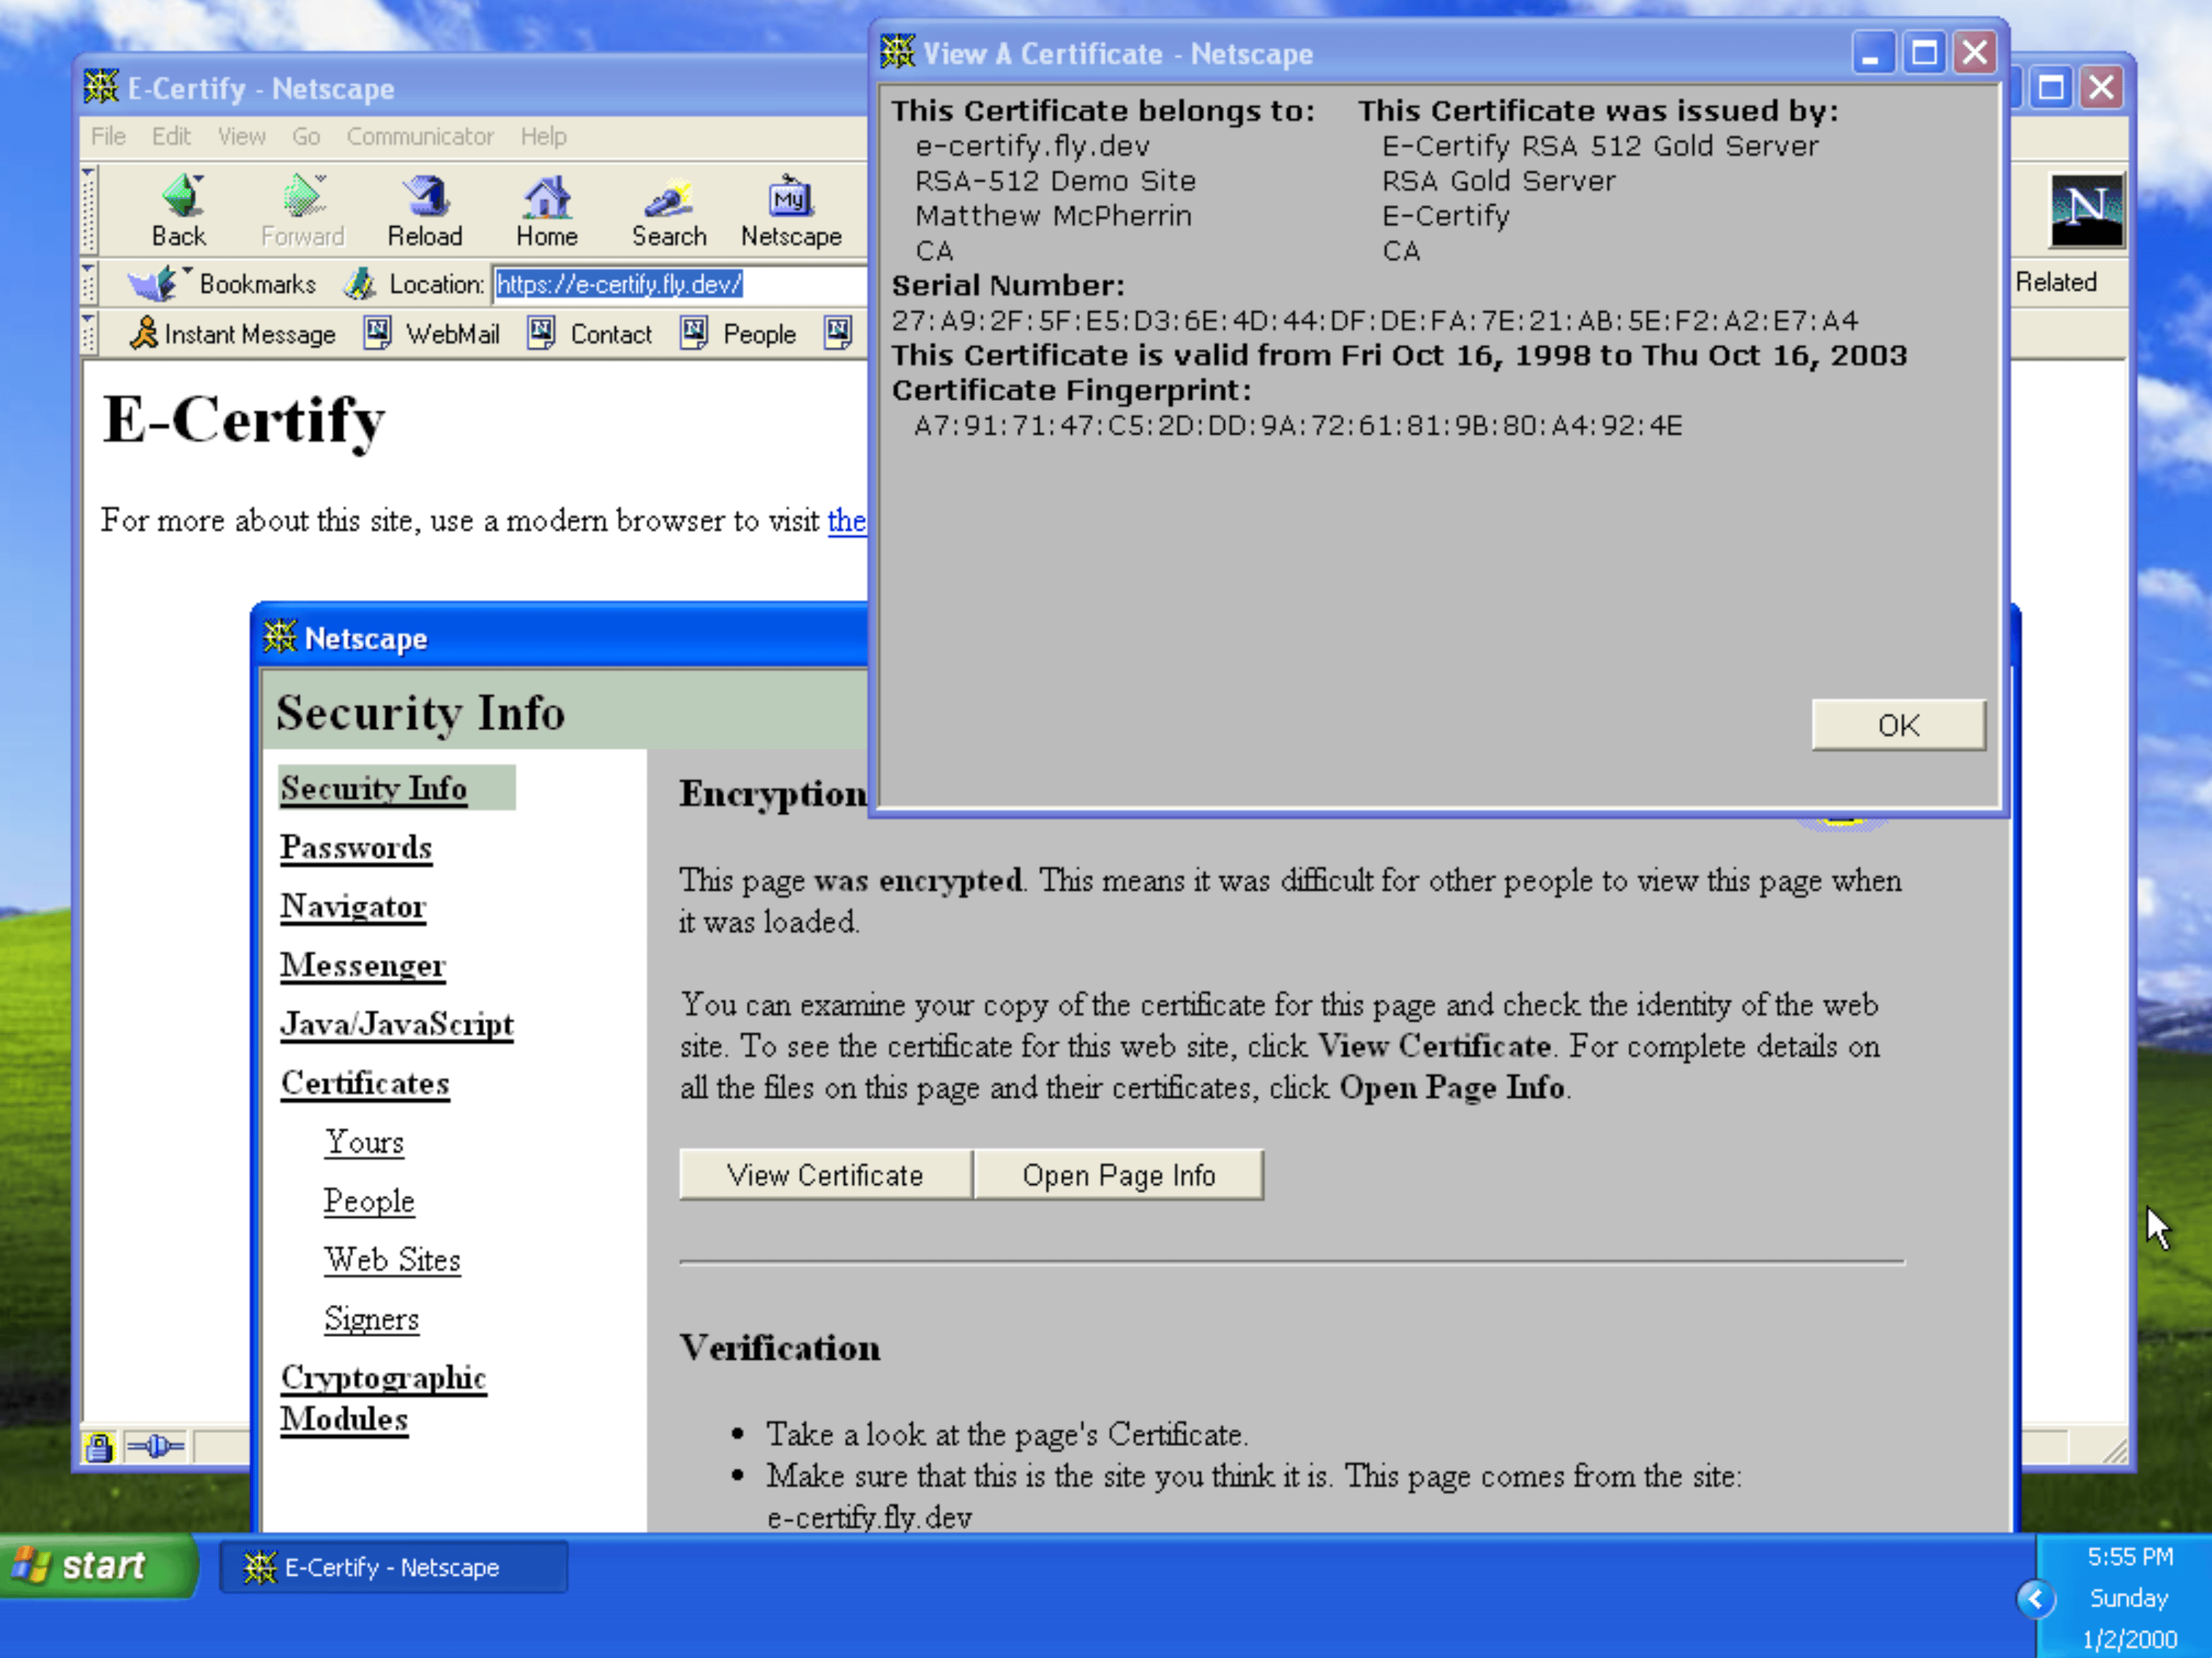
This led me to wonder: small RSA keys can be factored on even a modest desktop computer. And in the early days of the Web PKI, there were no standards, and no minimum requirements. Netscape shipped SSL support in 1994, and IE shortly afterwards.…