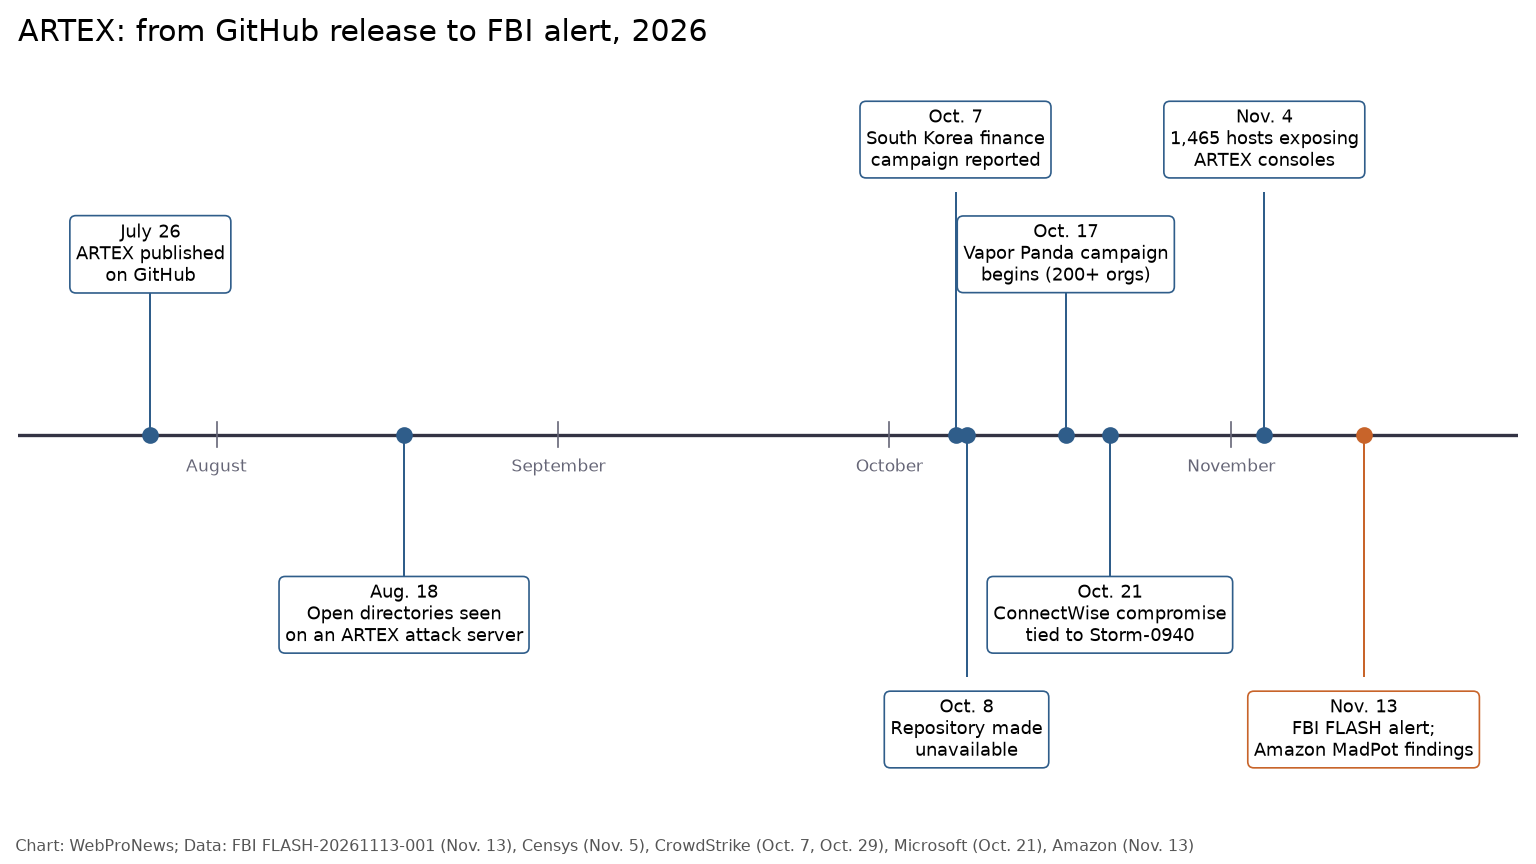
The FBI wants companies to look hardest at the systems they watch least. In a FLASH alert released Friday, the bureau said threat actors have turned ARTEX, an open-source AI agent framework built for penetration testing, into a way to “automate multiple phases of cyber intrusions at machine speed, from reconnaissance through data exfiltration.” It singled out partner and supplier portals, mobile backends, sales-support systems, legacy services and third-party integrations as the places the tool excels at breaking into.
Some ARTEX-driven intrusions went from initial targeting to privileged access in under three hours, the FBI said. A variety of malicious actors have used the framework since at least August against organizations in financial services, government, technology, defense, semiconductors, energy, healthcare, manufacturing, telecommunications and legal.…