Smashing the botnet
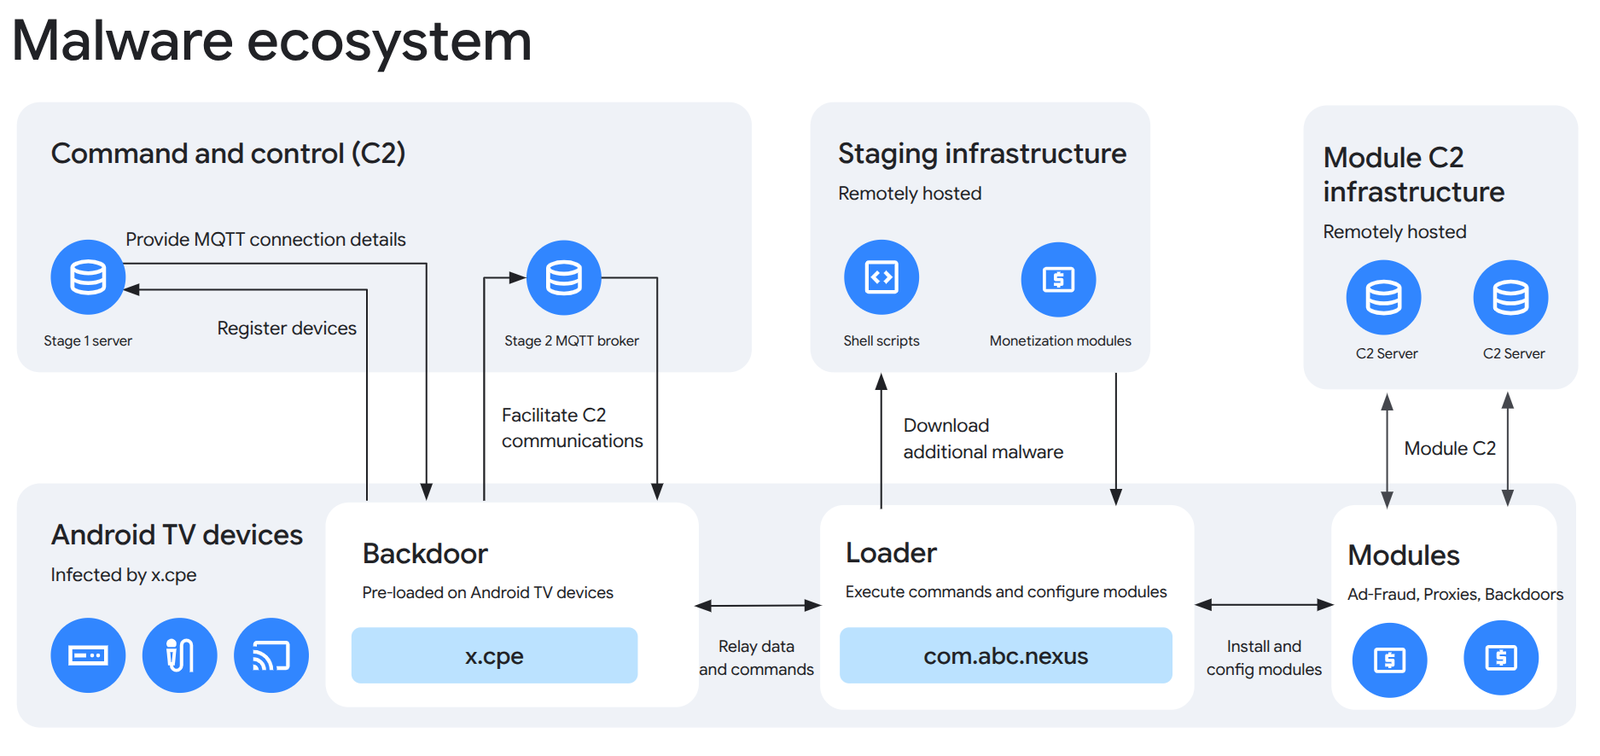
Google worked with several other organizations to disrupt the x.cpe network, including Japan’s National Police Agency, Synthient, and Trend Micro. Google says it has taken legal action to shut down the domains and servers Videostrong used to operate and install its malware. It also went after command-and-control servers operated by Videostrong that were connected to other malware campaigns. Google estimates Videostrong has been cut off from about 10 million compromised devices.
This action should make the affected devices safe to use, but probably not as safe as they should be. Play Protect is still disabled, and the inert malware modules are still installed. Since they are loaded as system apps, users cannot easily remove them.
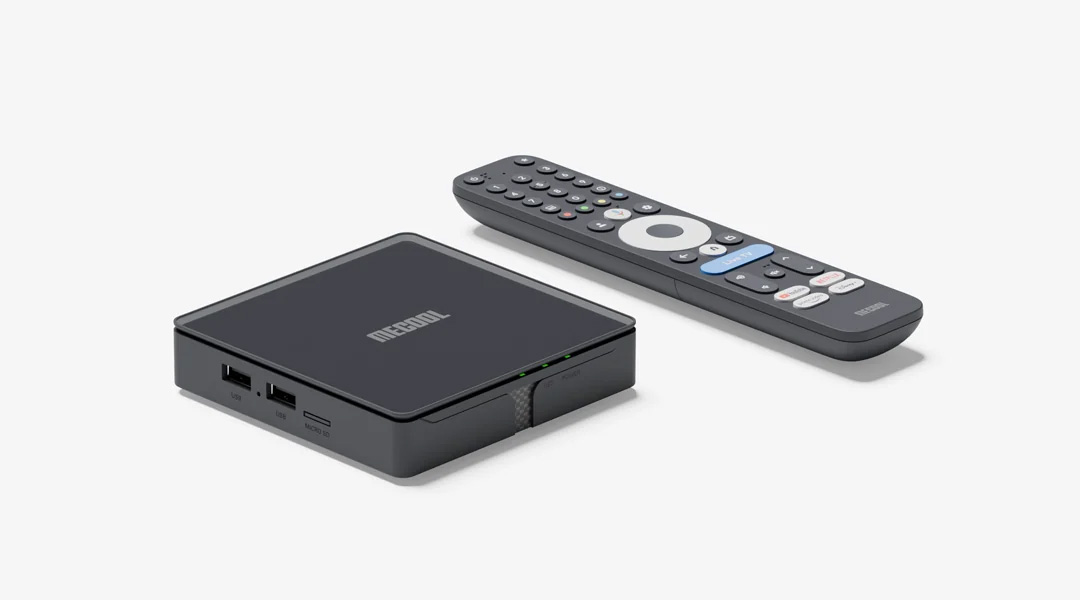
Synthient has published a list of 182 device model names known to be included in the botnet. Anyone who has purchased a MECOOL or white label Android TV box of unknown origin should check it.…